 www.thedefensenews.com
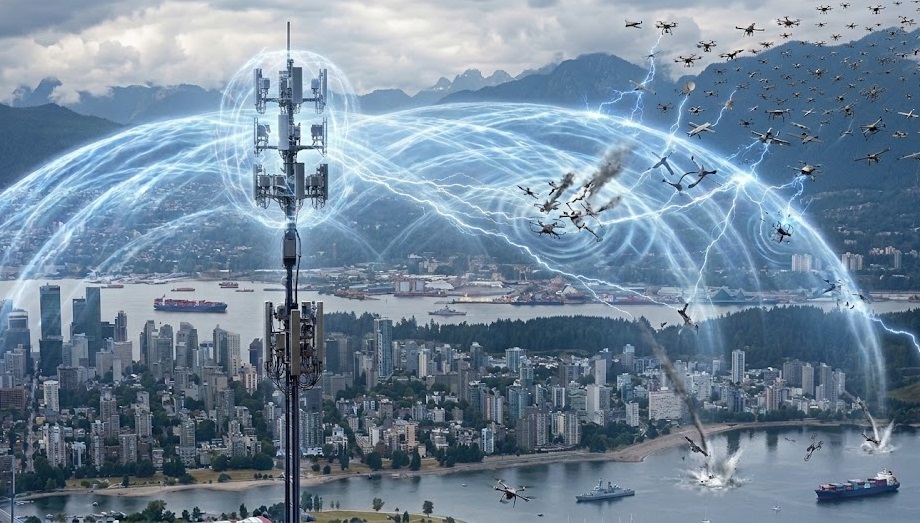
IAI Launches HYPNOSIS to Counter Drone Swarms via GPS Disruption
Article Content

- •HYPNOSIS disrupts GNSS signals to neutralize drone threats without kinetic force.
- •The system is designed to operate autonomously, enhancing response speed against multiple threats.
- •IAI aims to reduce the high costs associated with traditional missile defense systems.
Israel Aerospace Industries (IAI) unveiled HYPNOSIS, a new electronic warfare system designed to neutralize drone swarms by disrupting their GNSS signals rather than using kinetic interceptors. This system targets the GPS, GLONASS, BeiDou, and Galileo signals that drones rely on for navigation, effectively rendering them unable to reach their targets. The introduction of HYPNOSIS comes as military planners express growing concerns over the threat posed by large-scale drone attacks, which can overwhelm traditional air defense systems. By employing a network of mobile jamming and spoofing stations, HYPNOSIS can autonomously coordinate responses to multiple threats in real-time. This capability significantly reduces the economic burden on defense operations, as it aims to replace costly interceptor missiles with a more efficient electronic warfare approach. The system is expected to complement existing air defense architectures without replacing them. The announcement precedes the Farnborough International Airshow, highlighting its strategic importance.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Israel Aerospace Industries in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 China-linked Hackers Exploit PHP2Shell to Compromise 25 Firewalls A China-linked threat actor has exploited vulnerabilities in PHP2Shell (CVE-2026-109618, CVE-2026-109619) and the Fragnesia privilege escalation bug (CVE-2026-46300) to gain root access to 25 firewalls, including those in an U.S. The attackers identified vulnerable systems using the FOFA search engine and executed…
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…