 www.cbsnews.com
California Dog Voting Fraud Case Highlights Election Loopholes
Article Content

- •A dog was registered to vote in California, highlighting election system loopholes.
- •Laura Lee Yourex faced charges after self-reporting her actions, leading to a misdemeanor plea.
- •California's lack of citizenship verification raises concerns about election integrity.
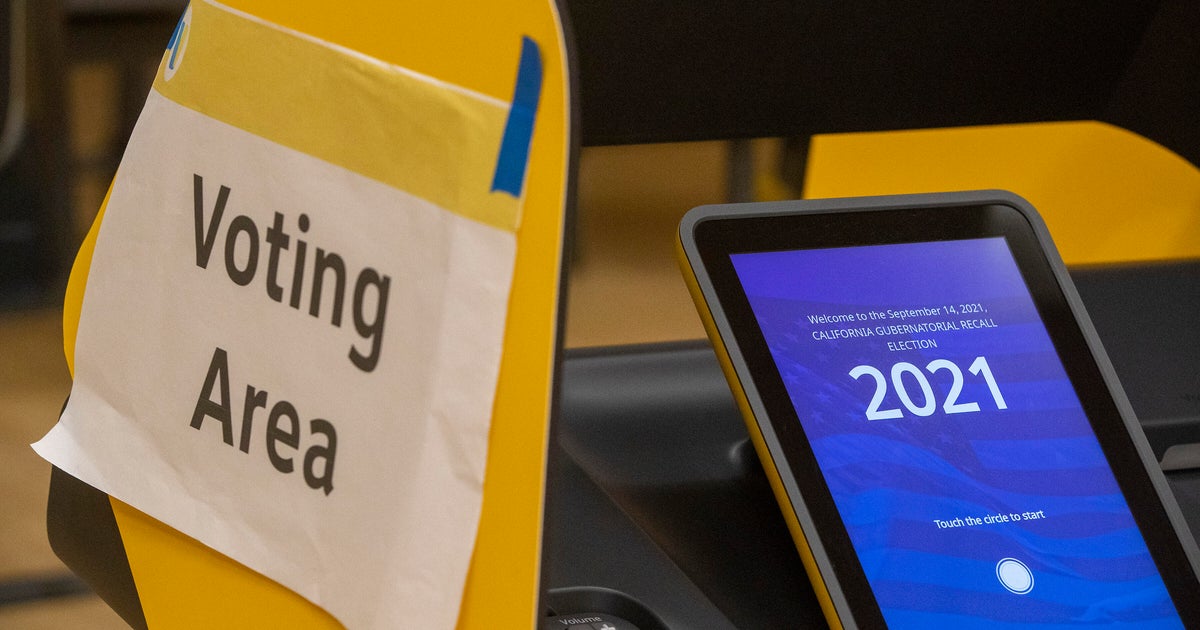
Laura Lee Yourex, a Costa Mesa resident, registered her dog, Maya Jean, to vote in California elections, successfully casting a ballot in the 2021 gubernatorial recall election. The dog's ballot was rejected in the 2022 primary due to federal verification requirements. Yourex self-reported her actions in 2024, leading to her prosecution by the Orange County District Attorney's Office. Initially charged with five felonies, she pleaded guilty to a misdemeanor and was fined $1,500. This incident underscores significant gaps in California's election integrity, as the state does not verify citizenship when registering voters. A federal judge recently ruled against enforcing laws to prevent noncitizens from voting, further complicating the issue. California voters are being urged to support Proposition 39, which aims to implement voter ID requirements and citizenship verification.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What charges did Yourex face?
Why was the dog's ballot counted?
What is Proposition 39?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…