 Ctvnews.Ca
Canada's Data Centres Face Rising Security Risks Amid Strategic Developments
Article Content

- •CSIS identifies data centres as critical for national security amid rising cyber threats.
- •The Canadian government plans a $1.5 billion data centre for the CSE in Ottawa.
- •Foreign ownership of data centres raises significant national security concerns.
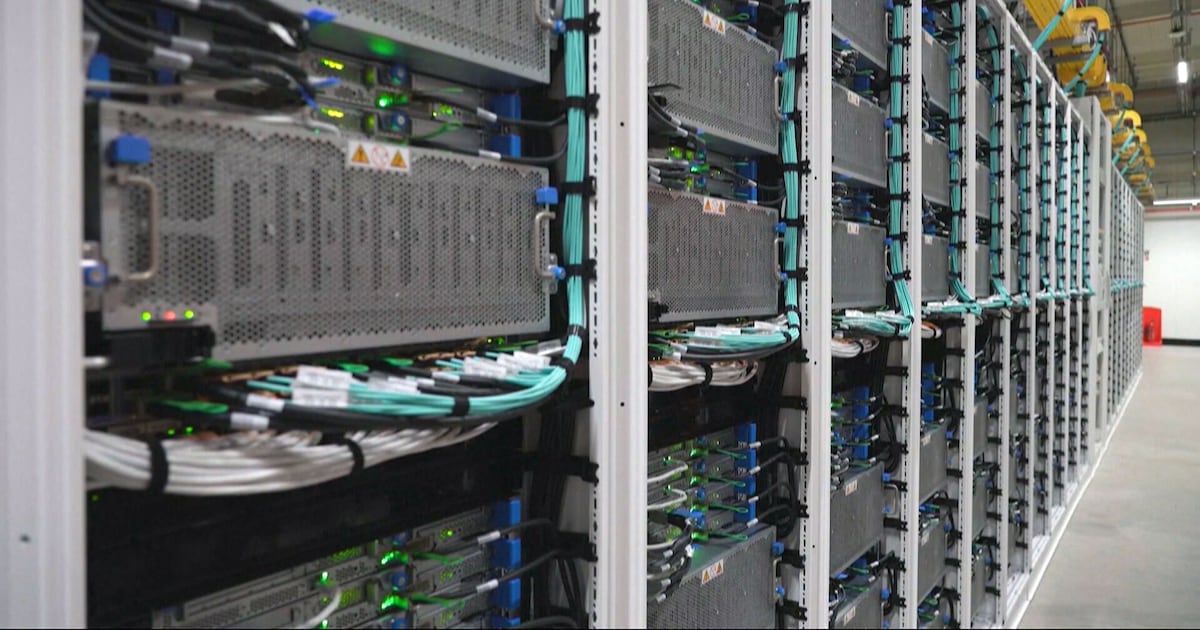
The Canadian Security Intelligence Service (CSIS) warns that data centres in Canada are becoming increasingly critical for national security, yet they face growing security risks from cyberattacks, supply chain vulnerabilities, and foreign threats. A recent assessment highlights the importance of these facilities in protecting sensitive information and supporting economic stability. The report emphasizes that foreign ownership poses significant risks, particularly from companies in China. Concurrently, the Canadian government plans to construct a new data centre for the Communications Security Establishment (CSE) in Ottawa, aimed at enhancing secure computing capacity. This facility will support mid to long-term objectives related to operations and technology modernization. The estimated cost of the project is between $1.5 billion and $1.8 billion, with a tender expected in 2027. The assessment also notes that data centres can be targets for cyberattacks, citing recent incidents involving Iranian and Russian attacks on data centres.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What security risks do data centres face?
What is the purpose of the new CSE data centre?
How much will the CSE data centre cost?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…