 Calgary.Citynews.Ca
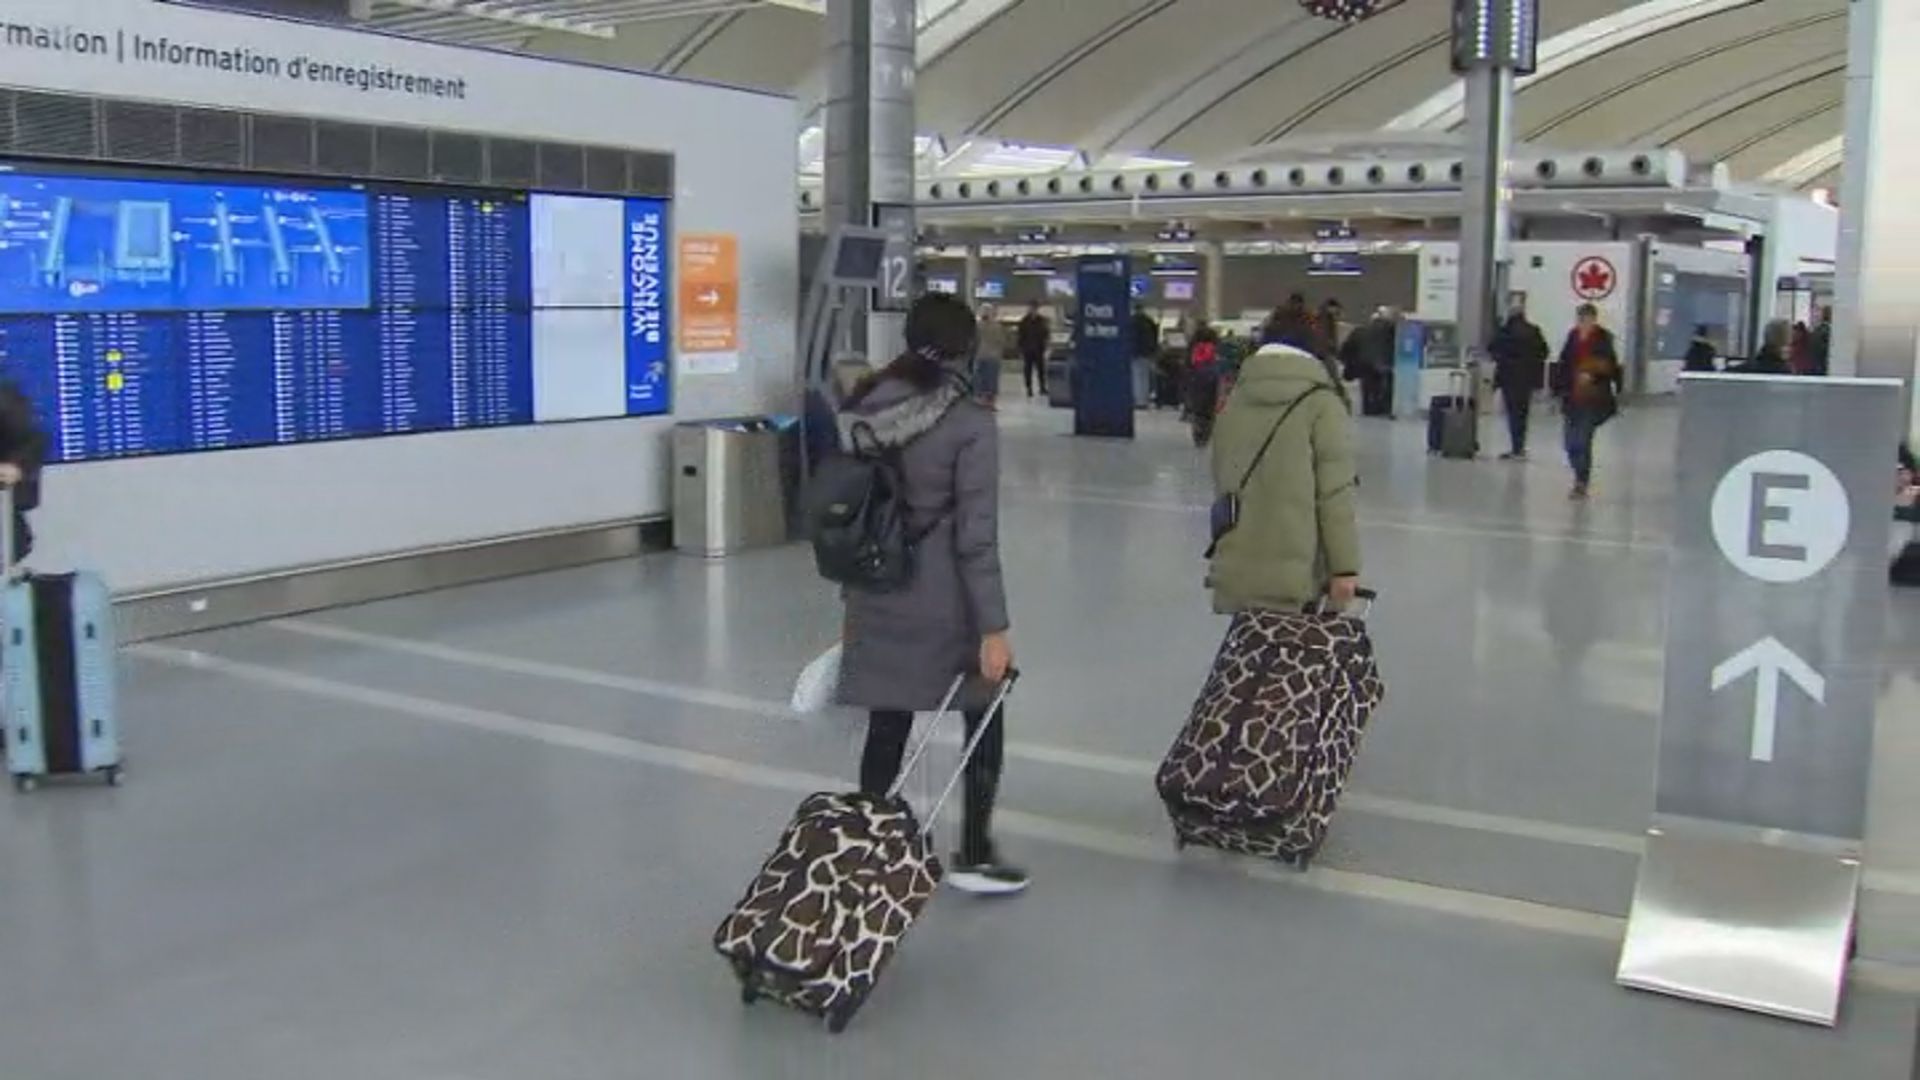
Canada's Major Airport Issues Warning on Misinformation from AI Websites
Article Content
Browse articles 
- •Canada's largest airport warns travelers about AI-generated misinformation.
- •Misinformation may include false travel advisories and flight schedules.
- •Travelers are urged to verify information through official sources.
Canada's largest airport has issued a warning to travelers about misinformation being spread by AI-generated websites. The airport has identified that these sites may provide false information regarding travel advisories, flight schedules, and safety protocols. The warning comes amid increasing concerns about the reliability of AI-generated content, especially as travelers prepare for busy travel seasons. Authorities have not specified the exact nature of the misinformation but emphasize the need for travelers to verify information through official channels. This advisory aims to protect travelers from potential scams and misinformation that could disrupt their travel plans.
Ask AI about this cluster
Answers cite the sources they use
Updated 10d ago How this analysis works
Timeline
2026-07-10
Airport issues warning
Canada's largest airport warns travelers about misinformation from AI websites affecting travel plans.
Edmonton.Citynews.CaMore articles in this cluster (5)
Common questions
What specific misinformation has been reported?
The airport has not detailed specific instances but warns about false travel advisories and flight schedules.
How can travelers verify information?
Travelers are advised to check official airport websites and trusted travel sources for accurate information.
Is this issue widespread?
The warning indicates a growing concern about AI-generated misinformation affecting travelers, particularly during busy seasons.
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…