 Nine.Au
Canberra Cyber Bootcamp Tackles Online Radicalisation Among Youth
Article Content

- •The re_B00TCMP bootcamp educates youth on ethical hacking and online safety.
- •35 high school students participated, selected for their outstanding IT skills.
- •The program addresses the rapid radicalisation of boys exposed to online extremist content.
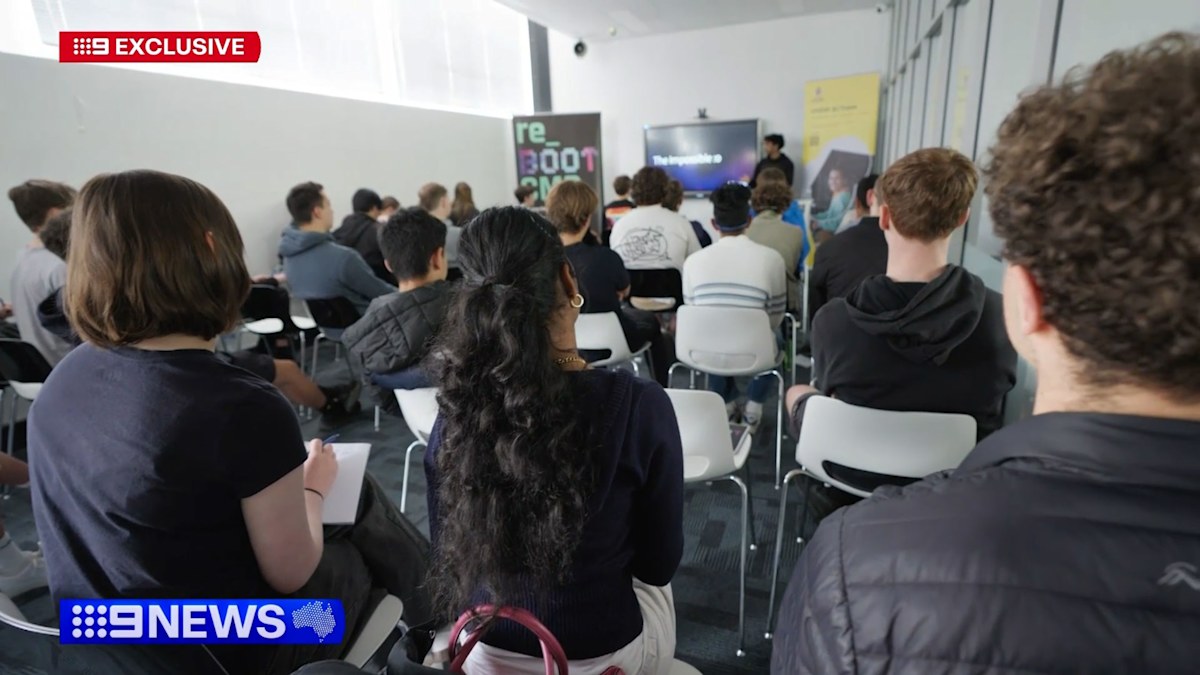
The re_B00TCMP cyber bootcamp, hosted by the Australian Federal Police, aims to educate young Australians aged 12-18 about ethical hacking and online safety. Held at the University of NSW on October 28, 2026, the program selected 35 students for their IT skills, focusing on combating the rapid radicalisation of boys exposed to online extremist content. Participants engaged in a 'Capture the Flag' competition, simulating real-world cyber incidents to develop their skills. Acting Assistant Commissioner Matthew Gale emphasized the importance of teaching children to use their cyber skills for good, particularly in light of recent threats from malicious state actors. The program also includes guidance for parents and educators on supporting safe online practices. Early evaluations show a significant increase in participants' understanding of online boundaries, with 98% reporting awareness of legal limits after the program. The initiative has been implemented in multiple Australian cities, demonstrating a positive impact on youth engagement in cybersecurity careers.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
Who can participate in the re_B00TCMP bootcamp?
What skills do participants learn?
How does the program address radicalisation?
Continue Reading
 Binance Hack: $6.3 Billion Stolen in Largest Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a major security incident involving an estimated $6.3 billion in stolen funds. The attack was attributed to a compromised laptop belonging to a DevOps engineer, allowing unauthorized withdrawal transactions. Approximately $3 billion in…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…