 Cyberdaily.Au
Canva Confirms Data Breach Linked to Third-Party Tool
Article Content

- •Canva experienced a data breach through a third-party tool, Canny.
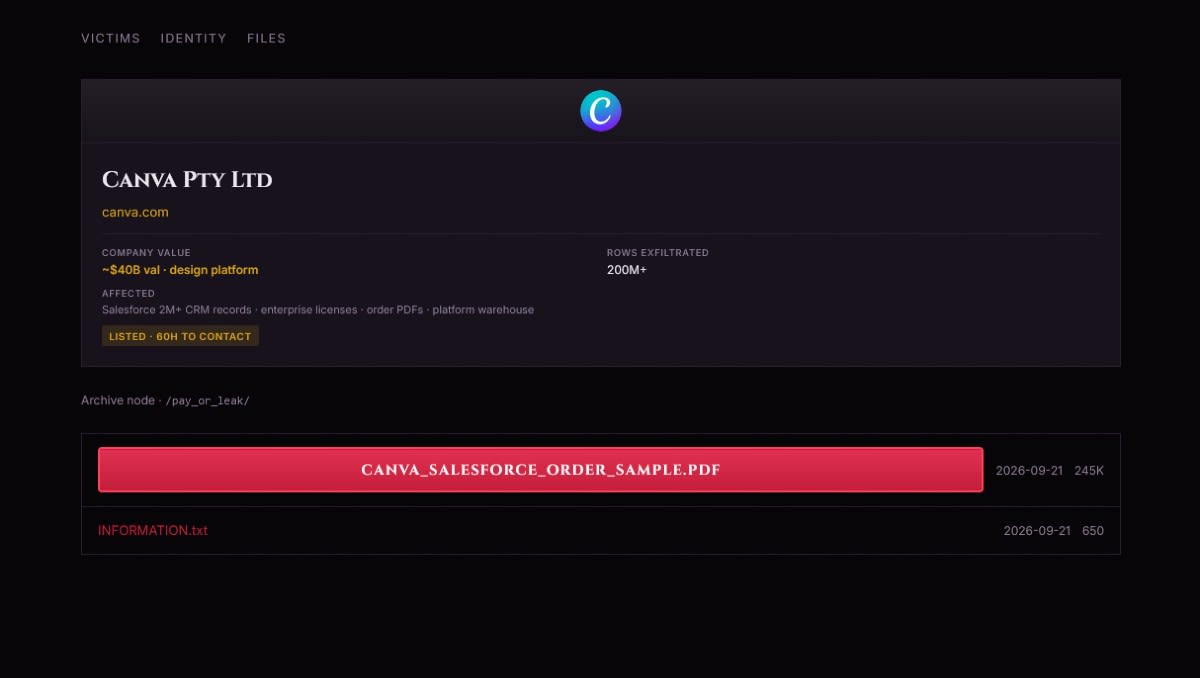
- •The Seven Deadly Sins ransomware group claims to have accessed over two million records.
- •Canva's core systems remain secure, and affected customers have been notified.
Canva has acknowledged a data breach affecting some enterprise customer records due to unauthorized access via Canny, a third-party tool used for product feedback. The Seven Deadly Sins ransomware group claimed responsibility, stating they accessed over two million Salesforce records, including enterprise license orders and billing PDFs. A sample document was published as proof of the breach, which the hackers allege has already been sold to a private buyer. Canva reported that its own systems were not compromised, and it has since revoked Canny's access and notified affected customers. The company has a history of data breaches, including significant incidents in 2019 and 2020. Canva is a major player in the tech industry, with over 265 million monthly active users and partnerships with notable companies like Netflix and YouTube.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Seven Deadly Sins and Salesforce in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was compromised?
Is Canva's platform secure?
What actions should affected customers take?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…