 Channelnewsasia
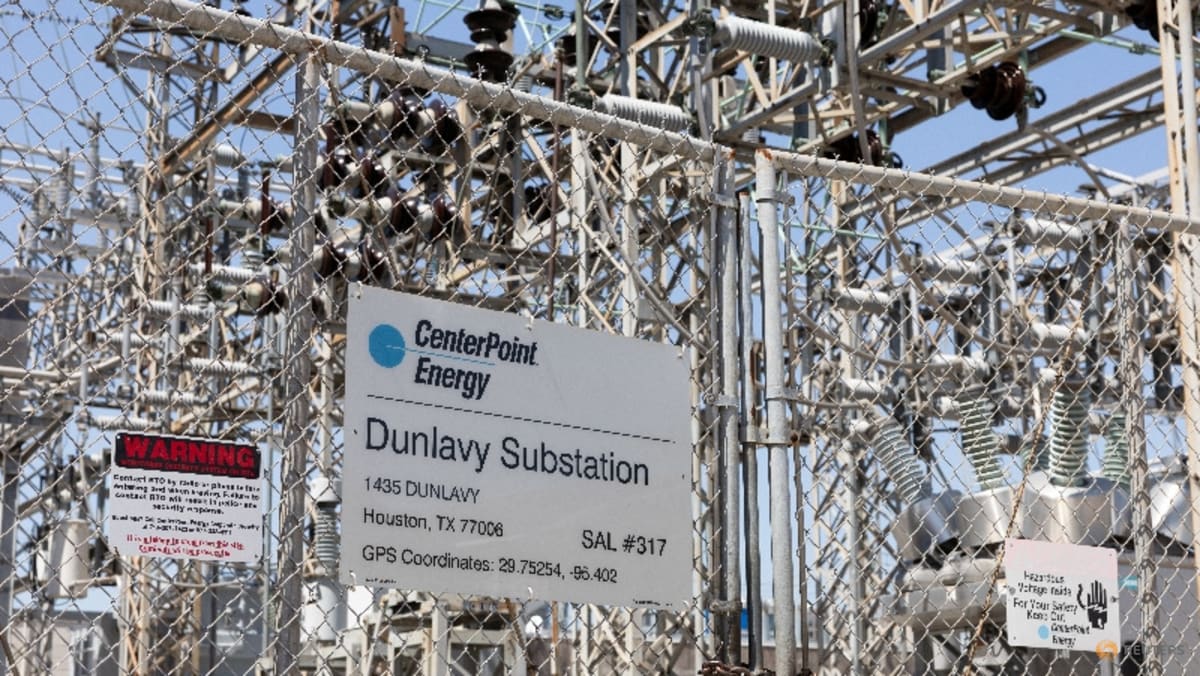
CenterPoint Energy Confirms Data Breach Affecting Millions of Customers
Article Content

- •CenterPoint Energy confirmed a breach affecting approximately 7.49 million customer records.
- •The breach was attributed to vulnerabilities in the company's external-facing systems.
- •No disruption to electric and gas services has been reported, and the company is investigating the incident.
CenterPoint Energy disclosed a data breach affecting customer information after a hacker leaked claims of having stolen 7.49 million records. The breach was confirmed following an online post by a threat actor who exploited vulnerabilities in the company's external-facing systems. The leaked data reportedly includes names, phone numbers, service addresses, account numbers, and partial Social Security numbers. CenterPoint Energy stated that its electric and gas services remain operational and that the incident is not expected to materially impact its financial condition. The company has activated its incident response protocols and is working with third-party cybersecurity experts to assess the situation. Multiple lawsuits have already been filed against the company by affected customers. The investigation into the breach is ongoing, and the company plans to notify affected customers and regulatory authorities as required by law.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (29)
Following this threat?
Track CenterPoint Energy in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…