 Foxnews
Charles Lieber Leads Brain-Computer Interface Lab in China Post-Conviction
Article Content

- •Charles Lieber leads a new brain-computer interface lab in Shenzhen, China.
- •Lieber was previously convicted for concealing ties to a Chinese recruitment program.
- •His new facility has access to advanced technology and significant state funding.
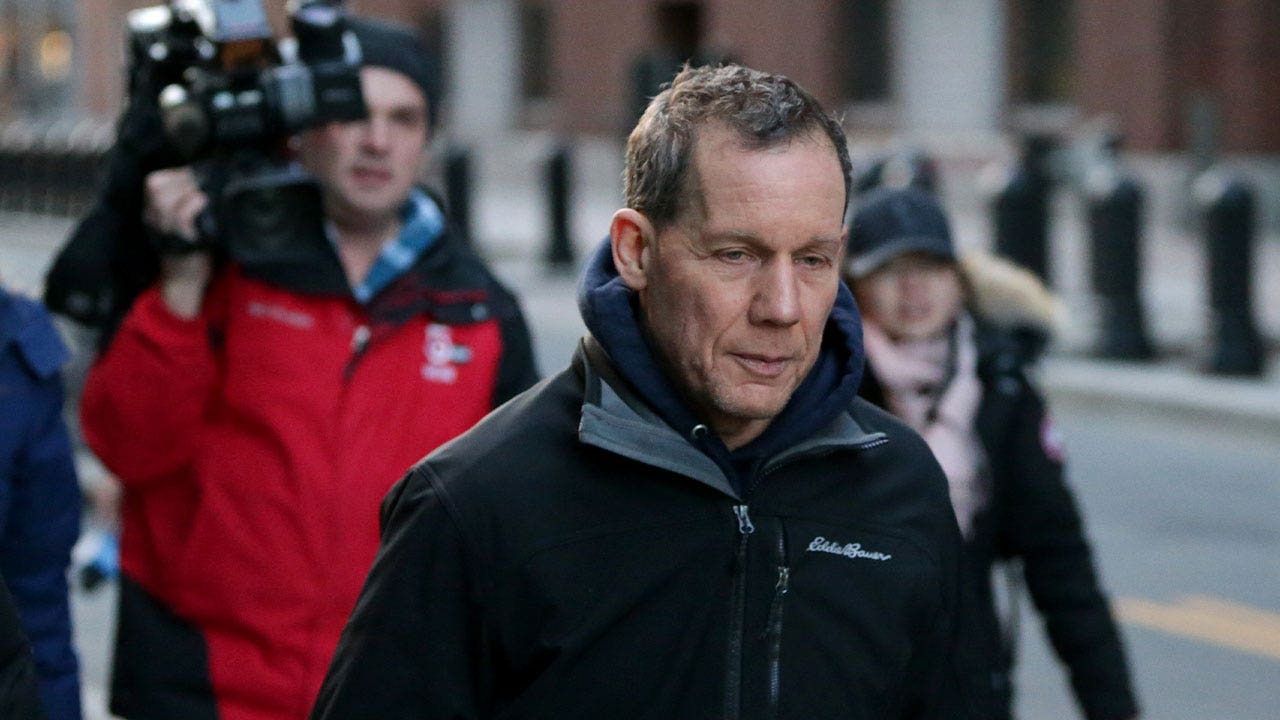
Charles Lieber, a former Harvard scientist convicted in 2021 for lying about his ties to a Chinese recruitment program, has established a brain-computer interface research lab in Shenzhen, China. After serving a brief prison sentence and house arrest, Lieber is now the head of the Institute for Brain Research, Advanced Interfaces and Neurotechnologies (i-BRAIN). His new facility, backed by the Chinese government, focuses on developing brain-computer interfaces, which could have both medical and military applications. Lieber's previous contract with Wuhan University of Technology paid him $50,000 monthly, but his new lab reportedly has access to advanced resources and significant state funding. His defection raises concerns about the effectiveness of U.S. export controls and research oversight, as China continues to recruit top-tier scientists despite prior convictions. The situation highlights ongoing tensions regarding technology transfer and national security between the U.S. and China.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…