 www.sabado.pt
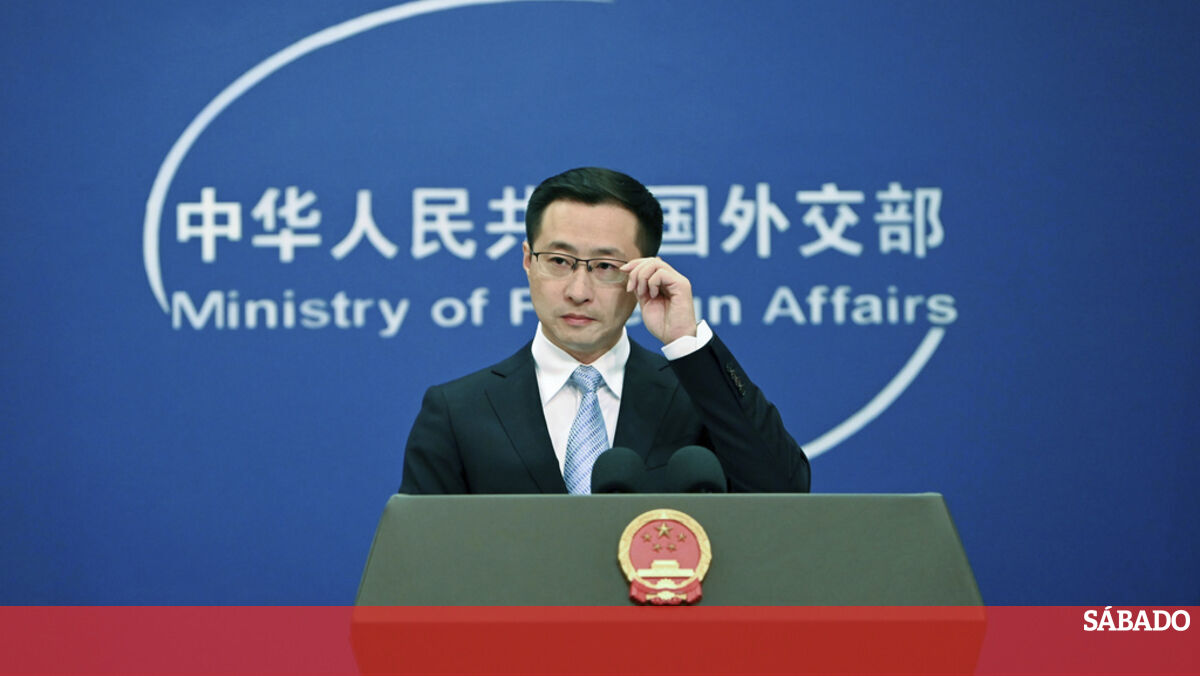
China Accuses U.S. of Technological Harassment in Latin America
Article Content

- •China claims the U.S. is pressuring Latin American nations to drop Chinese tech providers.
- •The U.S. cites risks of espionage and cyberattacks from companies like Huawei and ZTE.
- •Chinese officials label U.S. warnings as technological harassment and demand an end to interference.
China has accused the United States of pressuring Latin American countries to replace Chinese technology providers. This follows U.S. warnings about potential risks of espionage, cyberattacks, and network disruptions linked to companies like Huawei and ZTE. Chinese officials labeled these warnings as 'flagrant technological harassment' and called for an end to U.S. interference in sovereign decisions. The U.S. urged its partners in the region to swiftly transition to 'trusted' suppliers to safeguard their citizens and sovereignty. China defended its technology firms, asserting compliance with local laws and contributions to economic development. The dispute has escalated tensions between the two nations, particularly in the context of geopolitical maneuvering in Latin America. No specific cyber incidents or vulnerabilities were reported in the articles, focusing instead on diplomatic exchanges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…