 Scmp
China Conducts Patrols in Response to Japan-Philippines Maritime Talks
Article Content
Browse articles 
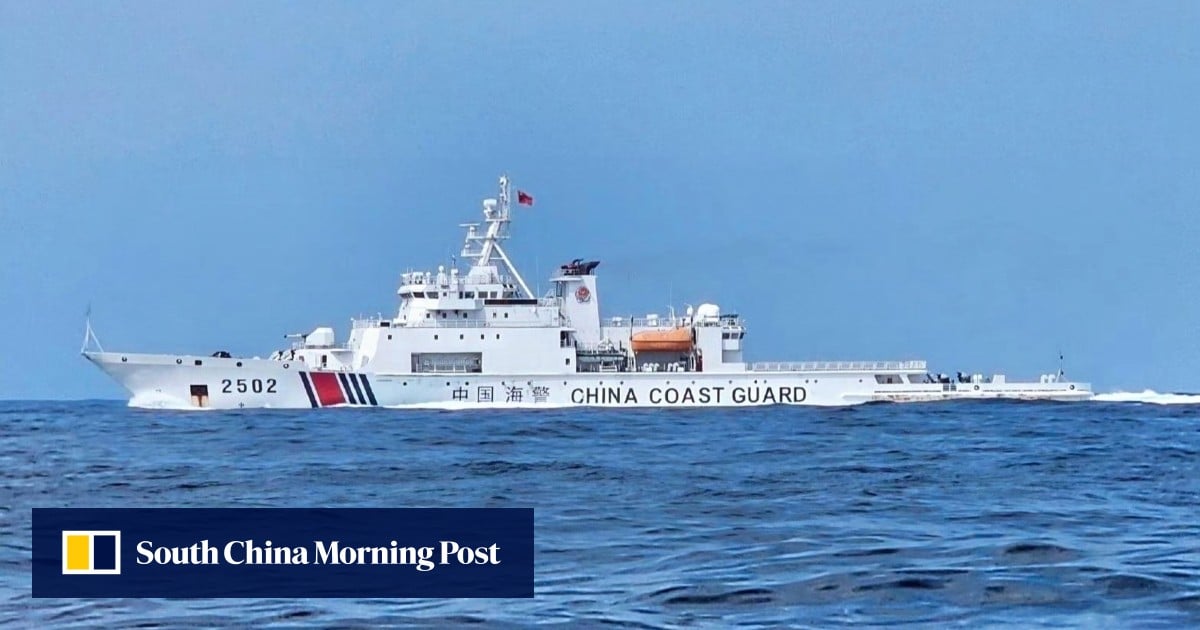
- •China's Coast Guard patrolled waters east of Taiwan on June 1, 2026.
- •The patrols respond to Japan and the Philippines' maritime boundary negotiations.
- •Taiwan's government disputes China's claims over the region.
On June 1, 2026, China's Coast Guard conducted law enforcement patrols in waters east of Taiwan. This action was described as a necessary response to Japan and the Philippines' announcement of maritime boundary delimitation negotiations, which China claims infringe on its territorial sovereignty. The Chinese Coast Guard's spokesman emphasized the need to safeguard China's maritime rights and interests. Taiwan's government has rejected China's claims over these waters, indicating ongoing territorial disputes in the region. The patrols are part of China's broader strategy to assert control over disputed maritime areas.
Ask AI about this cluster
Answers cite the sources they use
Updated 111d ago How this analysis works
Timeline
2026-06-01
China conducts patrols east of Taiwan
China's Coast Guard carried out law enforcement patrols in response to Japan and the Philippines' maritime boundary talks, asserting territorial claims.
Scmp2026-06-01
Japan and Philippines announce maritime talks
Japan and the Philippines revealed plans to discuss maritime boundary delimitation in areas claimed by China, prompting China's response.
M.EconomictimesMore articles in this cluster (13)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…