 Businesstimes.Sg
China Enforces Strict Drone Regulations Amid Safety Concerns
Article Content

- •New regulations require real-name registration for all drones in China.
- •Beijing has enacted a near-total ban on drone operations within the city limits.
- •Existing drone owners must register by April 30, 2026, or face penalties.
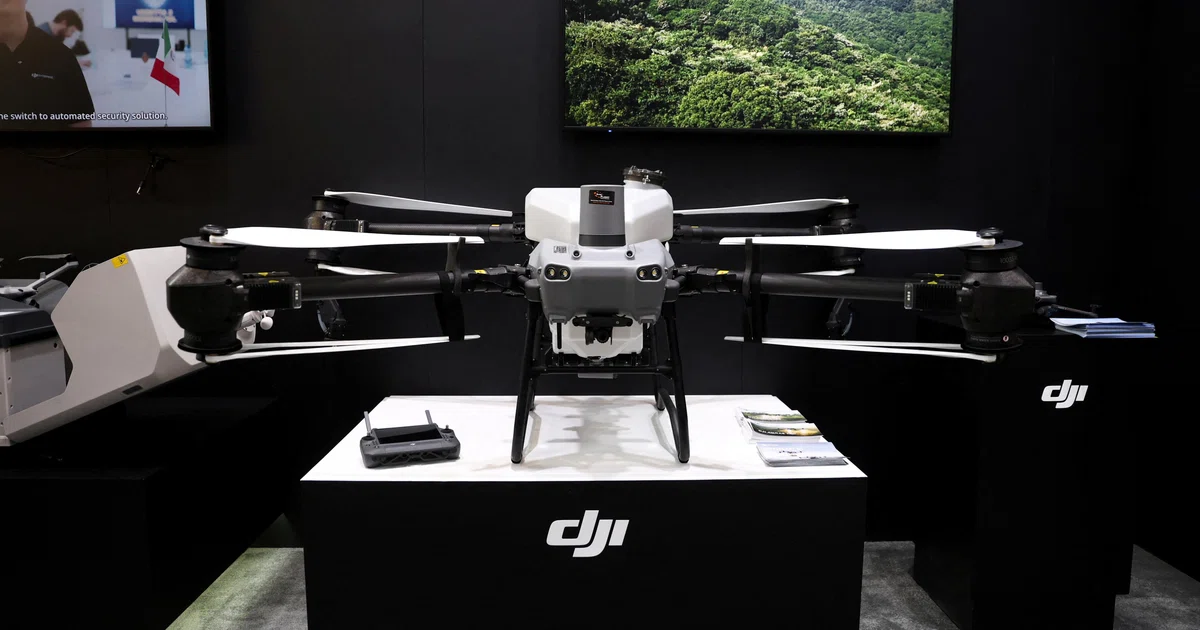
China, a leader in the global drone industry, is implementing stringent regulations for drone operations starting in May 2026. New rules require all drones to be registered with the owners' real names, linking flight equipment to official identification or cellphone numbers. Penalties for unauthorized drone flights have been increased to include potential jail time. The city of Beijing has adopted a near-total ban on drones, prohibiting their sale, rental, or entry into the city. Existing drone owners must register their devices by April 30, 2026, and are limited to three drones per address. The regulations aim to enhance public safety and address risks associated with drone operations, including hacking and incidents threatening civil aviation. As of the end of 2025, China had over three million registered drones, reflecting a 50% increase from 2024. The Ministry of Public Security emphasizes that these measures are necessary to protect citizens and facilitate a planned expansion of commercial drone use.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…