 Scmp
China's Proposed Space-Based Train Control System Raises Hacking Concerns
Article Content

- •China is exploring a space-based control system for its high-speed rail network.
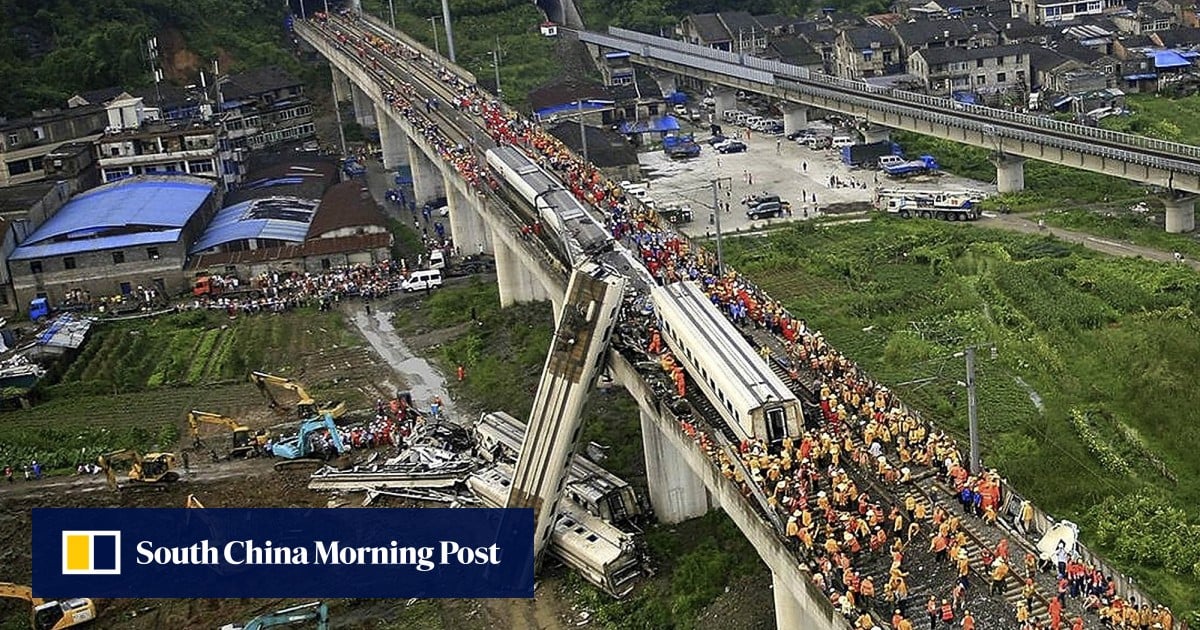
- •The system aims to prevent disasters like the 2011 Wenzhou train crash caused by a lightning strike.
- •Cybersecurity risks could allow hackers to exploit the new technology and crash trains.
A team of researchers in Beijing has proposed a space-based control system for China's high-speed rail network, aiming to enhance resilience against disasters like the Wenzhou train crash. The system would utilize low-orbit satellites to manage train operations, potentially preventing failures caused by natural events. However, the same technology could be vulnerable to cyberattacks, allowing hackers to manipulate train controls and cause crashes. The original Wenzhou disaster was linked to a lightning strike that rendered a train invisible to the control center, leading to a fatal collision. The proposed system could eliminate reliance on ground-based infrastructure, which is costly and susceptible to environmental damage. Despite its potential benefits, the research highlights the dual-use nature of the technology, raising alarms about new cyber threats. The paper was published in May 2026 in the Railway Signalling and Communication Engineering journal.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…