 www.scmp.com
China's Satellite Operations Escalate Space Warfare Concerns
Article Content

- •China claims to have conducted in-orbit refueling of the BeiDou-2 G7 satellite, but tracking data disputes this.
- •Shijian-21 has been observed maneuvering to pull a defunct satellite into a graveyard orbit, raising military concerns.
- •U.S. Space Force officials highlight a shift in space operations towards aggressive tactics, including 'dogfighting'.
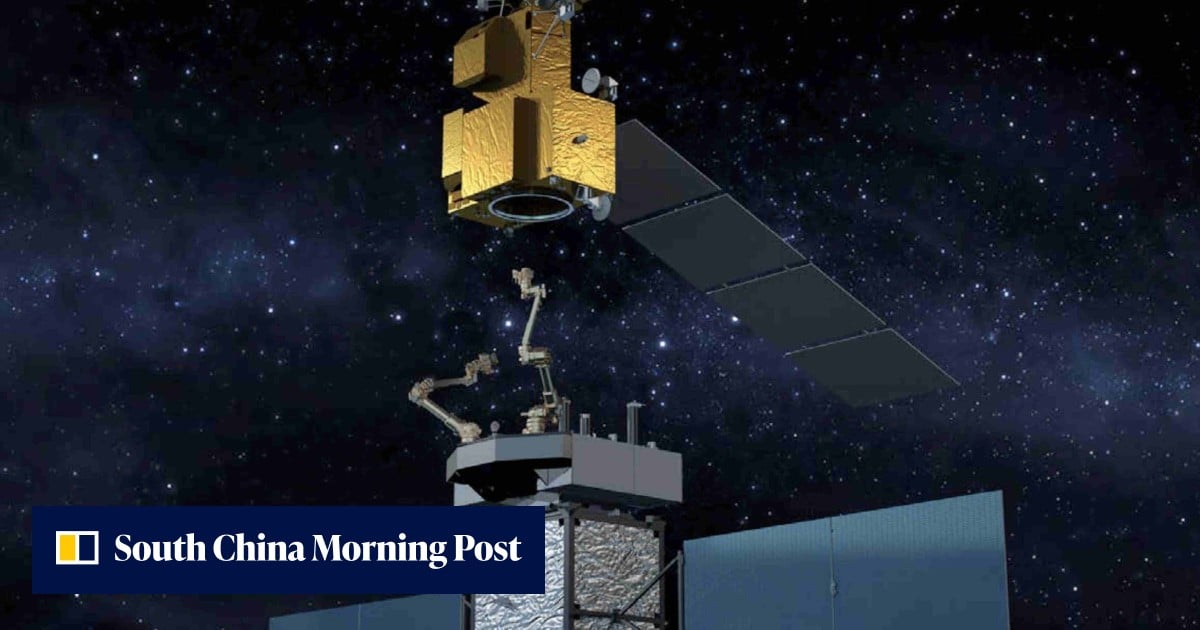
Recent reports indicate that China has engaged in significant satellite operations, including a disputed in-orbit refueling of the BeiDou-2 G7 satellite and the grappling of a defunct satellite by Shijian-21, raising alarms about military applications. The alleged refueling operation, claimed to have occurred in February 2025, could extend satellite operational lifespans and enhance tactical mobility, though independent tracking disputes its occurrence. Meanwhile, Shijian-21's maneuver to pull another satellite into a graveyard orbit has been observed, prompting concerns over China's intentions with its on-orbit servicing capabilities. U.S. Space Force officials have noted that these developments reflect a shift toward aggressive space tactics, including 'dogfighting' maneuvers in low-Earth orbit. The implications of these advancements could fundamentally alter the dynamics of space warfare, emphasizing the need for heightened vigilance among U.S. and allied space operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…