 Tokyoreporter
Chinese Couple Indicted for Massive Phishing Scheme in Kobe Hotel
Article Content

- •A Chinese couple was indicted for sending 480,000 phishing emails from a hotel in Kobe.
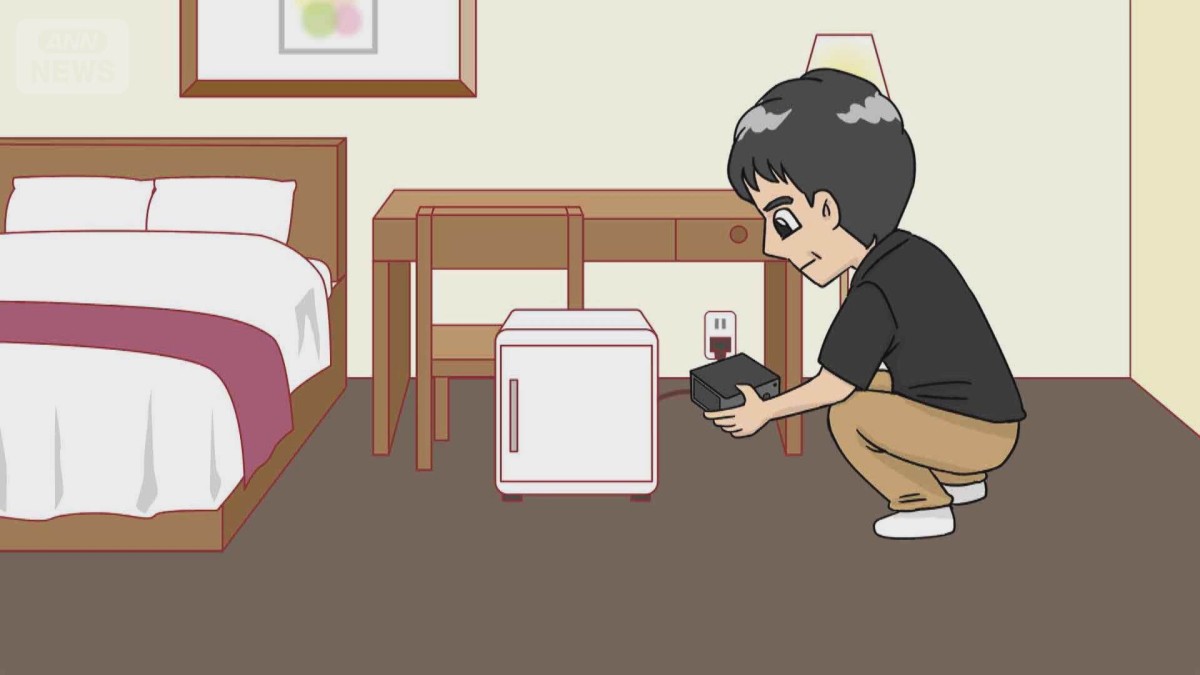
- •They concealed a laptop in their hotel room to exploit the hotel's Wi-Fi network.
- •Authorities suspect involvement in a larger organized cybercrime syndicate.
A Chinese couple, Ye Jiafeng and Shen Qi, were indicted for hiding a laptop in a Kobe hotel to send hundreds of thousands of phishing emails. They allegedly used the hotel's Wi-Fi to send at least 480,000 scam messages impersonating credit card companies. The couple checked into the hotel in August 2025, concealing the laptop in their room before leaving it powered on for remote access by an accomplice. The scheme was uncovered after hotel staff noticed irregularities and contacted local police. The couple faces charges including fraudulent obstruction of business and trespassing. Authorities suspect they are part of a larger cybercrime syndicate exploiting public Wi-Fi networks. Police have seized 74 smartphones from their possession and are investigating further. Cybersecurity experts warn that such phishing schemes are becoming increasingly common and difficult to detect.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What phishing methods were used?
What charges are the couple facing?
How can hotels protect against similar attacks?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…