 Asiae.Co.Kr
Clash Over Cyber Sanctions Following DMZ Land Mine Incident
Article Content

- •Minister Jeong opposes cyber sanctions linked to the DMZ land mine explosion.
- •The land mine incident injured three South Korean soldiers and is attributed to North Korea.
- •A significant rift exists within the South Korean government regarding North Korea policy.
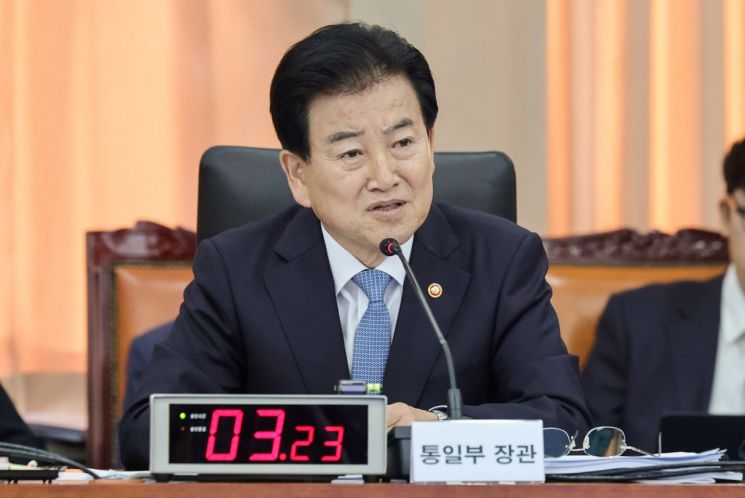
During a National Assembly audit on October 7, 2026, South Korean Minister of Unification Jeong Dongyoung and Foreign Minister Cho Hyun clashed over proposed unilateral cyber sanctions against North Korea following a land mine explosion in the DMZ. Minister Jeong argued that sanctions and peaceful coexistence cannot coexist, questioning the relevance of cyber sanctions to the incident. The land mine explosion, which occurred in September, injured three South Korean soldiers and was attributed to North Korea. The Ministry of Foreign Affairs aimed to expand sanctions against North Korean cyber operations, while the Ministry of Unification advocated for a more cautious approach. The disagreement reflects a broader rift within the South Korean government regarding its policy towards North Korea, with pro-alliance and autonomy factions at odds. The situation remains tense as lawmakers continue to debate the appropriate response to the incident.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the cause of the land mine explosion?
What are the proposed cyber sanctions?
What is the current status of the debate?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…