 Hellorayo
Cornwall Sex Offender Jailed for Dark Web Access Violations
Article Content

- •Richard Over was sentenced to three years and two months for breaching his SHPO.
- •A hidden tablet with dark web software was found during a police visit in April 2026.
- •Over had a history of multiple breaches of court orders since September 2023.
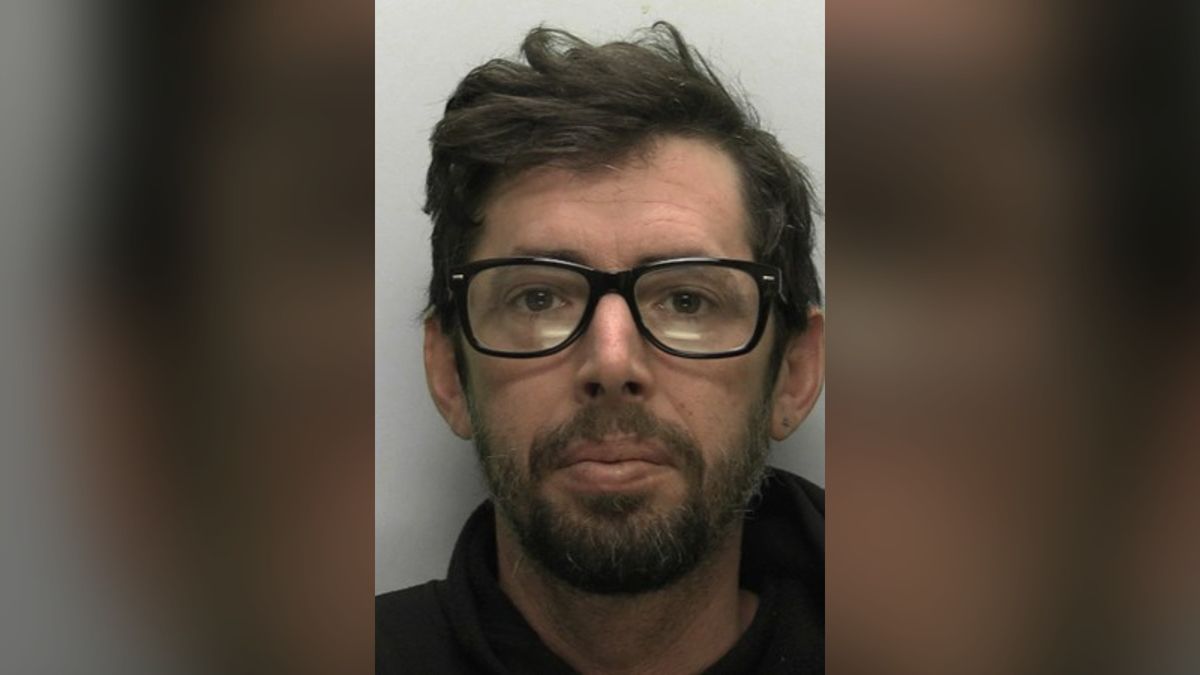
Richard Over, a 43-year-old high-risk sex offender from Marazion, Cornwall, has been sentenced to over three years in prison for breaching a Sexual Harm Prevention Order (SHPO). During an unannounced police visit in April 2026, officers discovered a PIN-locked tablet hidden under his duvet, which contained a history-concealing browser and dark web software. Over had previously been convicted of making indecent images of children in 2017 and 2024, receiving suspended sentences. He admitted to five breaches of his SHPO between December 2025 and April 2026, and had a history of breaching his notification requirements. The SHPO prohibited him from using internet-enabled devices without notifying police and required devices to retain online history. Police Constable Ross Waite emphasized the seriousness of Over's actions, highlighting the importance of monitoring offenders to protect vulnerable individuals.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…