 Techreviewafrica
CRASA Advocates for Enhanced Cybersecurity in Southern Africa
Article Content

- •CRASA calls for stronger cybersecurity measures in Southern Africa.
- •The Executive Masterclass focuses on spectrum management and security.
- •Dr. Shanapinda emphasizes regulatory harmonisation for better connectivity.
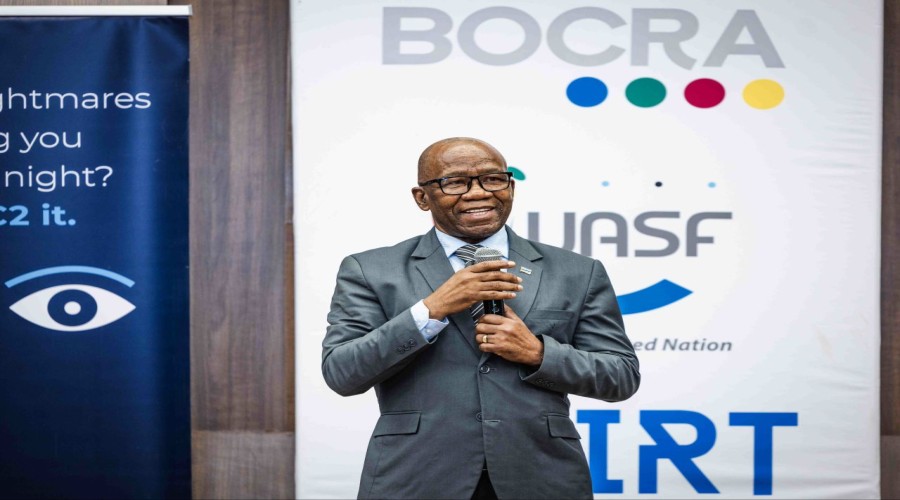
The Communications Regulators’ Association of Southern Africa (CRASA) has called for improved cybersecurity and regulatory harmonisation to bolster digital infrastructure across Southern Africa. This appeal was made by Dr. Stanley Shanapinda during a keynote address at the Commonwealth Telecommunications Organisation (CTO) Executive Masterclass in Gaborone, Botswana, from October 26 to 30, 2026. The masterclass focuses on spectrum management, satellite communications, and security in the commercial space economy. Shanapinda emphasized the need for coordinated regional investments and stronger cybersecurity measures to ensure secure communications networks. He also highlighted the importance of addressing barriers to connectivity, including affordability and digital skills. The initiative aims to foster investment and advance economic integration within the Southern African Development Community (SADC).
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is CRASA's main focus?
Who delivered the keynote address?
What topics are covered in the Masterclass?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…