 Techtimes
Critical Calix Router Flaw Exposes Home Networks to Attack
Article Content

- •CVE-2026-75501 allows remote attackers to bypass NAT and firewall protections.
- •No patch is available, and users are advised to disable UPnP as a workaround.
- •The vulnerability affects Calix GS5239XG routers, widely used by U.S. broadband providers.
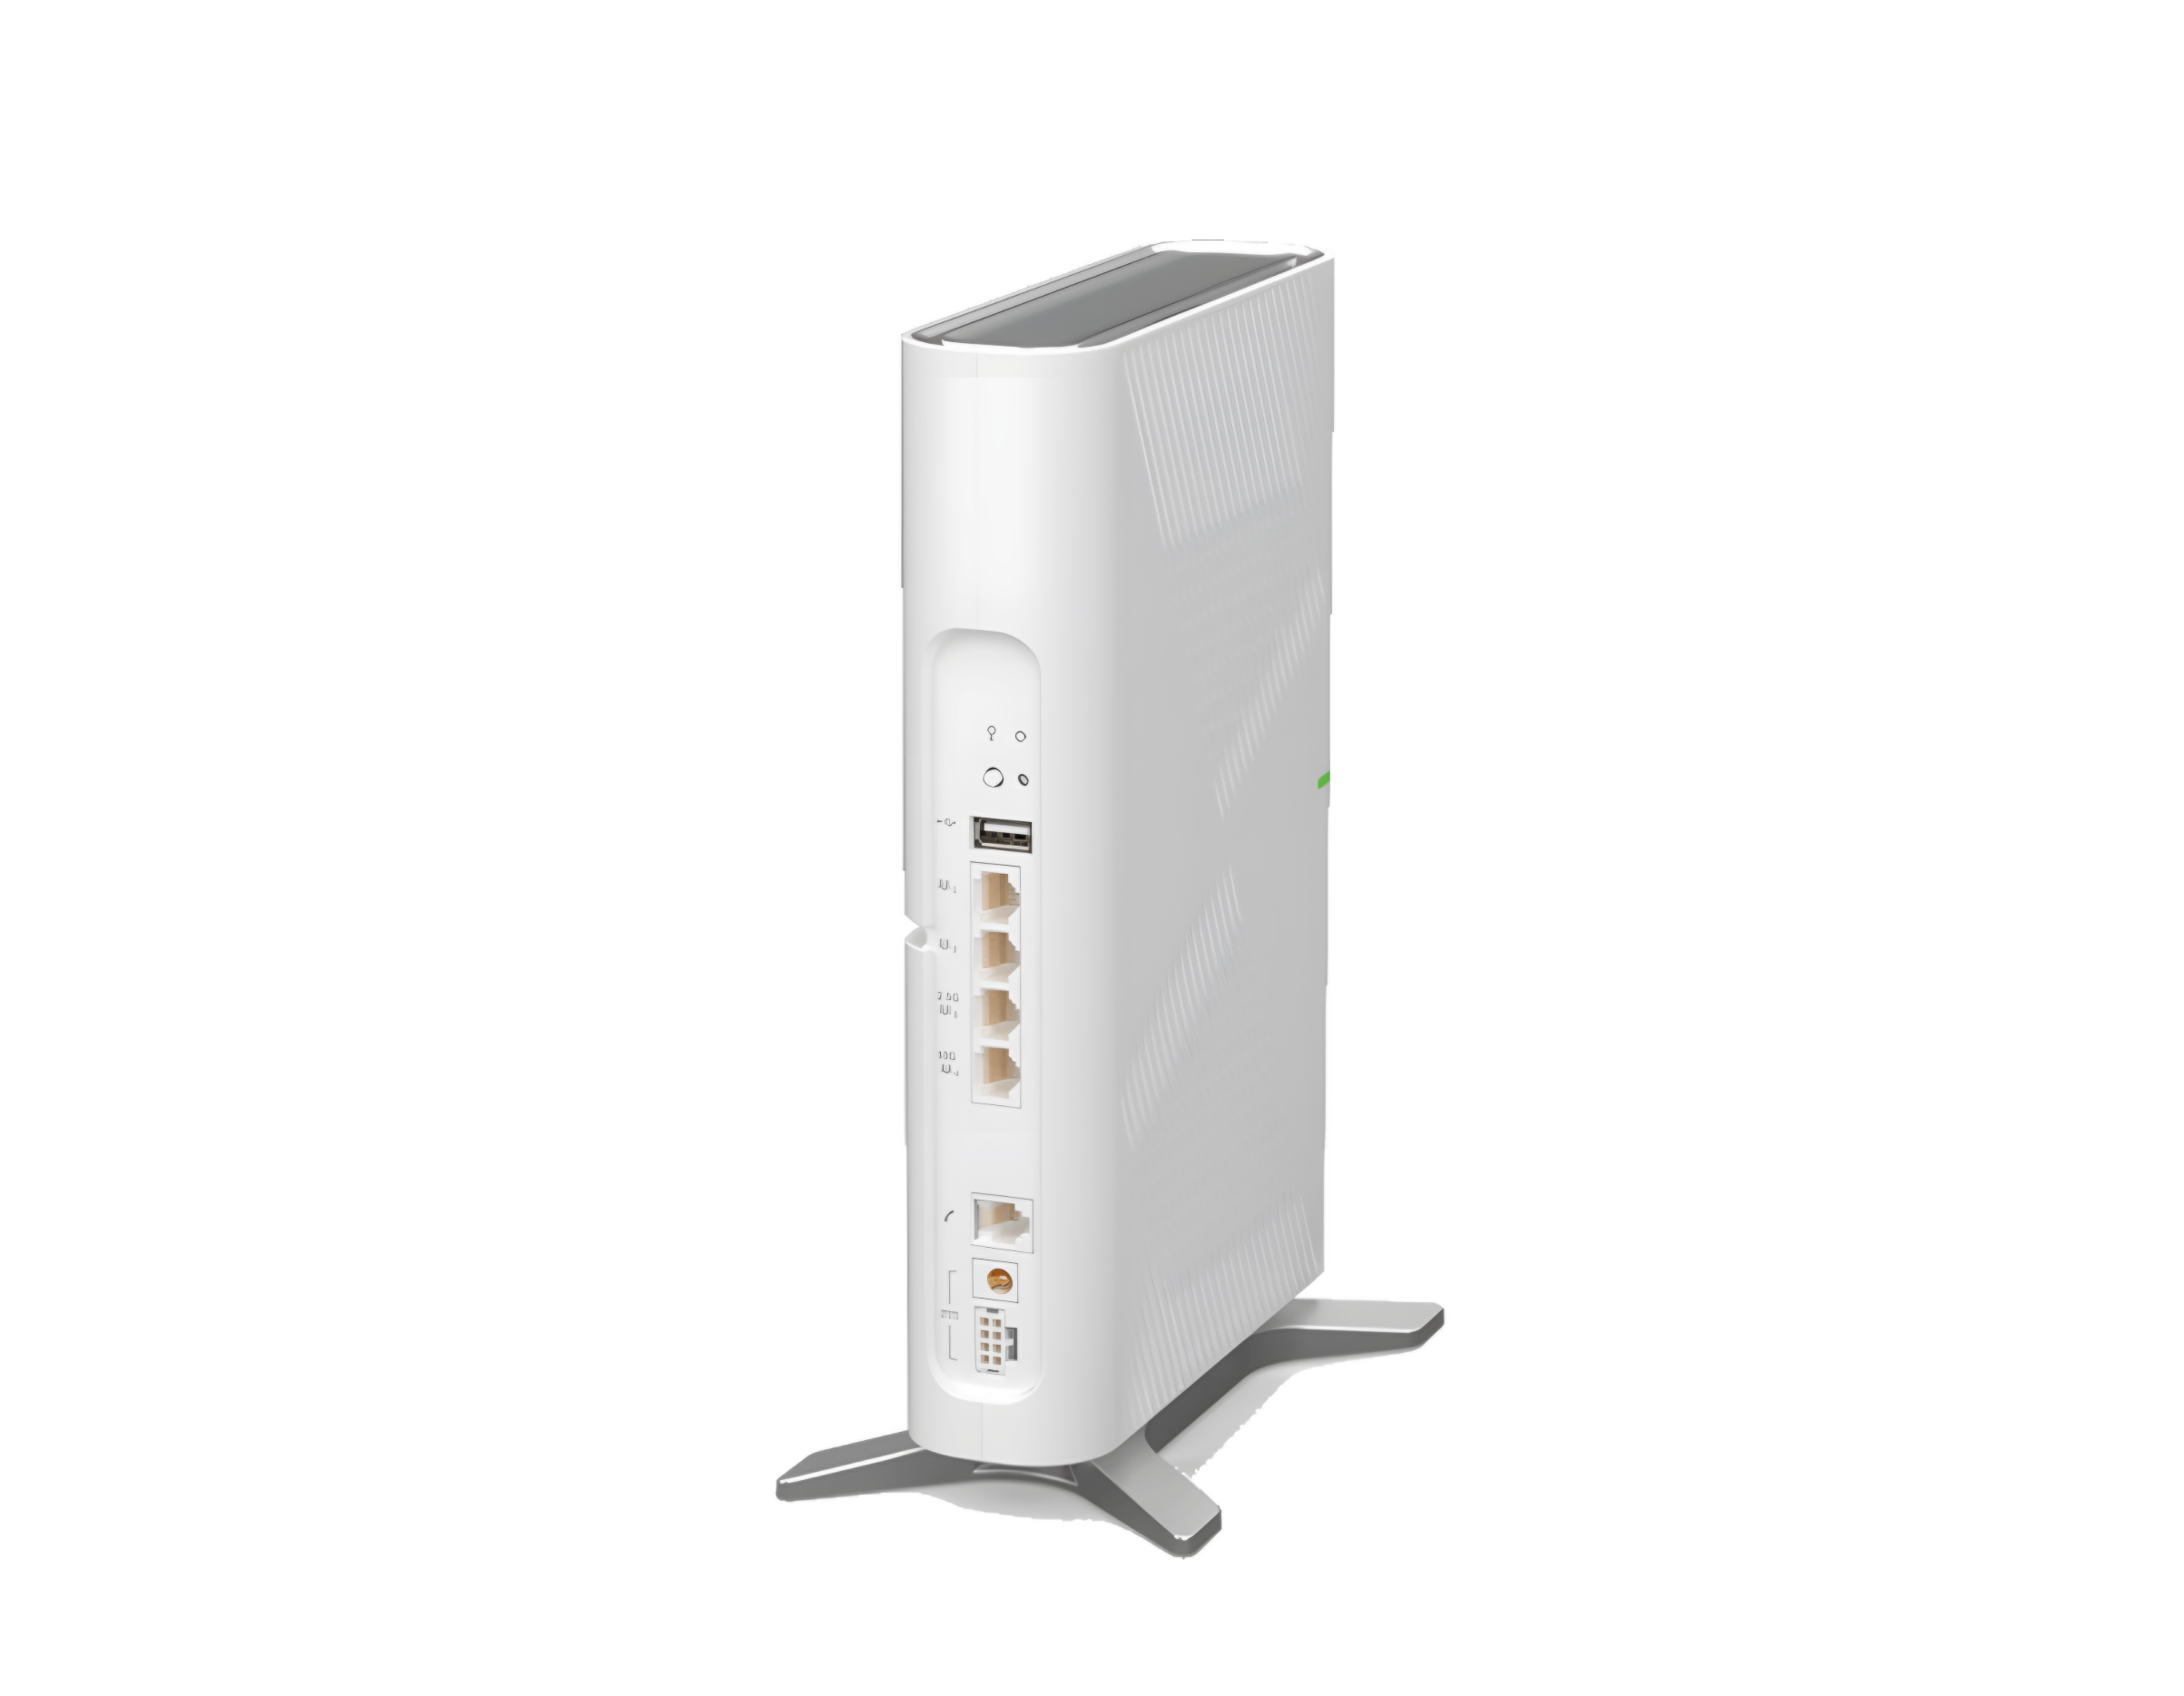
A critical vulnerability in Calix GS5239XG routers, tracked as CVE-2026-75501, allows unauthenticated remote attackers to create port-forwarding rules, exposing internal devices to the internet. Discovered by researcher Brian Khan Quintana, the flaw stems from the router's UPnP control endpoint being accessible on the WAN interface without authentication. This issue affects devices running EXOS/6.6.47 firmware and has been confirmed by the Carnegie Mellon CERT Coordination Center. No patch or firmware update has been released by Calix, and users are advised to disable UPnP as a temporary workaround. The vulnerability places millions of devices at risk, as many routers are provisioned with UPnP enabled by default. The potential impact includes exposure of sensitive internal devices like cameras and NAS drives. The situation is urgent, with active exploitation observed in the wild, as attackers can easily manipulate the router settings without user intervention.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Brightspeed and CVE-2026-75501 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…