 www.socdefenders.ai
Critical RCE Vulnerability in SWIFT Middleware Discovered
Article Content

- •CVE-2026-18397 is a critical RCE vulnerability affecting SWIFT middleware.
- •Attackers can bypass multi-factor authentication and gain privileged access remotely.
- •No public breaches have been reported, but immediate patching is essential.
A critical remote code execution (RCE) vulnerability, CVE-2026-18397, has been identified in middleware components used by SWIFT banking systems and government authentication portals. This flaw allows attackers to bypass multi-factor authentication (MFA) and gain privileged access to sensitive environments. The vulnerability stems from a cryptographic implementation flaw that permits oversized signatures and stale memory reads, enabling the injection of malicious DLLs. Attackers can exploit this vulnerability remotely, achieving complete compromise of the authentication layer in as little as six seconds. While no public breaches have been reported, the ease of exploitation and the critical nature of affected systems make it a high-priority risk. Immediate patching is recommended to mitigate potential threats. The vulnerability is currently not listed as exploited in the CISA KEV catalog.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Thales and CVE-2026-18397 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What systems are affected by CVE-2026-18397?
How can organizations mitigate this risk?
Is there any evidence of exploitation in the wild?
Continue Reading
 Critical Vulnerability Found in Thales SConnect Allows Remote Code Execution A critical vulnerability, CVE-2026-18397, has been identified in Thales SConnect, enabling unauthenticated remote code execution (RCE) on affected systems. The flaw arises from cryptographic weaknesses and memory management issues, allowing attackers to exploit an unrestricted messaging interface between a web page…
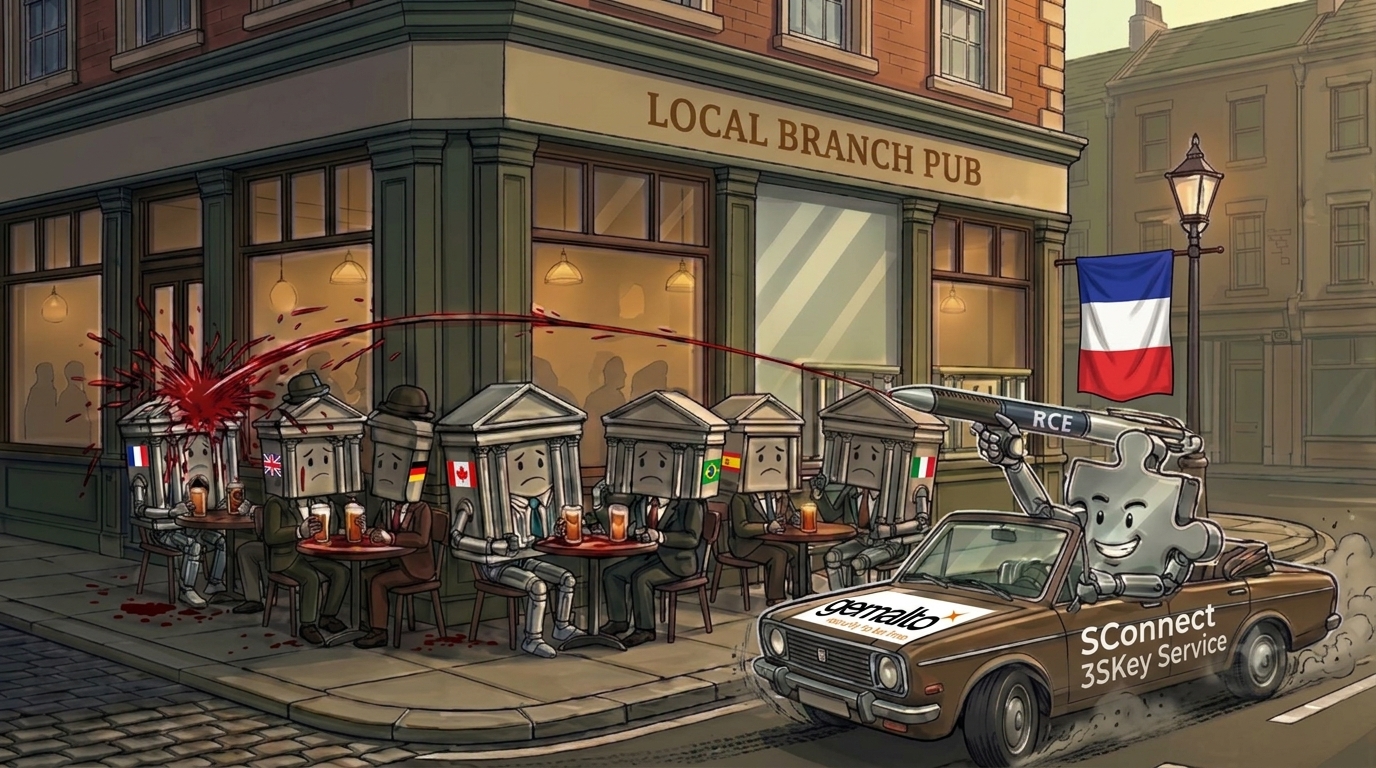 RCE Vulnerability in SConnect Affects Banks SConnect, an authentication middleware with over 1 million users, has a remote code execution (RCE) vulnerability (CVE-2026-18397) due to a flawed RSA-2048 token validation implementation. This flaw allows any site or iframe viewed by an user to silently download and execute a DLL, exploiting uninitialized memory…