 Securityaffairs.Co
Cybercriminals Exploit Expired Domains for Malware and Scams
Article Content

- •Cybercriminals are re-registering 65,000 expired domains daily for malicious use.
- •Sable Squirrel spent over $7 million on expired domains for illegal activities.
- •Repurposed domains pose a greater risk than newly registered domains due to retained trust.
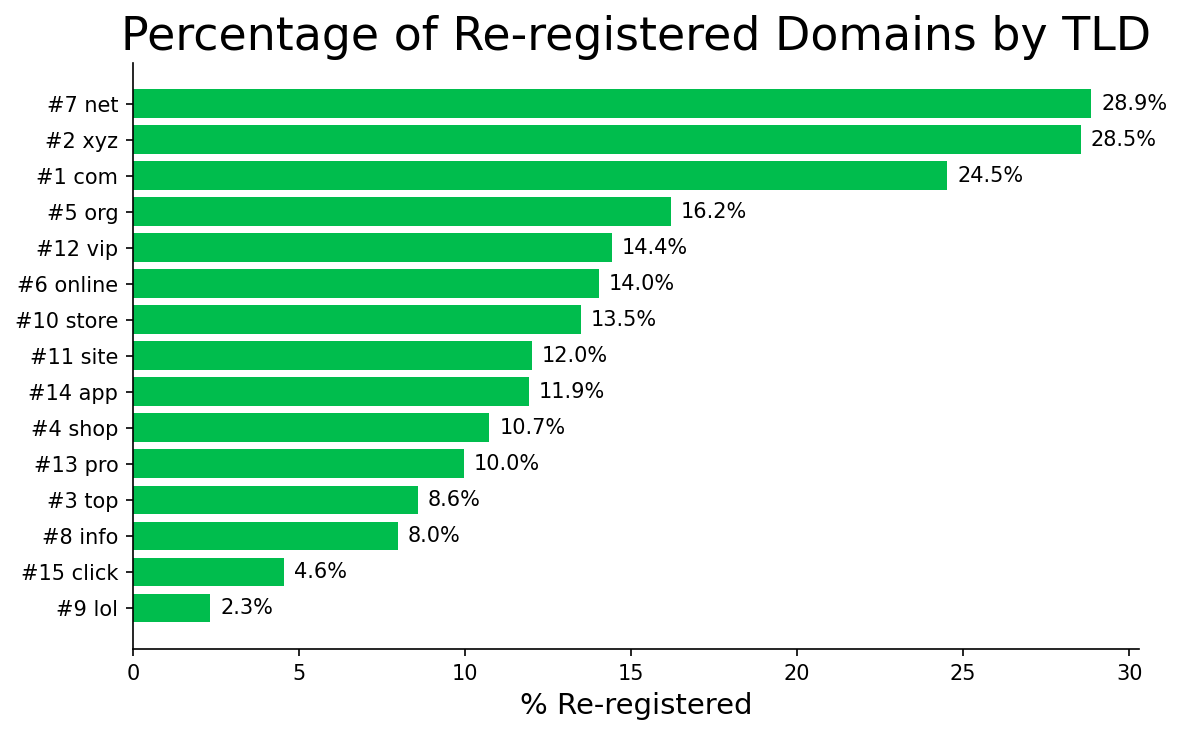
Cybercriminals are investing millions in expired domain names to facilitate various illicit activities, including malware distribution and scams. A report by Infoblox Threat Intel reveals that approximately 65,000 expired domains are re-registered daily, making them attractive to attackers due to their retained trust and traffic. Notable actors like Sable Squirrel have spent over $7 million on these domains for illegal streaming and malware command and control. The domains often host seemingly legitimate sites while serving as channels for malware such as Quasar RAT and HiddenTear ransomware. Another group, Shady Squirrel, is linked to the SocGholish infrastructure, delivering malware through scareware tactics. The repurposing of these domains poses a significant risk, potentially greater than newly registered domains.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track HiddenTear and Quasar RAT in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…