 Pv-Magazine
Cyber Attack on Polish Solar Plants Highlights Vulnerabilities in Energy Infrastructure
Article Content

- •30 solar energy sites in Poland were attacked with wiper malware targeting substation equipment.
- •Solar inverters remained untouched, indicating a shift in attack focus to broader energy systems.
- •Vulnerabilities exist in solar monitors and APIs, posing significant cybersecurity risks.
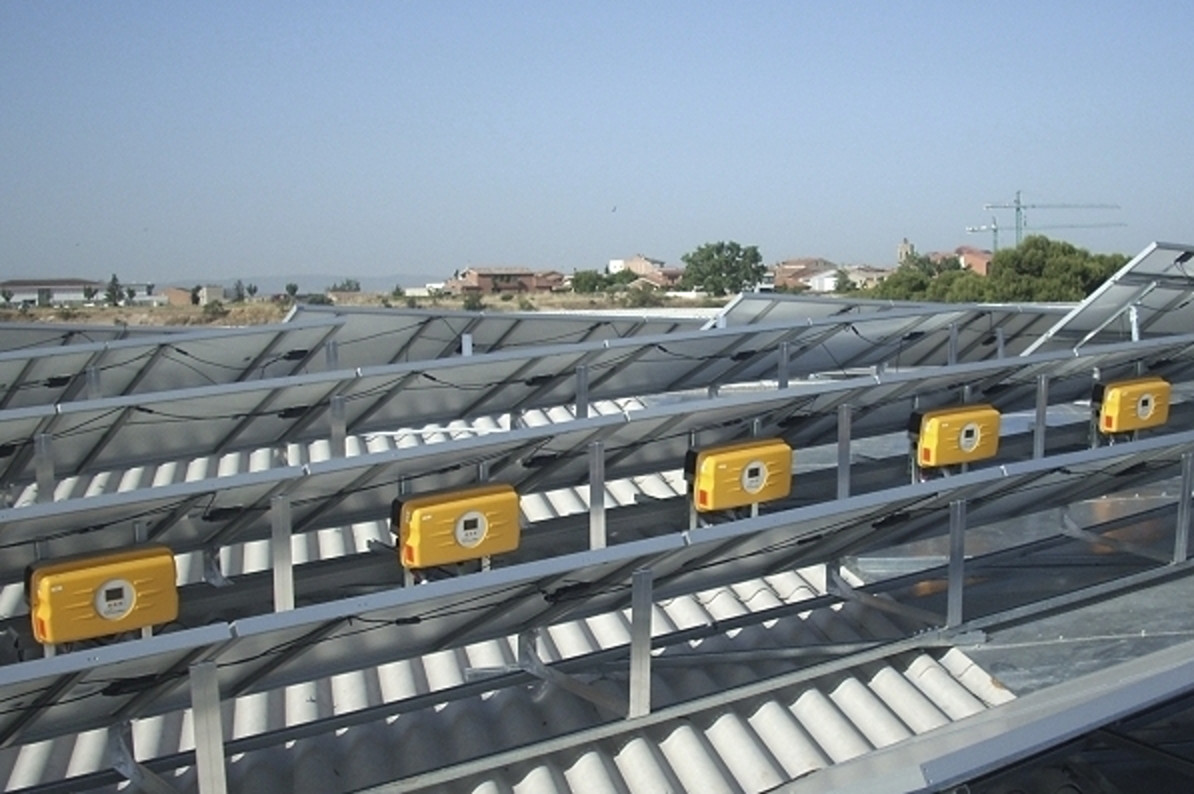
In late December 2025, a cyber attack targeted several solar plants in Poland, affecting 30 renewable energy sites. The attackers deployed wiper malware against substation equipment, leaving solar inverters untouched. This incident revealed that attackers are increasingly targeting the broader ecosystem of distributed energy resources rather than just individual devices. Although the attack did not lead to widespread blackouts, it highlighted vulnerabilities in solar monitors, APIs, and mobile applications that communicate with solar equipment. Backhaul communication channels, such as SSH and HTTPS, are potential entry points for attackers, raising significant cybersecurity concerns. The incident underscores the need for improved security measures across the solar energy sector, as many systems still utilize unencrypted interfaces. Industry experts are calling for enhanced cybersecurity protocols to protect against similar threats in the future.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…