 Nation.Cymru
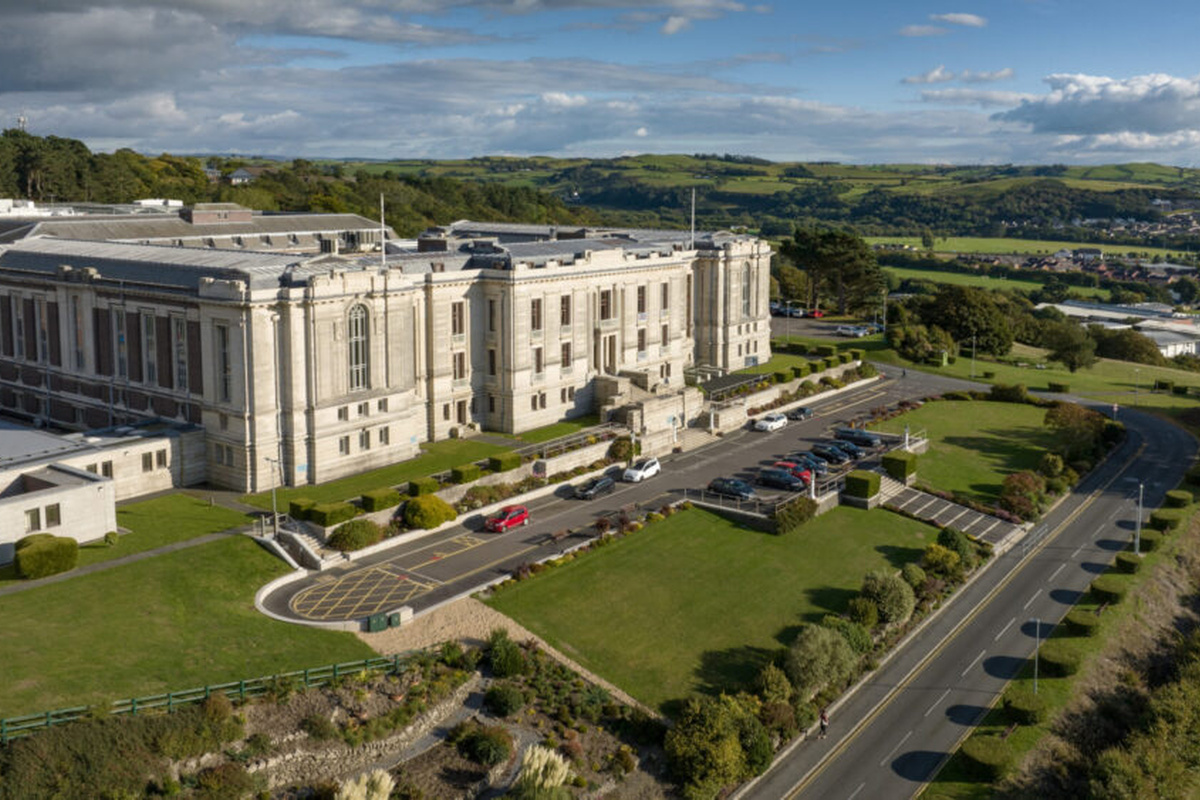
Cyber Security Risks Highlighted at National Library of Wales
Article Content

- •Cyber security is the primary risk for the National Library of Wales.
- •The British Library's 2023 cyber breach remains unresolved, impacting its systems.
- •The National Library is collaborating with NCSC to enhance its cyber resilience.
Cyber security is the top concern on the National Library of Wales' risk register, as stated by Chief Executive Rhodri Llwyd Morgan during a scrutiny session on October 19, 2026. This follows a significant cyber breach at the British Library in October 2023, which has left their systems unrecoverable. The National Library is actively addressing technological risks, including the closure of legacy systems, and is collaborating with the National Cyber Security Centre (NCSC) for monthly briefings. The library is also facing challenges from bots attempting to scrape its collections for AI purposes. The library's president, Ashok Ahir, emphasized the need for digital preservation and the expansion of its collections, which are mandated by law. The library is exploring a second location to manage its growing collection and improve resilience against cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track British Library in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific cyber threats is the library facing?
How is the library improving its cyber security?
What is the impact of the British Library's breach?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell to Root 25 Servers Cybersecurity firm Dream reported that a China-linked threat actor exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) and a Linux kernel privilege escalation flaw (CVE-2026-46300) to gain root access to 25 servers, including three in a U.S. government-affiliated environment. The attackers used…
 Brotli Decoder Vulnerability Patched Across Multiple Linux Distributions A vulnerability, CVE-2026-111497, affecting the Brotli decoder has been patched in various Linux distributions, including Fedora 44 and Oracle Linux 10. The flaw allows for an out-of-bounds write, which could potentially enable attackers to execute arbitrary code. The vulnerability was published on October 22, 2026…