 Securityaffairs.Co
Cybercriminals Target Trucking Firms for Cargo Theft via Digital Intrusions
Article Content

- •Cybercriminals are exploiting logistics systems to steal physical cargo shipments.
- •The collaboration between organized crime and cybercriminals is increasing the scale of theft.
- •Trucking and freight companies are facing significant financial losses due to these attacks.
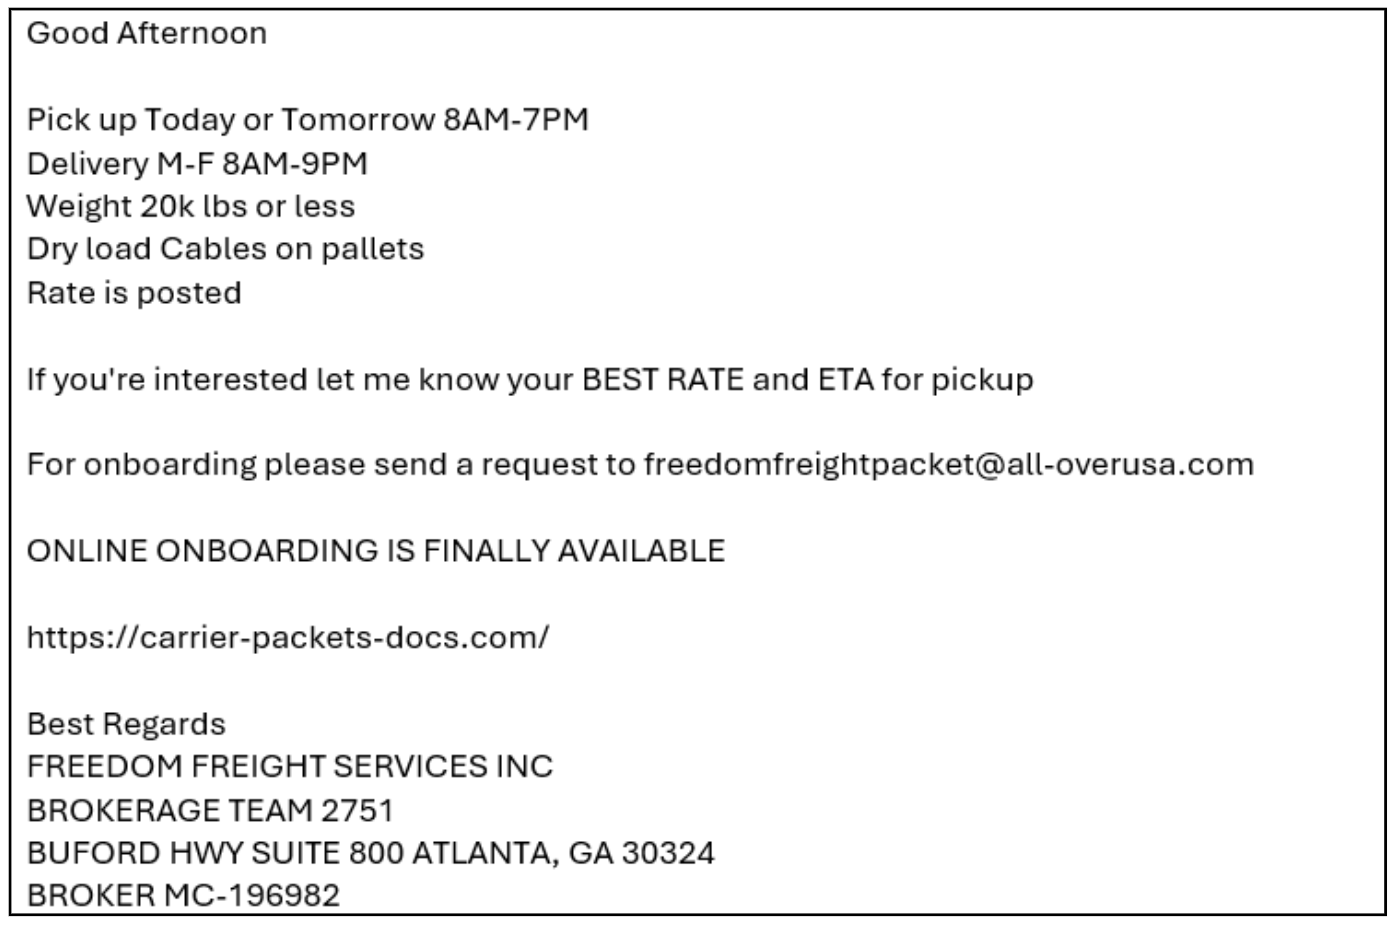
A surge in cyber attacks against trucking and freight companies has been reported, where hackers are infiltrating logistics systems to steal physical cargo shipments. Organized crime rings are collaborating with cybercriminals to exploit vulnerabilities in the systems used by carriers and freight brokers. This new method of cargo theft is transforming traditional theft into a digital-first operation, affecting numerous firms in the logistics sector. The financial impact is significant, with stolen shipments valued in the millions. While cargo theft is not a new crime, the scale and sophistication of these attacks represent a growing concern for the industry. The current status indicates that these attacks are ongoing, with no immediate resolution in sight. Companies are urged to enhance their cybersecurity measures to protect against these threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (18)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…