 Da.Za
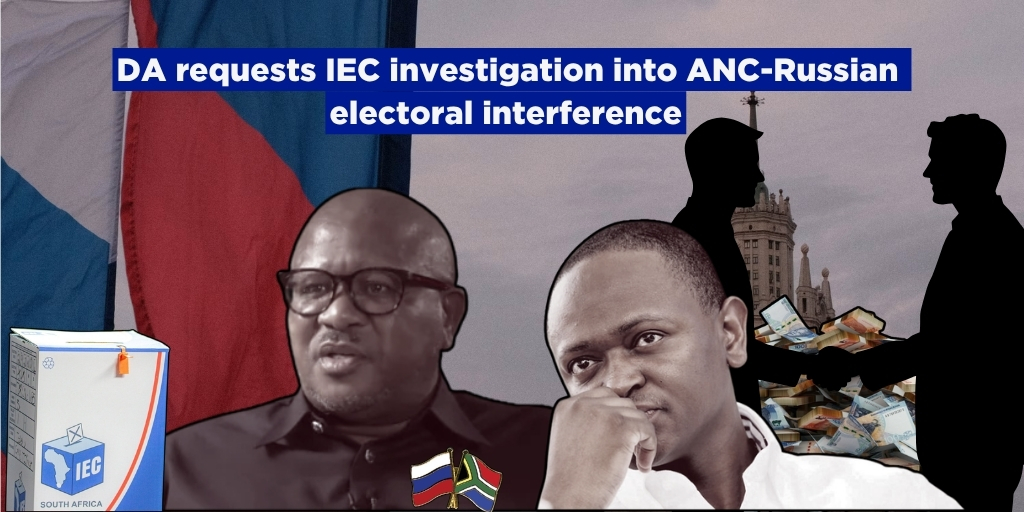
DA Calls for IEC Investigation into ANC-Russian Disinformation Operations
Article Content

- •DA requests IEC investigation into ANC's alleged collusion with Russian SVR.
- •Leaked documents indicate targeted disinformation campaigns against opposition parties.
- •Allegations include electoral interference during the 2024 elections and earlier.
The Democratic Alliance (DA) has formally requested an investigation by the Independent Electoral Commission (IEC) into allegations of collusion between the African National Congress (ANC) and the Russian Foreign Intelligence Service (SVR). Reports suggest that ANC officials, including Secretary General Fikile Mbalula, engaged in secret meetings with SVR representatives in 2024 to orchestrate disinformation campaigns aimed at undermining opposition parties in South Africa. Leaked SVR documents reveal a coordinated effort to manipulate public perception through fabricated scandals and smear campaigns targeting DA leaders. This alleged interference is said to have influenced the 2024 National and Provincial Elections, with operations dating back to 2019. The DA's request follows the South African government's refusal to take diplomatic action against Russia, which they view as a significant conflict of interest. The IEC is now tasked with reviewing the DA's formal complaint.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Russian Foreign Intelligence Service and African National Congress in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 KeyDrift Malware Exploits Cisco SD-WAN Flaw CVE-2026-20127 Cisco Talos reported that the advanced persistent threat group UAT-11473 exploited a critical authentication bypass vulnerability (CVE-2026-20127) in Cisco SD-WAN Catalyst Controllers. This flaw, which has a CVSS score of 10.0, allows unauthorized remote access to administrative privileges. The group deployed a custom…