 Newsmeter.In
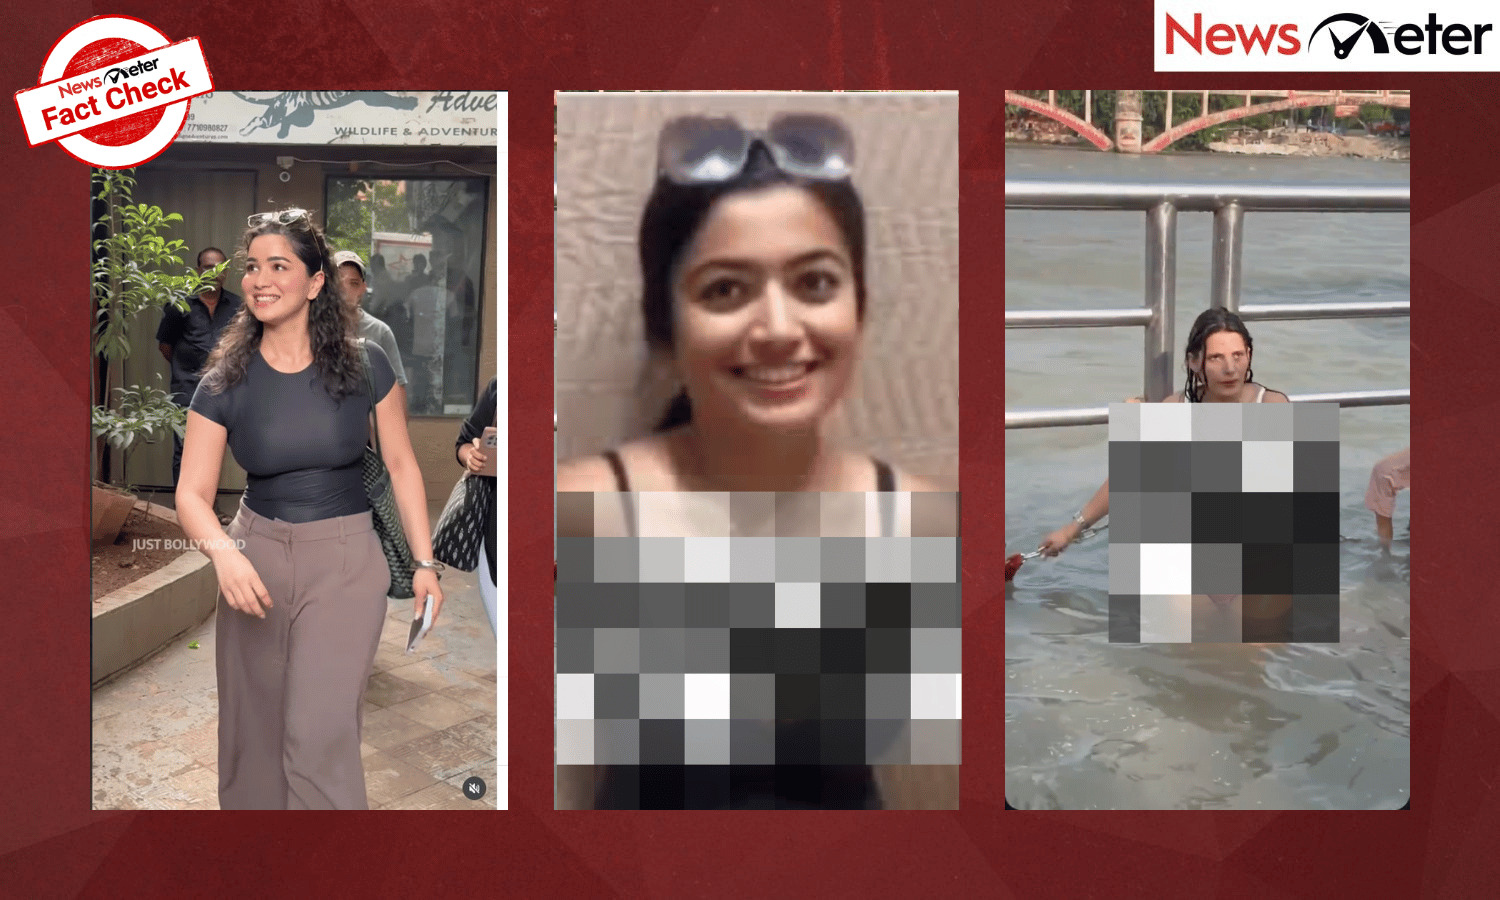
Deepfake Video of Woman in Ganga Sparks Outrage
Article Content

- •A deepfake video of Sonam Yadav was manipulated to show her inappropriately dressed.
- •The incident illustrates the dangers of synthetic media, particularly for women.
- •Yadav has filed a complaint with the cyber cell against those circulating the altered video.
A manipulated video of social media influencer Sonam Yadav taking a dip in the Ganga was circulated online, falsely depicting her as semi-naked. The original footage showed her in a salwar suit, but the altered version incited moral outrage and led to her filing a complaint with the cyber cell. This incident highlights the growing issue of deepfakes and manipulated content, particularly targeting women. The spread of the video prompted significant backlash on social media, with users expressing outrage over the perceived behavior of the woman in the religious context. Yadav urged people not to share the altered video and indicated that legal action would be pursued against those distributing it. The incident reflects broader concerns about the misuse of synthetic media for harassment and misinformation. Under India's 2026 IT Rules, there are new requirements addressing unlawfully generated synthetic content. A survey indicated that half of respondents encountered fake videos in the past year.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization. Both…