 Channelnewsasia
Delay in Air India Crash Report Raises Concerns Among Pilots and Families
Article Content

- •The AAIB will miss the one-year deadline for the final crash report due to ongoing investigations.
- •The Federation of Indian Pilots has criticized the decision to release an interim report instead of a final one.
- •Preliminary findings indicate potential pilot error related to fuel control switches before the crash.
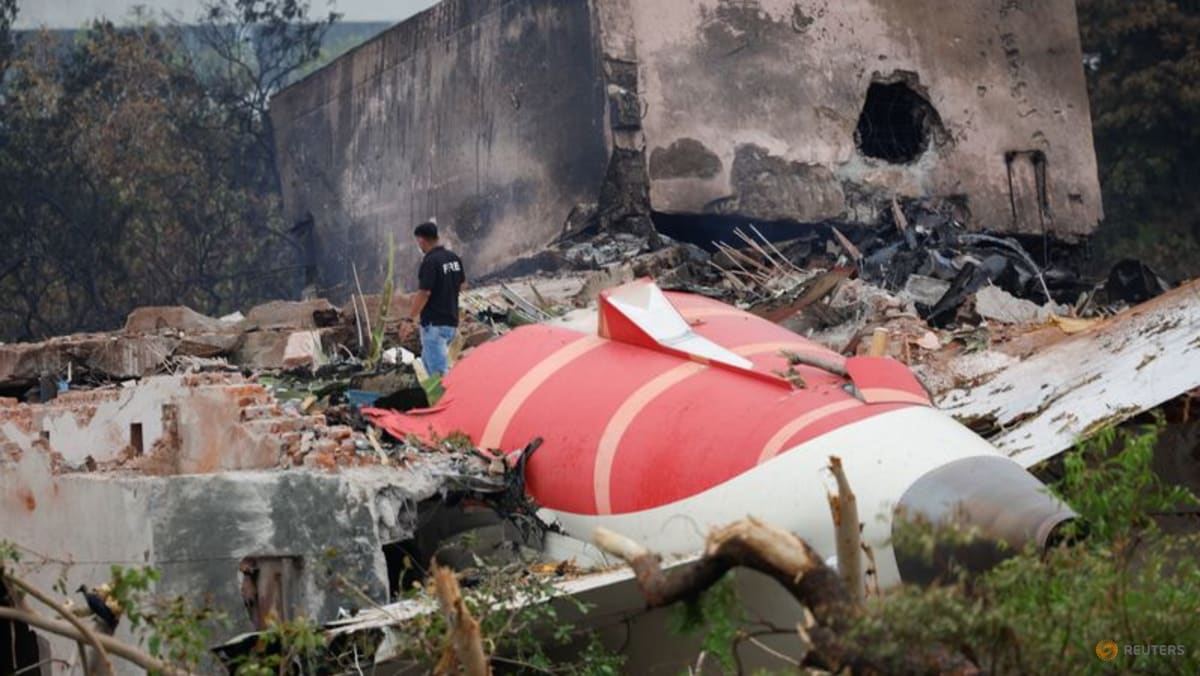
The investigation into the Air India flight AI-171 crash, which killed 261 people on June 12, 2025, is facing delays due to unfinished examinations of the Boeing 787's engines in the U.S. The Aircraft Accident Investigation Bureau (AAIB) is expected to issue an interim report instead of a final one, which has prompted criticism from the Federation of Indian Pilots. They argue that the interim report could lead to confusion and speculation regarding the cause of the crash, which preliminary findings suggest may involve pilot error. The AAIB's preliminary report indicated that the aircraft's fuel control switches moved to the cutoff position just before the crash, but did not determine the cause of this switch movement. Families of the victims are demanding clarity and accountability as they await answers. An interim report is anticipated to be released on June 12, 2026, marking the one-year anniversary of the crash.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (8)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…