 Civicmedia.Us
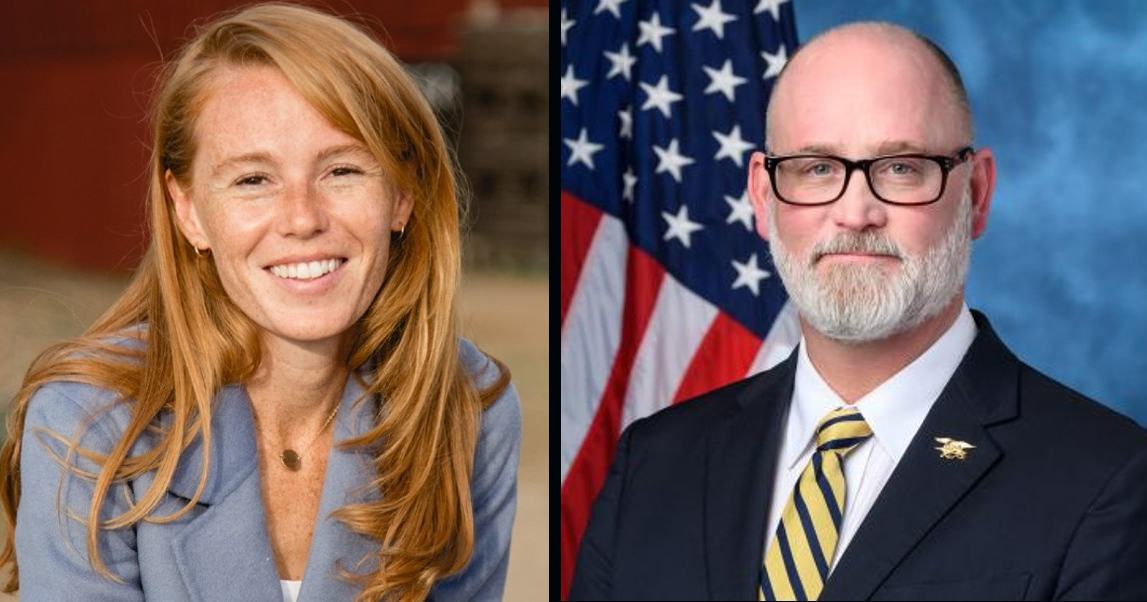
Dem Candidate Cooke Takes Legal Action Over AI Deepfake Ads by Van Orden
Article Content

- •Rebecca Cooke issued a cease-and-desist letter to Derrick Van Orden over deepfake videos.
- •The videos falsely attribute controversial statements to Cooke, misleading voters.
- •Cooke's campaign is monitoring Van Orden's social media for further legal action.
Rebecca Cooke, a Democratic candidate for Congress in Wisconsin, has issued a cease-and-desist letter to her Republican opponent, Derrick Van Orden, over his use of AI-generated deepfake videos that falsely depict her making controversial statements. The videos, which have been shared on social media, attribute fabricated quotes to Cooke, including claims about illegal immigration and healthcare that she never made. Cooke's legal team argues that these deepfakes violate Wisconsin law against defamation and mislead voters. In response, Van Orden has continued to post similar content, prompting Cooke to warn of potential legal actions if the behavior persists. The race is closely watched, with polls showing Cooke slightly ahead of Van Orden. This incident highlights the growing concern over the use of AI in political campaigns and its potential to distort public perception.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific statements are attributed to Cooke?
What legal grounds does Cooke have for her cease-and-desist?
What actions will Cooke's campaign take if Van Orden continues?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…