 www.cbsnews.com
DHS Criticizes CBS for Omitting Key Fraud in Deportation Profile
Article Content

- •DHS claims Moussa Diawara's asylum application included fraudulent information.
- •CBS's '60 Minutes' segment omitted key details about Diawara's deportation.
- •Diawara was deported to Ghana but quickly sent back to Mali, raising concerns about third-country deportations.
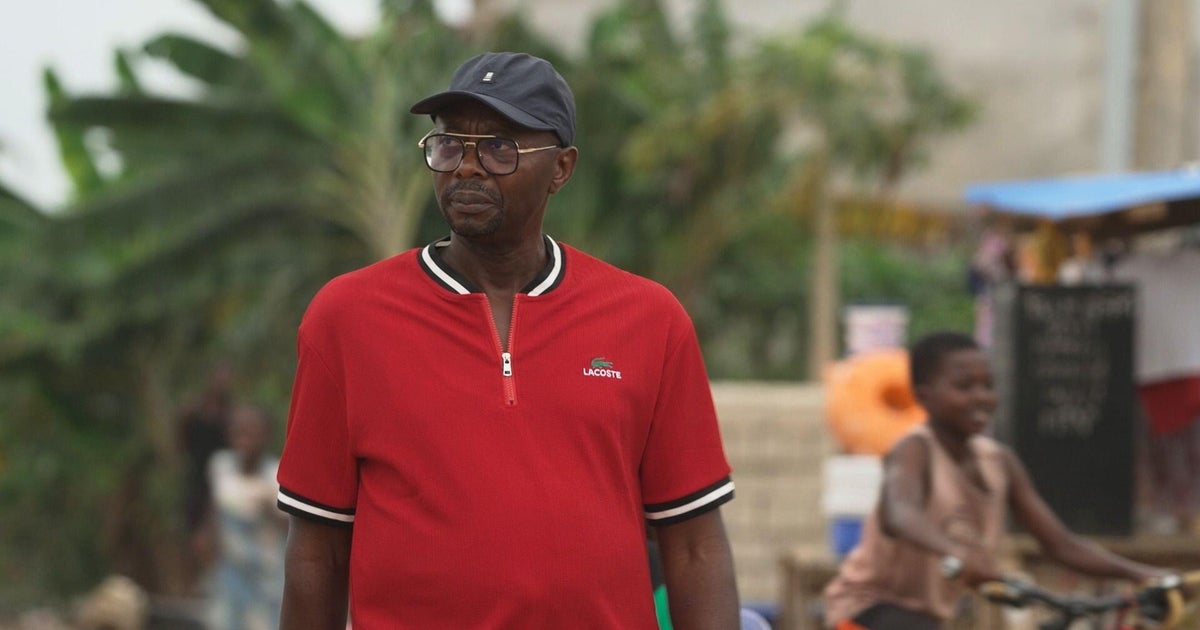
The Trump administration criticized CBS's '60 Minutes' for not mentioning a crucial detail in the deportation story of Moussa Diawara, a Malian immigrant. Diawara was deported to Ghana after overstaying a tourist visa and claiming asylum based on his alleged homosexuality. The Department of Homeland Security (DHS) claims Diawara's asylum application included fraudulent claims, as he is married to a woman and has two children. DHS General Counsel James Percival highlighted this discrepancy on social media, stating that Diawara's case exemplifies immigration fraud. CBS's report focused on Diawara's struggles after deportation, including being sent back to Mali shortly after arriving in Ghana. The segment did not address the alleged fraud in Diawara's asylum claim, leading to the administration's backlash. The DHS maintains that Diawara's deportation was lawful and justified based on his immigration history.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the basis for Diawara's asylum claim?
Why did DHS criticize CBS's report?
What happened to Diawara after his deportation?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…