 Npr
Iran-Linked Cyberattacks Target U.S. Water Systems Amid Ongoing Conflict
Article Content
Browse articles 
- •At least seven U.S. states experienced cyberattacks on water systems.
- •The FBI is investigating potential links to the war in Iran.
- •No specific attack methods or tools have been disclosed yet.
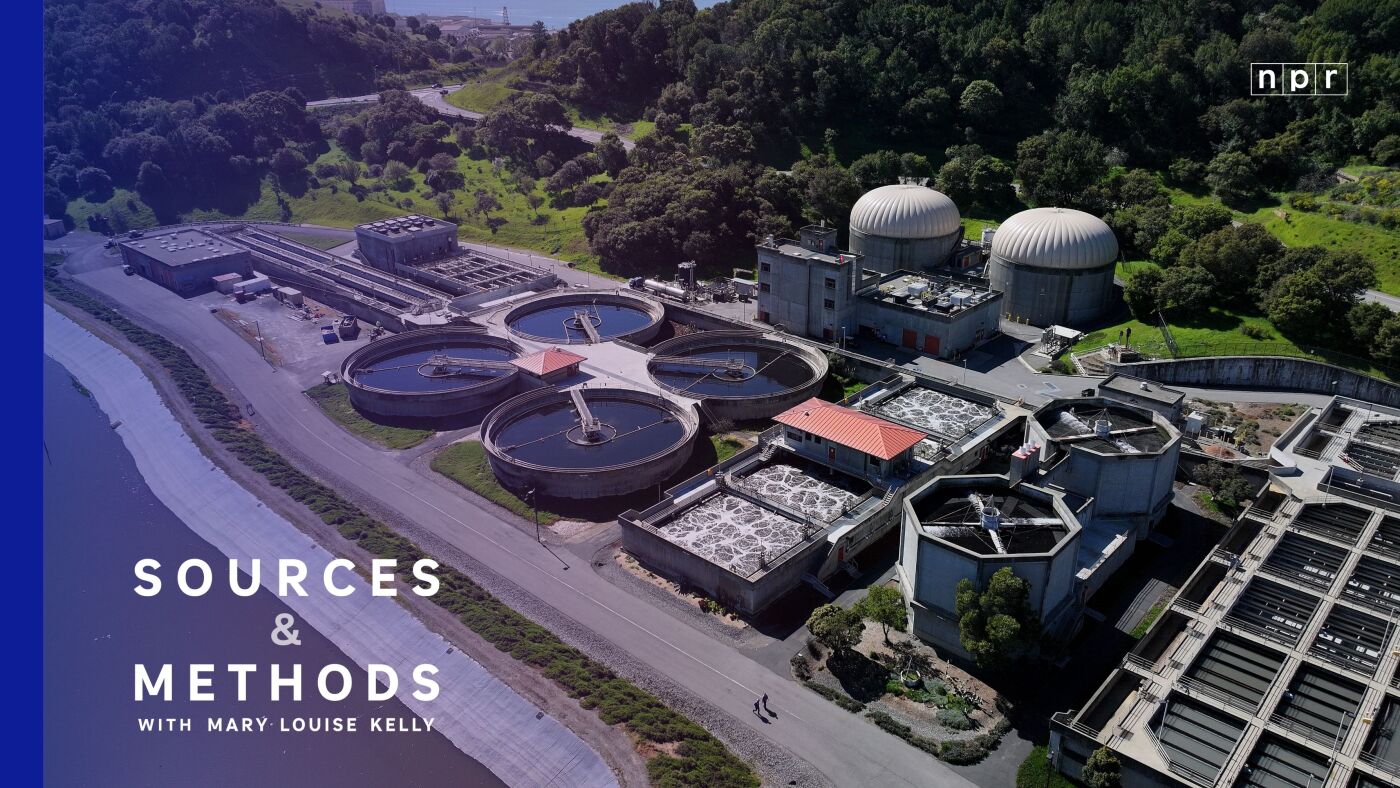
Recent cyberattacks have targeted water systems in at least seven U.S. states, potentially linked to the ongoing war in Iran. The FBI is investigating these incidents, which raise concerns about the security of critical infrastructure. Specific attack methods and tools have not been disclosed, but the scale of the attacks suggests a coordinated effort. The situation remains under investigation, with no confirmed attribution to Iranian state actors yet. The attacks highlight vulnerabilities in U.S. water systems and the potential for further escalation in cyber warfare. Authorities are urging vigilance in monitoring and securing critical infrastructure against such threats.
Ask AI about this cluster
Answers cite the sources they use
Updated 45d ago How this analysis works
Timeline
2026-08-07
FBI launches investigation
The FBI confirmed it is investigating the cyberattacks for possible connections to the ongoing conflict in Iran.
NprRecent
Cyberattacks on U.S. water systems reported
At least seven states experienced cyberattacks targeting their water systems, prompting an FBI investigation.
NprMore articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…