 Cbsnews
DOJ Charges James Comey Again Under Espionage Act
Article Content

- •James Comey faces new charges under the Espionage Act for alleged leaks in 2016.
- •This is the third attempt by the DOJ to prosecute Comey, who maintains his innocence.
- •Comey's defense argues that the charges are time-barred and previously investigated without indictment.
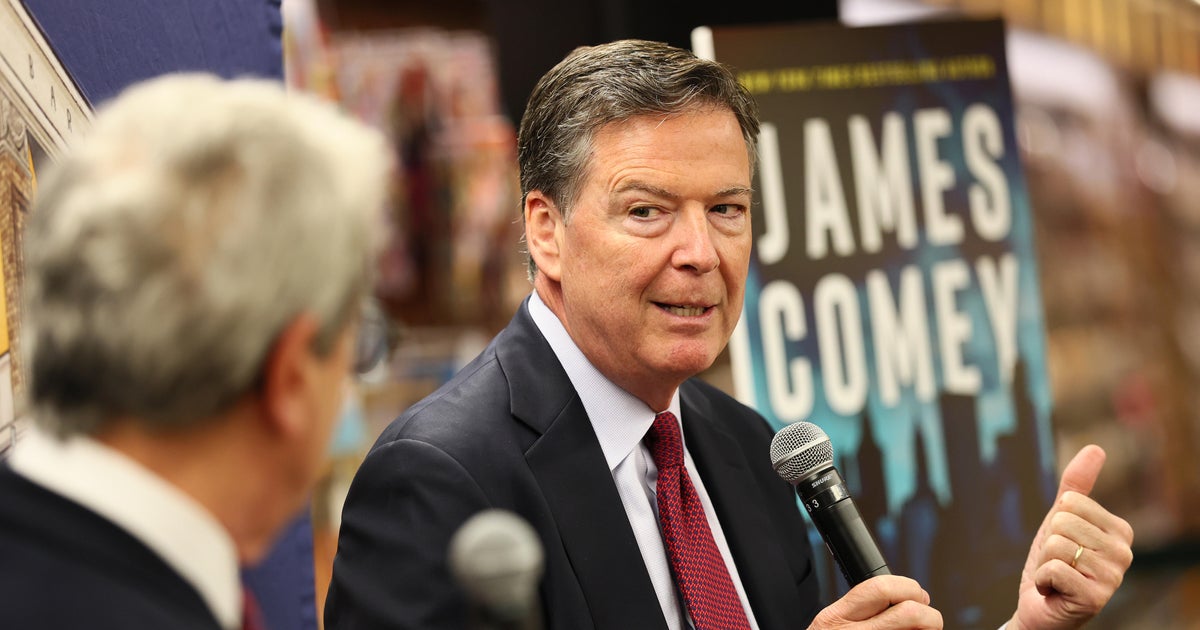
The Justice Department has filed new charges against former FBI Director James Comey, alleging he leaked classified information to a New York Times reporter in 2016. The charges, which include two counts of violating the Espionage Act, were filed to extend the statute of limitations. Comey's attorney has dismissed the allegations as invalid and outside the legal time limit for prosecution. This marks the third attempt to charge Comey, who has consistently maintained his innocence. The case revolves around a New York Times article published on October 5, 2016, that discussed Yahoo's assistance with U.S. email surveillance. Comey's defense argues that previous investigations during the Trump administration found no basis for charges. The DOJ claims that Comey directed staff to correct misinformation in a Reuters article, leading to the alleged disclosure. The case is currently ongoing, with Comey's legal team seeking dismissal of the charges.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (13)
Common questions
What are the specific charges against Comey?
What is Comey's defense strategy?
What happens next in this case?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…