 United24Media
Drone Strike Targets Russian Chemical Plant Linked to Missile Production
Article Content

- •The Redkinsky Experimental Chemical Plant was attacked by drones on October 9, 2026.
- •The facility produces components for Russian cruise missiles and is linked to the defense industry.
- •No injuries were reported, and the fire caused by the attack was extinguished by emergency crews.
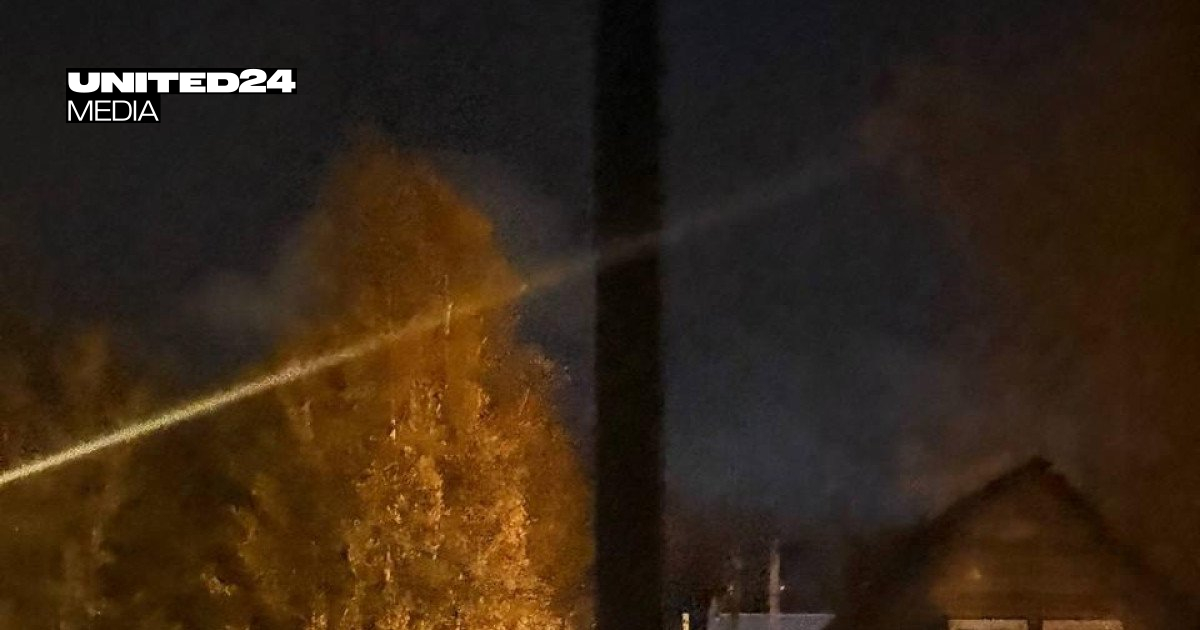
On October 9, 2026, a drone strike hit the Redkinsky Experimental Chemical Plant in Tver, Russia, causing explosions and a fire. The facility is known for producing fuel components for Kh-55 and Kh-101 cruise missiles, as well as additives for diesel and aviation fuels. Ukrainian monitoring channel Exilenova+ reported the attack, which was confirmed by local authorities. No injuries were reported, and emergency crews extinguished the fire. This plant plays a crucial role in Russia's defense industry, and its previous attacks have raised concerns about Ukraine's long-range strike capabilities. The UK had previously sanctioned the plant for its strategic importance to the Russian military-industrial base. This incident highlights the ongoing conflict and the targeting of critical infrastructure in the war.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Redkino Experimental Chemical Plant in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the significance of the Redkinsky Plant?
Were there any casualties from the drone strike?
What has been the response to this attack?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…