 www.autonomyglobal.co
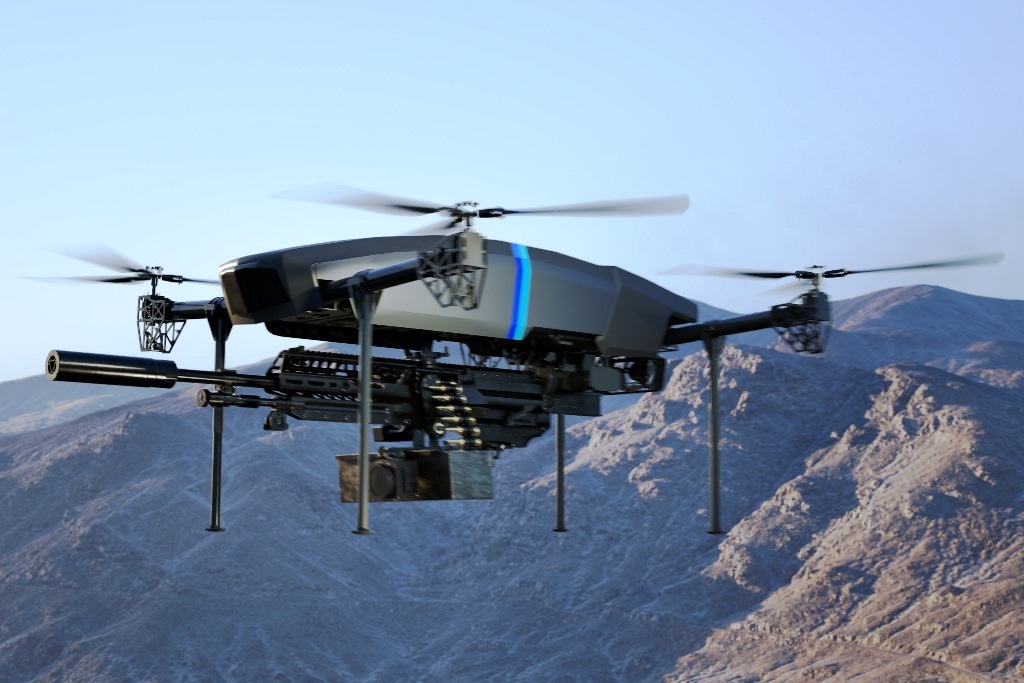
IAI and SIG SAUER Test Armed Drone with M250 Machine Gun
Article Content

- •The FIRE STORM 250 drone can engage targets from the air using the M250 machine gun.
- •It can remain airborne for up to three hours and is designed for close support operations.
- •The system integrates advanced targeting algorithms and is intended for use in austere environments.
Israel Aerospace Industries (IAI) and SIG SAUER conducted a live-fire demonstration of the FIRE STORM 250, a tactical unmanned aerial system (UAS) equipped with the M250 machine gun. The test, held in Israel, showcased the drone's ability to identify and engage targets from the air using both single-shot and semi-automatic firing modes. The drone can remain airborne for up to three hours and is designed for armed reconnaissance and close support for small units. It incorporates advanced control algorithms for accurate targeting while hovering. The M250 can carry 200 rounds of ammunition and is adaptable to different calibers. The system is intended for use in austere environments, requiring minimal logistical support. The demonstration precedes the AUSA 2026 exhibition in Washington, highlighting the rapid development of this technology.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track SIG Sauer in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the purpose of the FIRE STORM 250?
How long can the drone stay airborne?
What type of ammunition does the M250 use?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…