 siliconangle.com
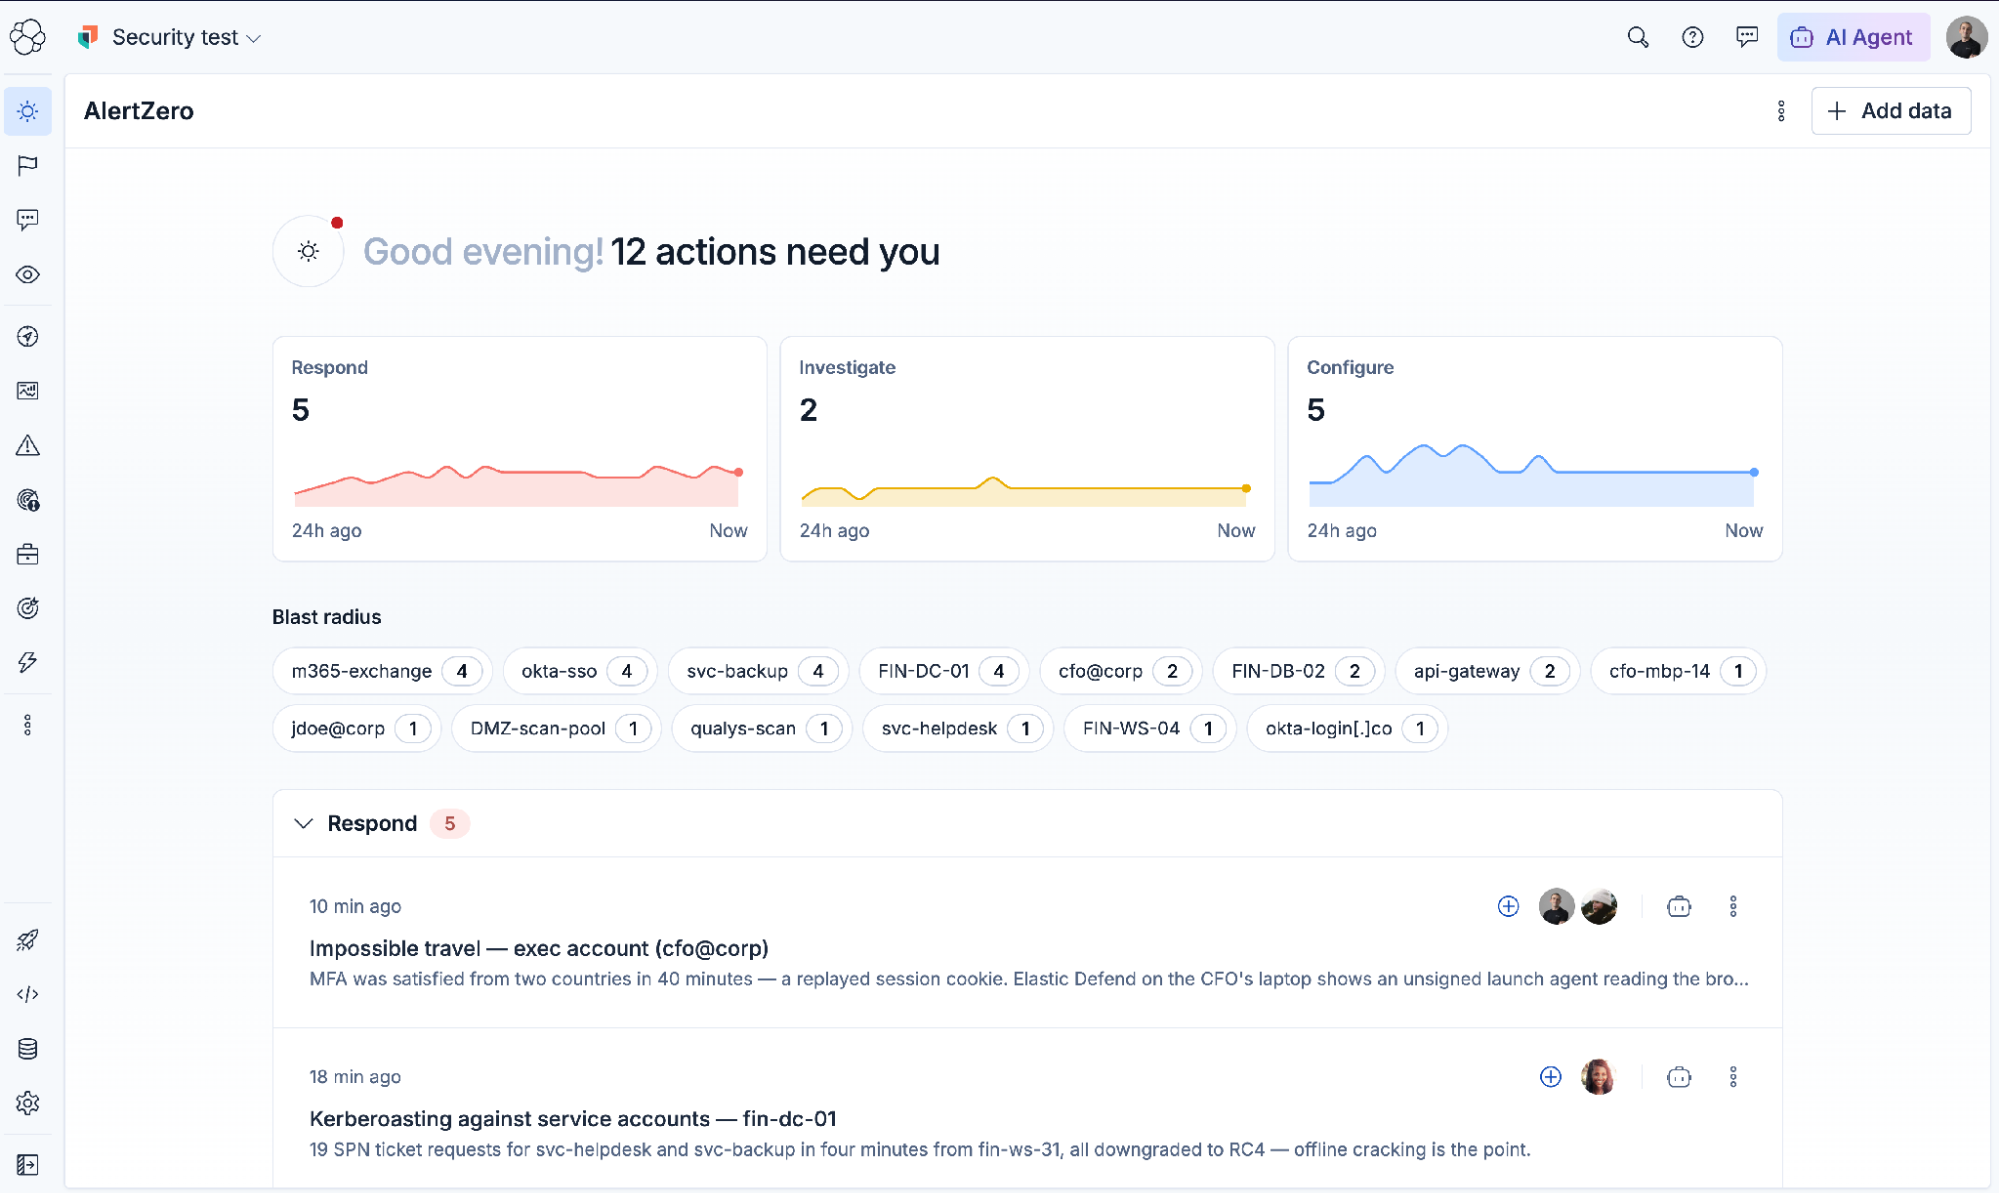
Elastic Launches AI Agents to Tackle Security Alert Overload
Article Content

- •Elastic's AlertZero aims to reduce alert fatigue in security operations.
- •The system features four AI agent groups, each with specific roles.
- •Customers can customize the level of automation for security tasks.
Elastic N.V. has launched AlertZero, a suite of AI agents aimed at automating security operations. The agents are integrated into Elastic Security and handle tasks like alert triage, threat hunting, and forensic analysis. This initiative addresses the issue of alert overload in security operations centers, worsened by the use of AI by attackers. The system includes four groups of agents, called Watches, each responsible for different tasks such as processing alerts and conducting threat hunting. Customers can control the level of autonomy for each agent, ensuring human oversight for inconclusive findings. The introduction of AlertZero follows a notable incident where an attack on Hugging Face Inc. generated over 17,000 alerts in four days, highlighting the need for enhanced automation in security operations. The offering is currently available as a technical preview.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What tasks can AlertZero handle?
How does AlertZero address alert overload?
Is human oversight required with AlertZero?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…