 Ransomware.Live
Emperador Ransomware Targets AB InBev, Demands $1M Ransom
Article Content

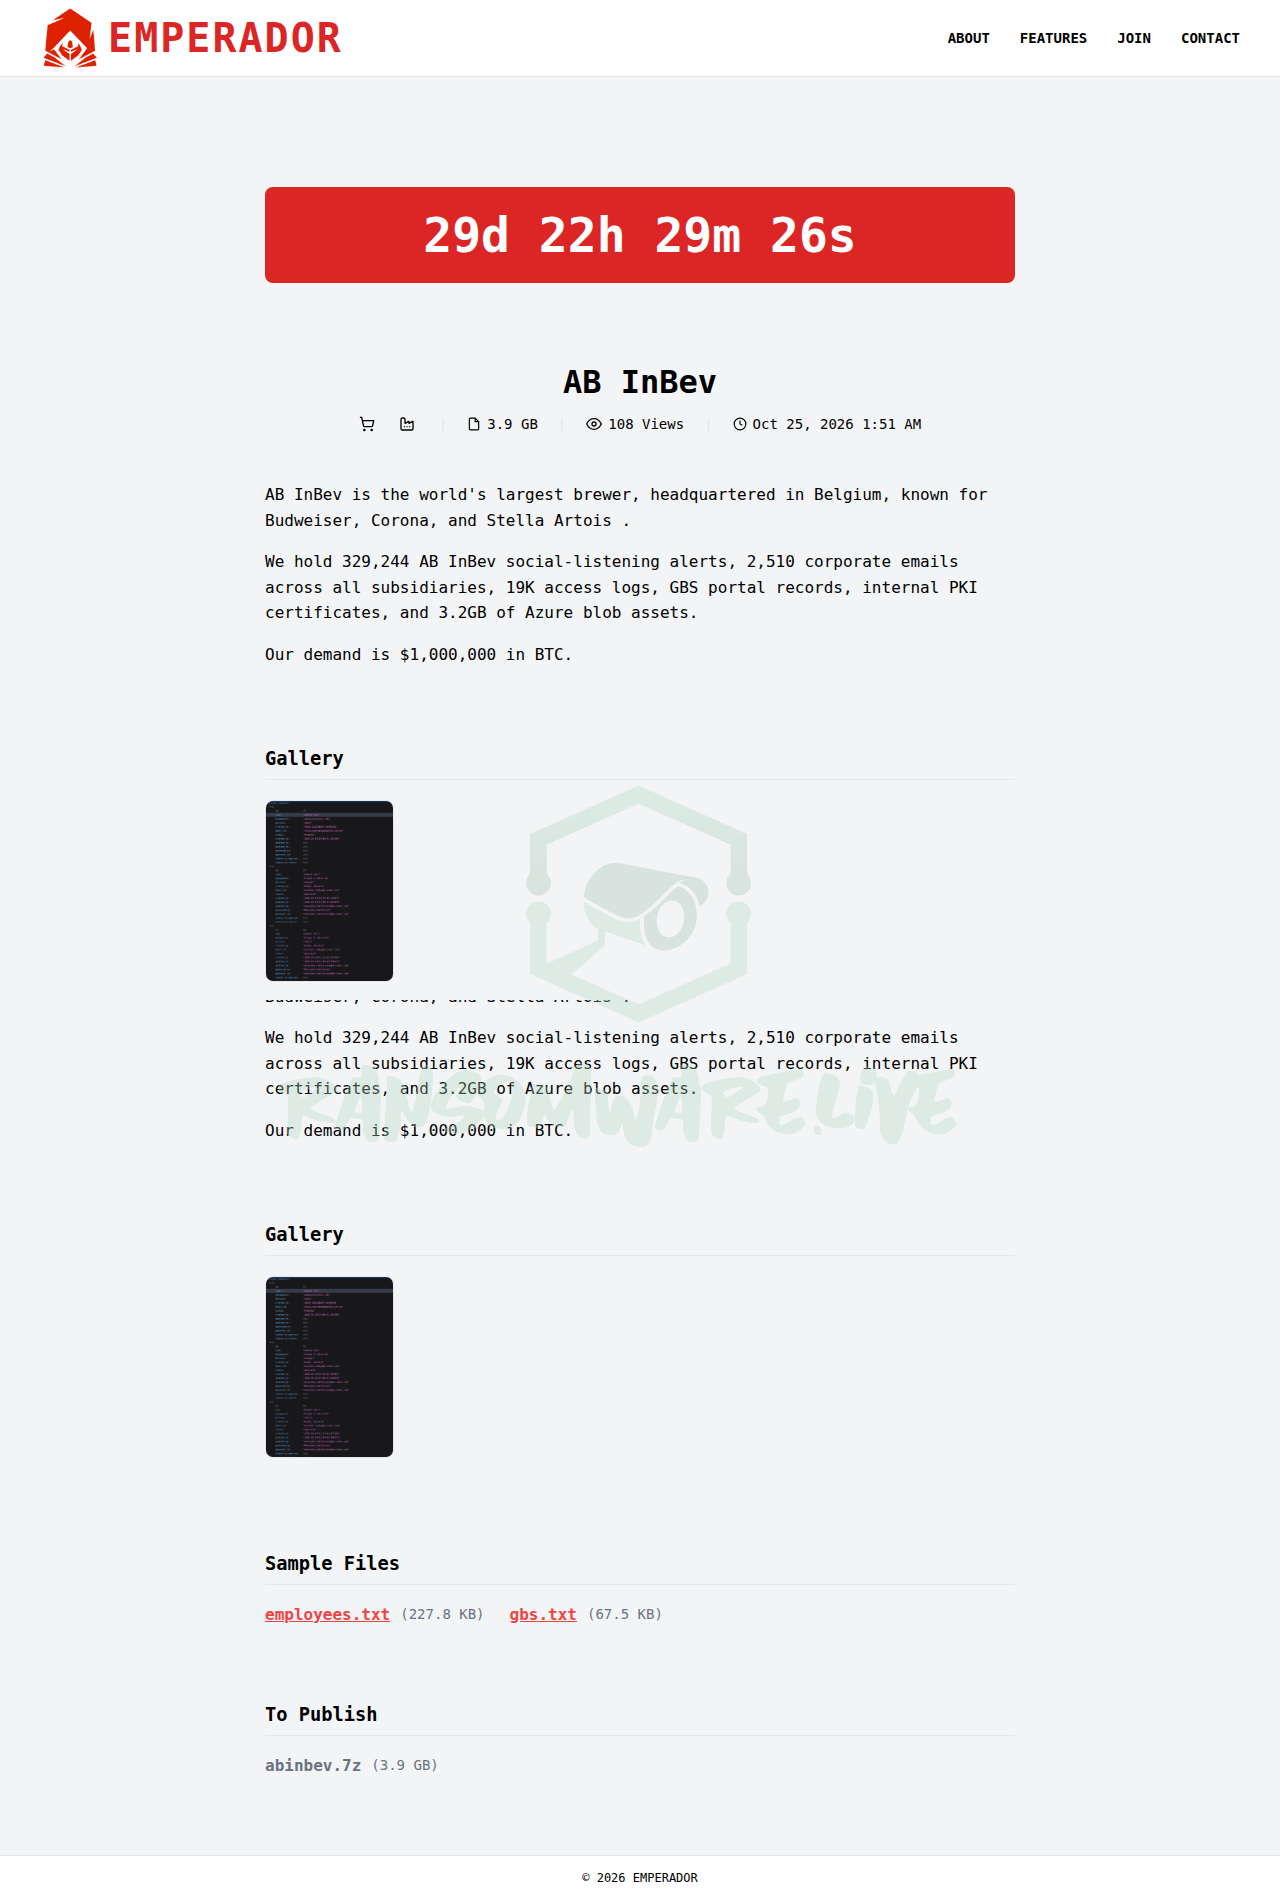
- •Emperador ransomware claims to have breached AB InBev, demanding $1M in Bitcoin.
- •The group claims to possess 3.9 GB of data, including corporate emails and access logs.
- •AB InBev has not confirmed any breach, and the authenticity of the claims remains unverified.
The Emperador ransomware group has claimed responsibility for a cyber incident involving AB InBev, the world's largest brewer. They have reportedly added the company to their leak site, claiming to possess 3.9 GB of data, including 2,510 corporate emails and 19,000 access logs. The group is demanding a ransom of $1 million in Bitcoin, with a deadline set for November 23. The authenticity of the data has not been independently verified, and AB InBev has not confirmed any breach. The data appears to focus on marketing and cloud storage rather than brewing operations. If the internal PKI certificates are valid, they would require revocation and rotation to mitigate potential risks. Partners and employees are advised to be vigilant for AB InBev-themed phishing attempts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Emperador and AB InBev in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Has AB InBev confirmed the breach?
What type of data was reportedly stolen?
What should AB InBev do to mitigate risks?
Continue Reading
 Emperador Ransomware Targets OnTrac with Employee Data Theft Claims The Emperador ransomware group has claimed a new attack against OnTrac, a major U.S. parcel carrier, alleging the theft of approximately 197,000 employee records and demanding a ransom of $1 million. This claim follows a previously confirmed network breach at OnTrac that occurred between March 20-22, 2026, where…
 Imperial Diamond Jewellery Listed as Ransomware Victim by Emperador Group On October 9, 2026, the Emperador ransomware group publicly listed Imperial Diamond Jewellery as a victim of their attack. The Hong Kong-based company specializes in precious-metal and diamond jewellery. The group claims that financial documents and personal customer data were compromised, but details regarding system…