 www.nanosats.eu
ESA Launches CyberCUBE for In-Orbit Cybersecurity Testing
Article Content

- •CyberCUBE is ESA's first satellite dedicated to cybersecurity experiments in orbit.
- •The satellite will conduct various cyber-defense experiments, including detecting unauthorized commands.
- •ESA invites researchers to propose experiments, enhancing collaboration in space cybersecurity.
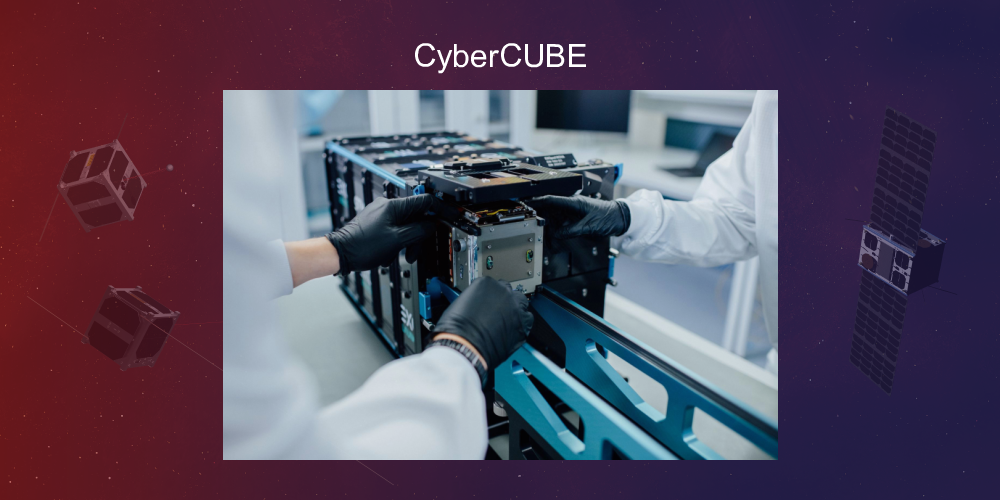
The European Space Agency (ESA) successfully launched CyberCUBE, a 3U CubeSat designed for live cyber-defense experiments in orbit, on July 7, 2026. This mission, led by GMV's Romanian subsidiary, aims to validate cybersecurity measures for space-based assets against emerging threats. CyberCUBE will conduct experiments to detect unauthorized commands, identify radio-frequency jamming, and test post-quantum cryptographic algorithms. ESA has opened a call for ideas, inviting researchers to propose experiments utilizing CyberCUBE's capabilities. The satellite operates at an altitude of 590 to 600 kilometers in a sun-synchronous orbit, equipped with advanced technologies like a reprogrammable FPGA and a software-defined radio. The mission is expected to last at least a year, providing valuable data for future ESA missions. This initiative marks a significant step in enhancing the resilience of space assets against cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What is CyberCUBE?
How long will CyberCUBE operate?
Who can propose experiments for CyberCUBE?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…