 Breakingdefense
EU Proposes Emergency Protocol for Hybrid Threats and Cyberattacks
Article Content

- •EU proposes a new emergency response protocol for hybrid threats.
- •The mechanism allows any member state to summon a meeting of all EU governments.
- •Recent incidents in several EU countries highlight the need for this initiative.
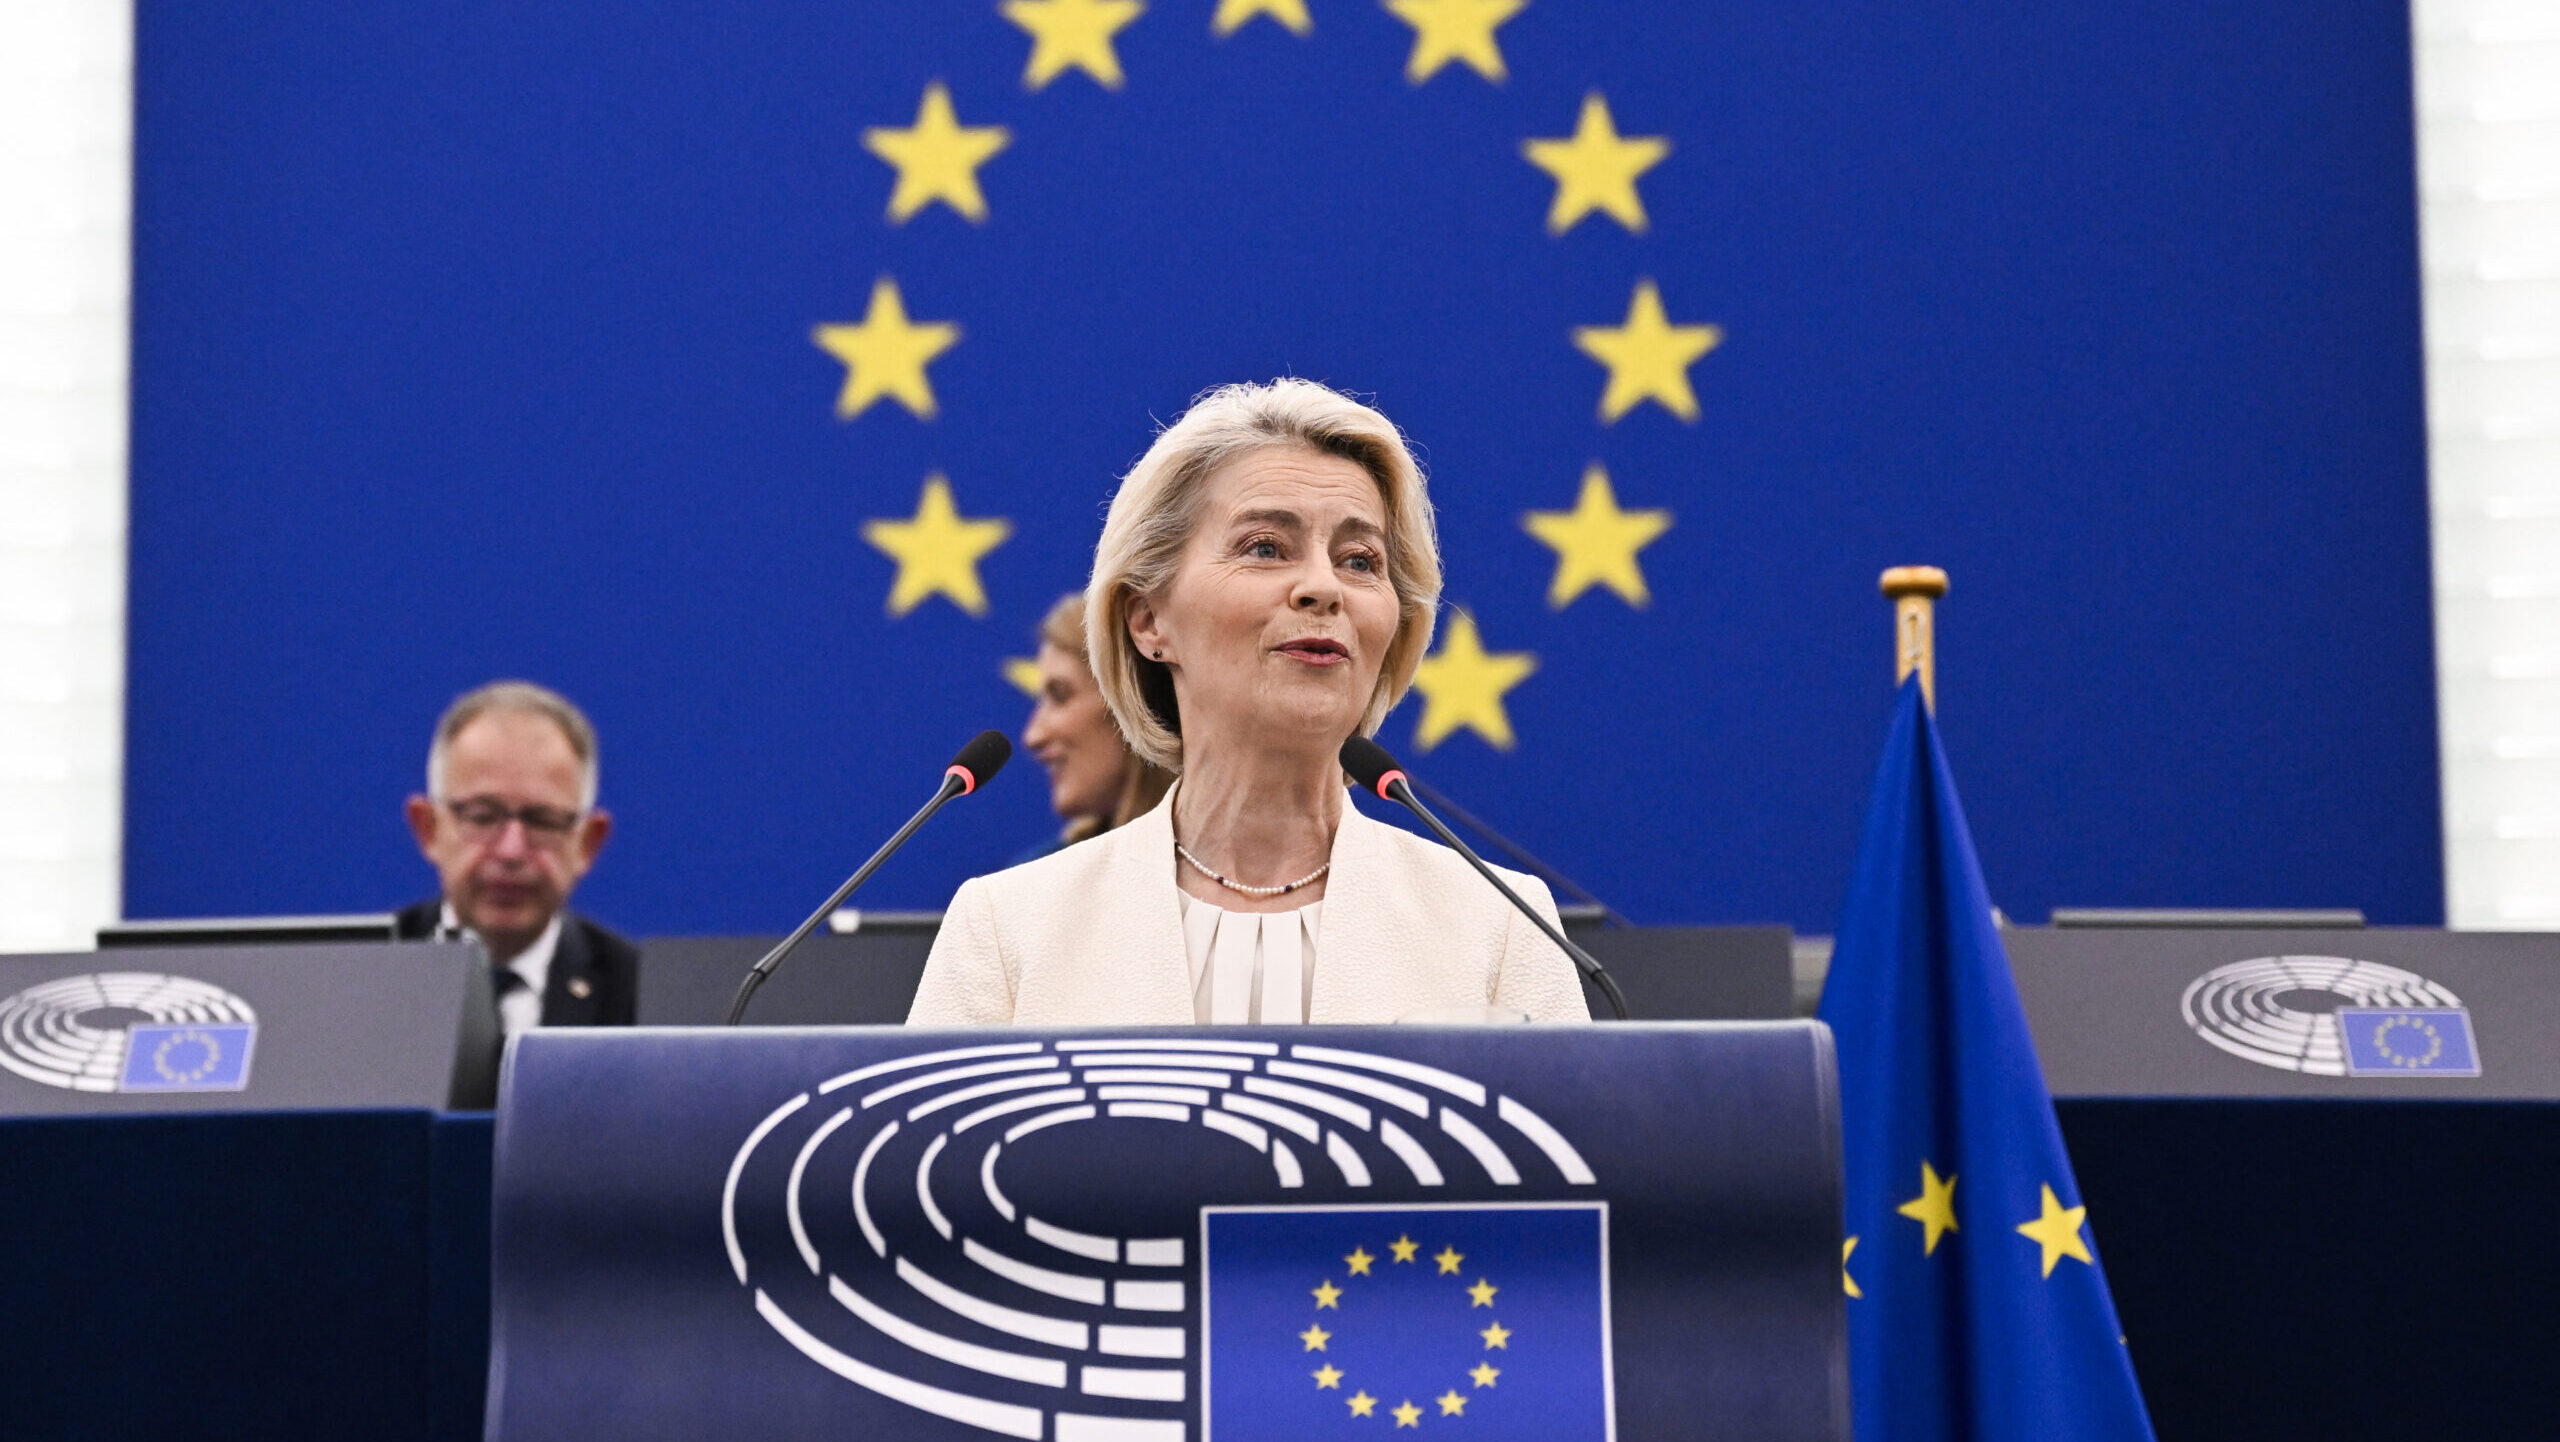
On September 16, 2026, European Commission President Ursula von der Leyen proposed a new emergency mechanism for EU member states to respond to rising security threats, including cyberattacks and sabotage. This mechanism would allow any member state to convene all EU governments to coordinate responses to incidents that threaten national security but do not constitute armed aggression. Recent incidents in Denmark, Lithuania, and Poland, as well as drone incursions, prompted this initiative. The proposed protocol is modeled after NATO's Article 4, which facilitates consultations among member states under threat. Von der Leyen emphasized the need for a more agile response framework, as existing EU mechanisms were deemed insufficient for the current threat landscape. The proposal is still in development, with questions remaining about decision-making authority and response protocols. The urgency of this proposal reflects a significant increase in hybrid threats across Europe, including cyberattacks targeting critical infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab Vulnerabilities Exploited Within Hours of Disclosure On September 10, 2026, GitLab released patches for critical vulnerabilities CVE-2026-85706 and CVE-2026-87719. CVE-2026-85706, a path traversal flaw, allows unauthenticated users to read arbitrary files from GitLab servers, while CVE-2026-87719 enables credential theft via insecure deserialization. Both…