 Theguardian
EU Rejects Putin's Proposal for Schröder as Mediator in Ukraine Talks
Article Content

- •The EU rejected Putin's proposal for Gerhard Schröder as a mediator in Ukraine talks.
- •Kaja Kallas emphasized that Schröder's past ties to Russia disqualify him as an impartial negotiator.
- •Ongoing conflict dynamics suggest a diplomatic resolution is unlikely in the near future.
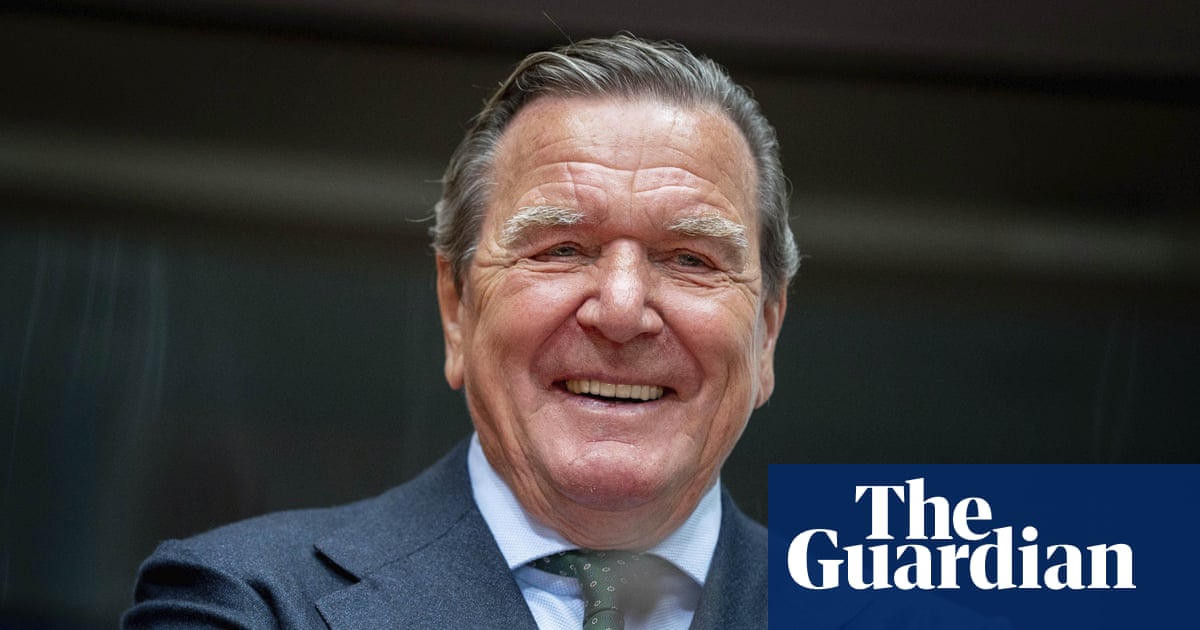
The EU has dismissed Vladimir Putin's suggestion to appoint former German Chancellor Gerhard Schröder as a mediator in Ukraine peace talks. Kaja Kallas, the EU's top diplomat, stated that allowing Russia to choose a negotiator would be unwise, highlighting Schröder's past ties to Russian energy companies. Schröder, who has been criticized for his close relationship with Putin, has not condemned Russia's invasion of Ukraine. This proposal comes amid ongoing conflict dynamics, with both Ukrainian and Russian forces experiencing heavy casualties. Analysts suggest that a diplomatic breakthrough remains unlikely given the current battlefield conditions and Russia's insistence on preconditions for negotiations. Germany's defense minister expressed skepticism about Putin's intentions, suggesting they may be part of a deceptive strategy. The situation continues to evolve as both sides remain entrenched in their positions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…