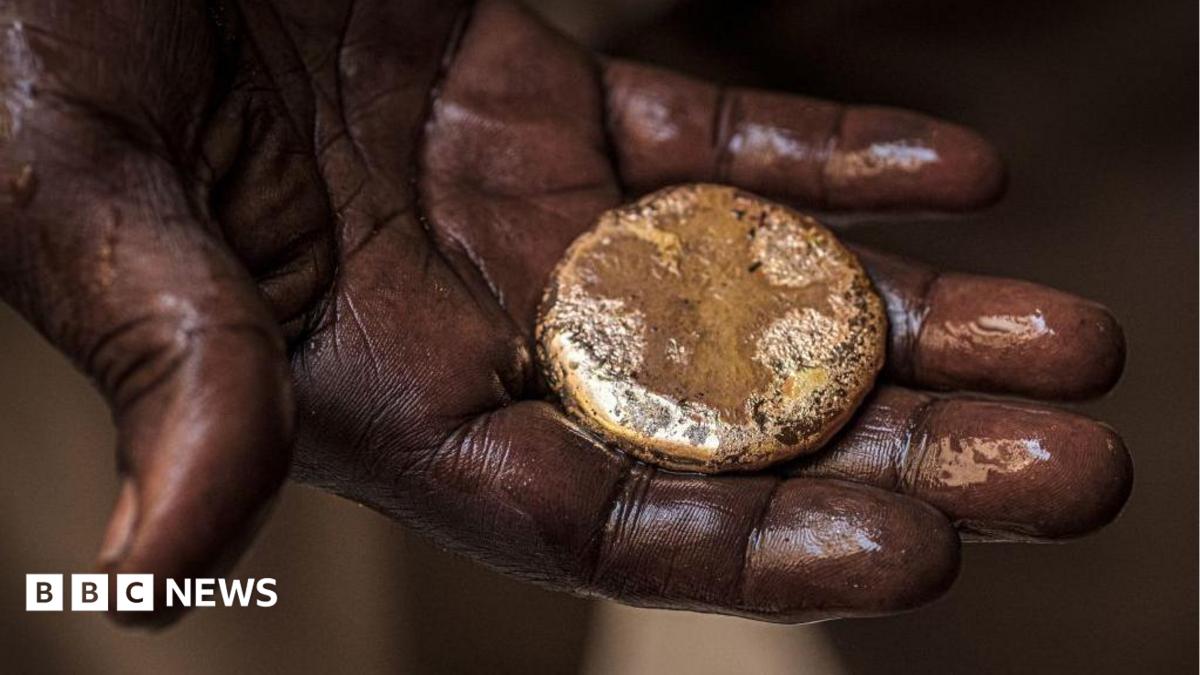 www.bbc.co.uk
EU Sanctions Target Sudan's Gold Trade Amid Ongoing Civil War
Article Content

- •EU sanctions ban Sudanese gold imports to curb war financing.
- •The civil war has displaced over 14 million people since April 2023.
- •Gold smuggling complicates the effectiveness of the sanctions.
On October 3, 2026, the European Union announced a ban on the purchase and import of gold from Sudan, citing its role as a key financing source for the ongoing civil war that began in April 2023. The conflict, primarily between the Sudanese Armed Forces and the Rapid Support Forces, has led to a humanitarian crisis, displacing over 14 million people. The sanctions also include a prohibition on exporting mercury and cyanide, chemicals used in gold mining. Rights groups report that a significant portion of Sudan's gold, estimated between 50% to 70%, is smuggled out of the country, complicating the effectiveness of the sanctions. The RSF controls most goldfields, while the Sudanese army oversees production in other regions. The EU's sanctions aim to disrupt the financial networks sustaining the conflict, although previous sanctions targeting individuals have had limited impact. The situation remains dire, with ongoing violence and humanitarian needs escalating.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What are the main sanctions imposed?
How has the conflict affected civilians?
What challenges do the sanctions face?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…