 dx.doi.org
Evaluation of Lightweight and Federated Learning Models for IIoT Intrusion Detection
Article Content

- •Lightweight models for IIoT IDS show overfitting risks when evaluated on unseen networks.
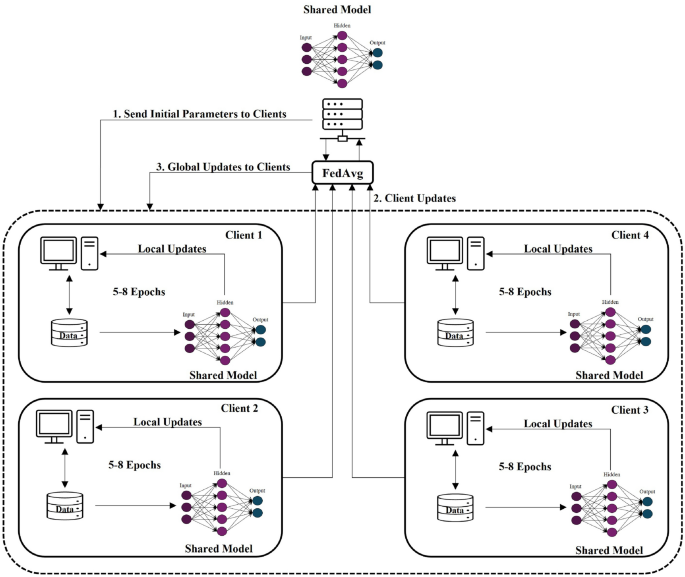
- •Federated learning models can achieve high accuracy but struggle with generalization across datasets.
- •Cross-network evaluation is essential for assessing the deployment readiness of intrusion detection systems.
Recent studies published on July 2, 2026, focus on the effectiveness of lightweight machine learning models and federated learning in intrusion detection systems (IDS) for Industrial Internet of Things (IIoT) networks. Article 1 highlights that existing models often overfit to training datasets, leading to unverified performance on unseen networks. It emphasizes the need for cross-network evaluation under realistic class distributions. Article 2 discusses federated learning approaches that address privacy concerns but also face challenges in generalization across diverse datasets. Both studies reveal that models trained on specific datasets may not perform well in different environments, with significant performance degradation observed in cross-dataset evaluations. The findings suggest a need for improved training strategies that encompass diverse attack scenarios and environments to enhance the robustness of IDS in IIoT settings.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (27)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…