 ransomnews.com
Exploit.in Forum's Role in Ransomware Evolution
Article Content

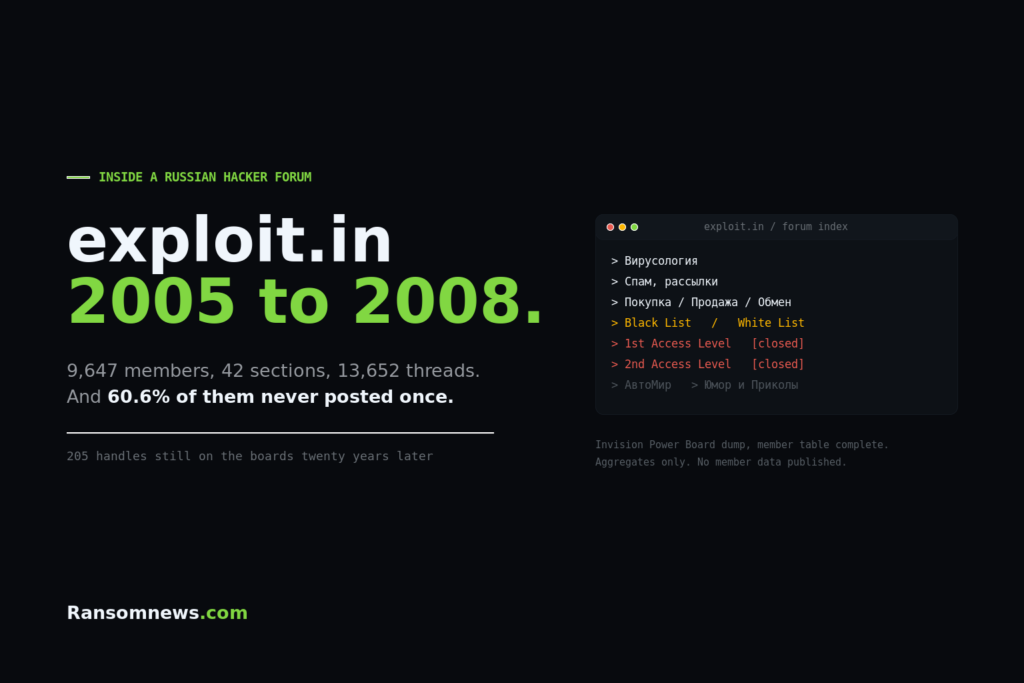
- •Exploit.in has 9,647 members and 80,891 posts, revealing a rich history of cybercrime.
- •The forum's structure and culture have influenced the development of ransomware-as-a-service (RaaS).
- •Many early users are still active, indicating a long-standing community in cybercrime.
The Exploit.in forum, active since 2005, has been analyzed through a database dump revealing its influence on the modern ransomware ecosystem. The database includes 9,647 registered members, 13,925 threads, and 80,891 posts, showcasing a blend of cybercrime discussions and casual topics. Many users from the early days are still active, indicating a continuity in the cybercrime culture. The forum's structure included sections for malware analysis, carding, and general chat, reflecting a community that combined technical discussions with social interactions. The findings suggest that the practices established in the early years have directly influenced today's ransomware-as-a-service (RaaS) model, where affiliates rent ransomware to execute attacks. This model has allowed ransomware to scale significantly, making it a prevalent threat in 2026. The analysis highlights the resilience of the cybercrime ecosystem, as shutting down forums may not significantly impact operations due to the adaptability of users. The current status of the forum remains active, continuing to serve as a hub for cybercriminal activities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical Code Injection Vulnerability in Staggs Plugin for WordPress A critical code injection vulnerability, CVE-2026-78287, has been identified in the Staggs plugin for WordPress, affecting versions up to 3.3.0. This flaw allows unauthenticated attackers to execute arbitrary code remotely, posing severe risks to affected sites. The vulnerability stems from improper control over code…