 Wiz
Exposed GitHub PATs Enable Cloud Environment Breaches
Article Content
Browse articles 
Threat actors are exploiting exposed GitHub Personal Access Tokens (PATs) to gain unauthorized access to cloud environments. The Wiz Customer Incident Response Team reported that these compromised tokens allow attackers to bypass security measures and access sensitive GitHub Action Secrets. This incident highlights a significant vulnerability in the trust placed in GitHub's security features.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track Shai-hulud and Azure in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
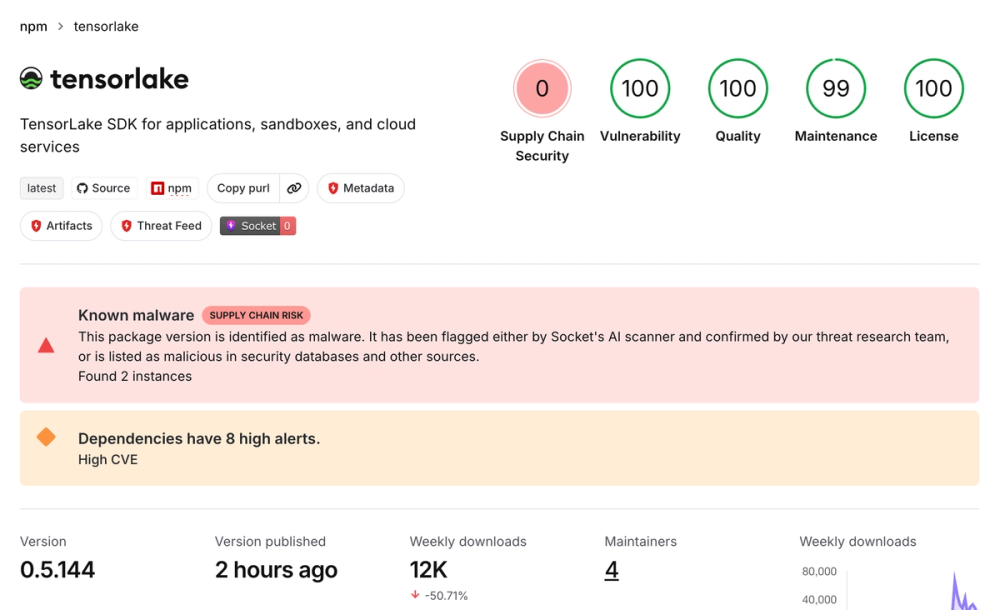 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Cisco Email Bug Exploited as Zero-Day by Unknown Actors A zero-day vulnerability in Cisco's email system has been by unknown criminals. The flaw, described as a 'make-me-root' bug, allows attackers to gain root access via email. Cisco has not disclosed specific details about the vulnerability or the affected systems. The exploit is reportedly being used in the wild…