 Interestingengineering
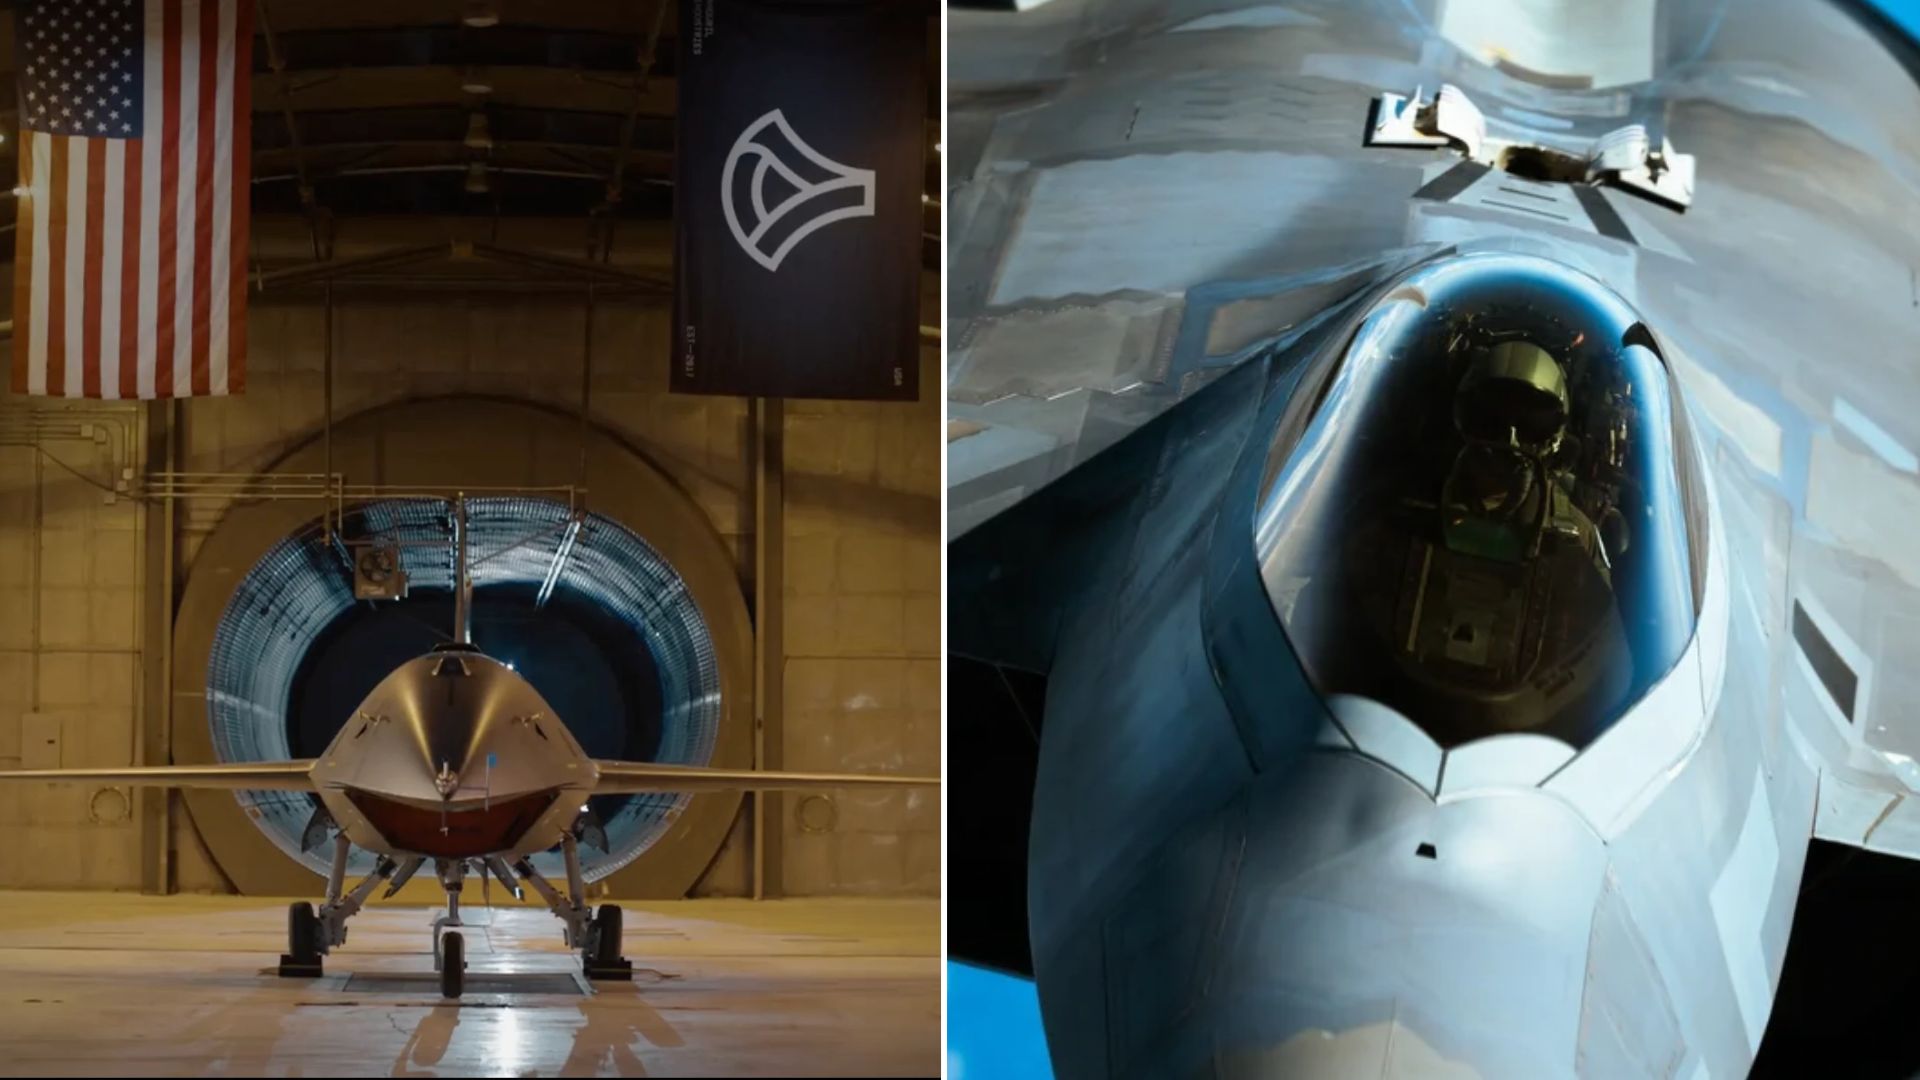
F-22 Pilot Commands Fury Drone in Historic Test
Article Content

- •F-22 pilot commanded a YFQ-44A Fury drone for the first time in mid-October 2026.
- •The test demonstrated the potential for crewed fighters to direct multiple autonomous drones.
- •The Air Force aims to have a fleet of 500 Collaborative Combat Aircraft by 2032.
An F-22 Raptor pilot successfully commanded a YFQ-44A Fury drone during a flight demonstration, marking a significant advancement in the U.S. Air Force's Collaborative Combat Aircraft program. The test, conducted earlier in October 2026, involved the pilot issuing high-level tactical directives that the drone's autonomy software executed in real-time. This capability aims to enhance the operational effectiveness of crewed fighters by allowing them to direct multiple uncrewed aircraft. The demonstration took place at Edwards Air Force Base in California, with the F-22 and Fury taking off together and joining midair. The Air Force and Anduril, the drone's manufacturer, have not disclosed specific details about the cockpit configuration used for this test. The goal is to integrate these systems further, with plans for a fleet of at least 500 CCAs by 2032. Previous tests have shown the Fury's ability to launch missiles, indicating its combat readiness.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was demonstrated during the test?
What are the future plans for CCAs?
Who conducted the test?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…