 www.dw.com
Russian Disinformation Campaign Targets German Elections
Article Content

- •A disinformation campaign targeting German election candidates has been identified.
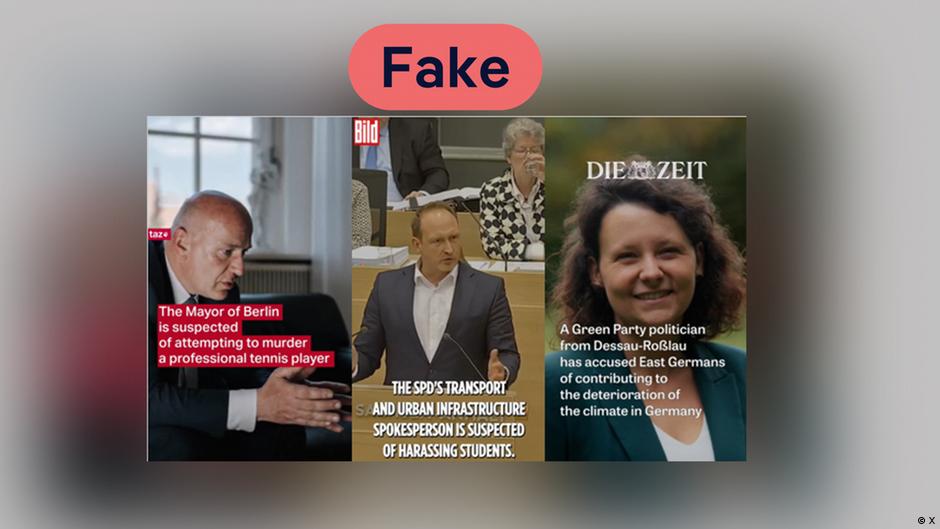
- •Eric Stehr is a primary target, facing false allegations of murder and misconduct.
- •The Matrjoschka operation has produced over 180 fake posts since June 2026.
In the lead-up to the September 2026 elections in Germany, a disinformation campaign has emerged, primarily targeting candidates like Eric Stehr from the Left Party. Fake videos and posts allege serious crimes against Stehr, including murder and organizing illicit parties, falsely attributing these claims to major German media outlets. The campaign is part of a larger Russian influence operation known as Matrjoschka, which has been active since September 2023. Over 180 fake posts have been identified across social media platforms such as X, Bluesky, and TikTok. The operation aims to discredit candidates in key regional elections, including those in Sachsen-Anhalt and Berlin. Authorities have confirmed that there are no investigations against Stehr, and the claims are entirely fabricated. The campaign's scale and targeted nature raise concerns about the integrity of the upcoming elections.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track X in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…