 Esecurityplanet
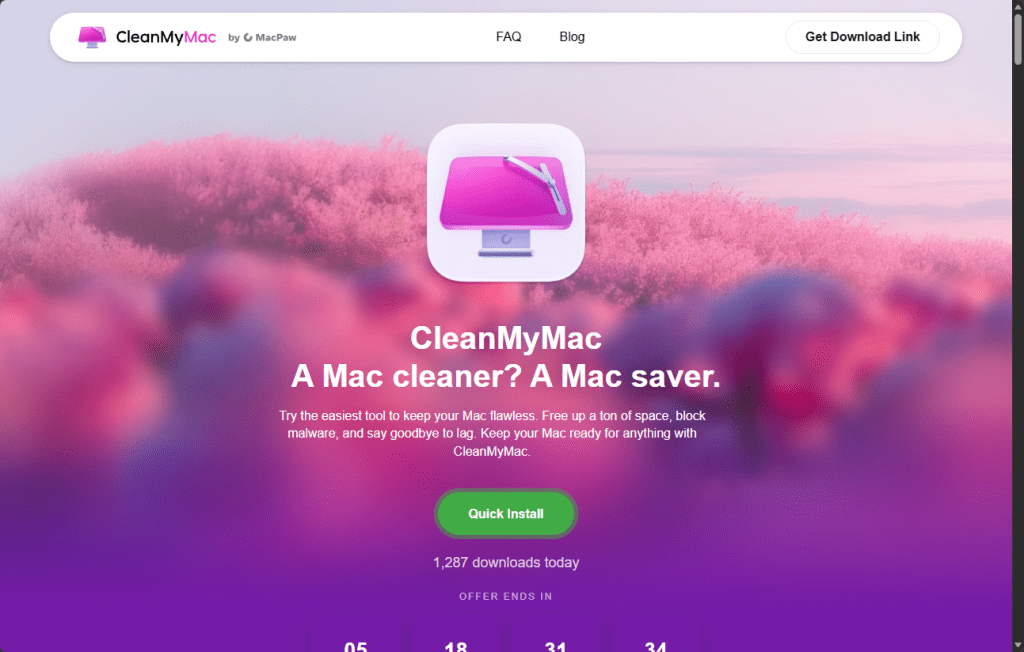
Fake CleanMyMac Site Distributes SHub Stealer to Target Crypto Wallets
Article Content
Browse articles 
A fraudulent CleanMyMac website is deceiving macOS users into downloading SHub Stealer malware, which is designed to steal credentials and crypto wallet information. This campaign specifically targets Apple users, posing a significant risk to their sensitive financial data.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
Timeline
2026-03-09
Reports of fake CleanMyMac site distributing SHub Stealer emerge
More articles in this cluster (6)
Following this threat?
Track SHub in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…