 Calgary.Citynews.Ca
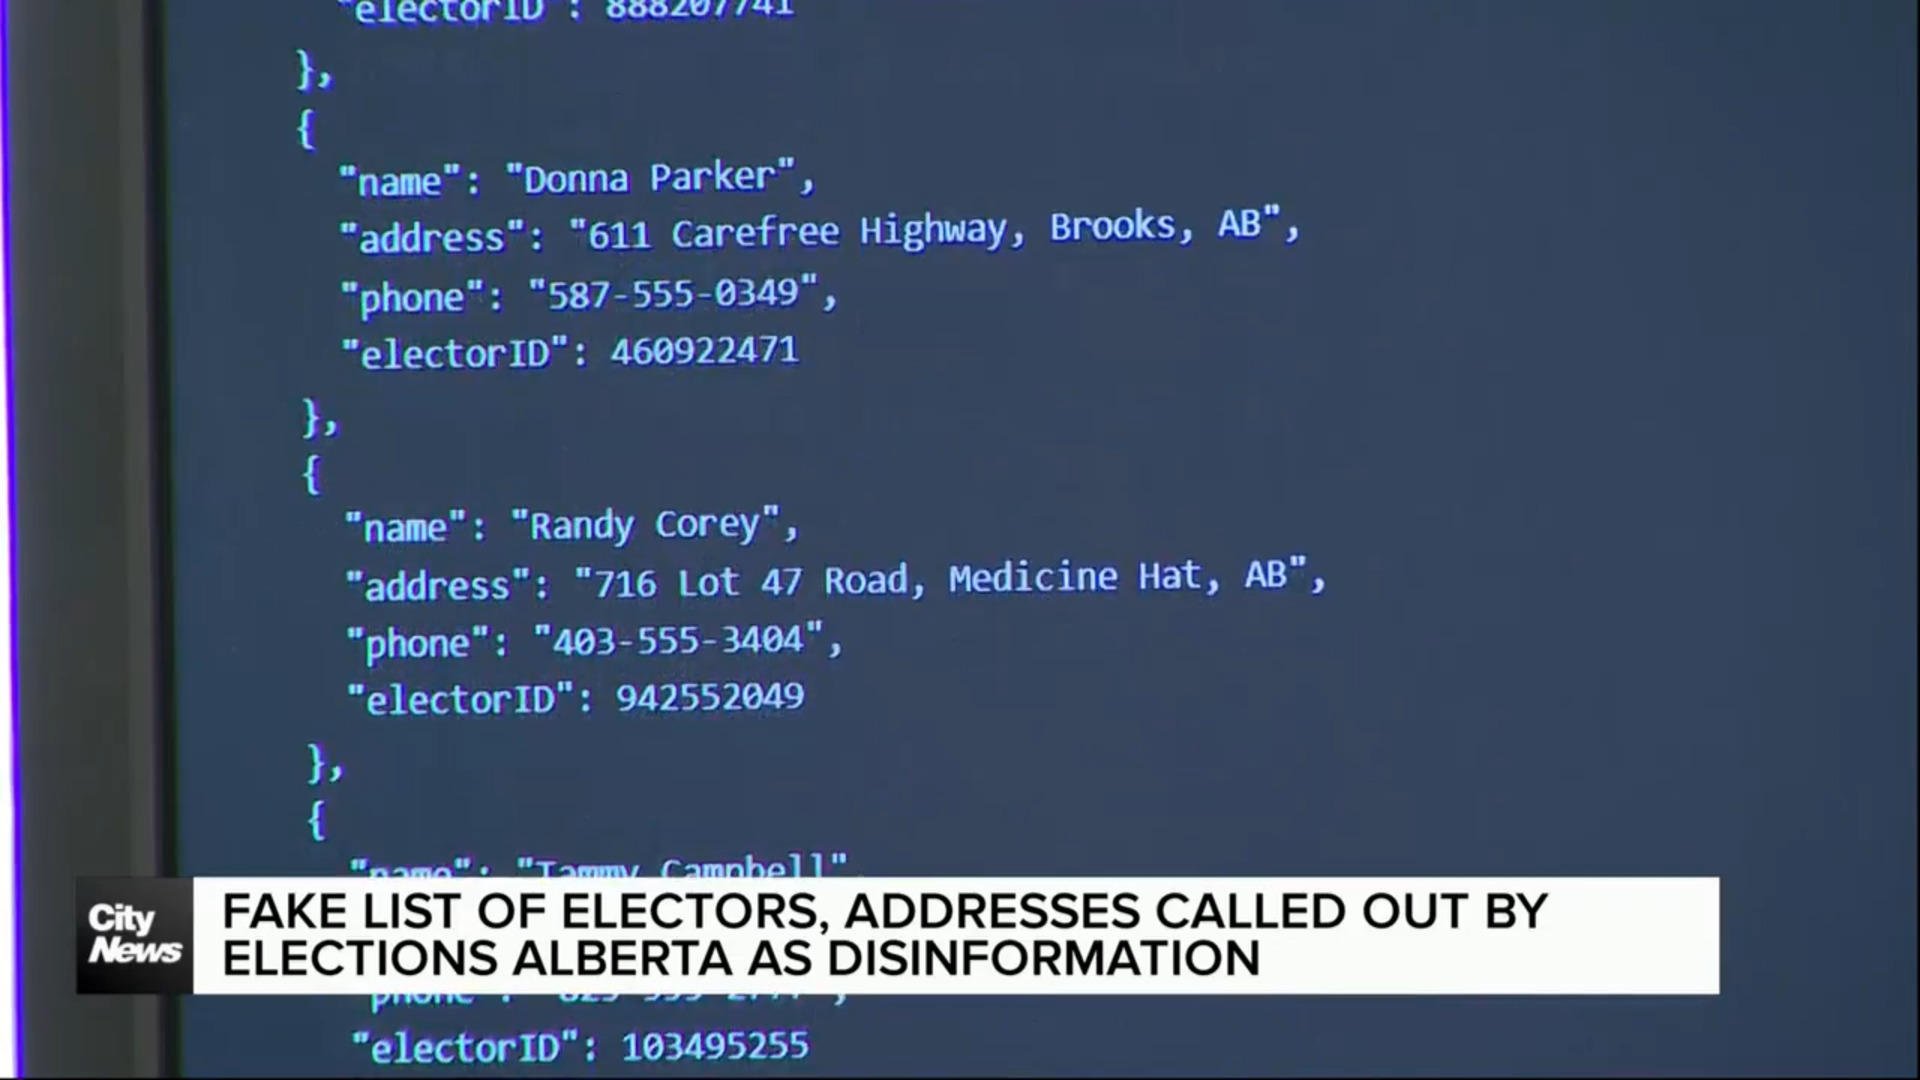
Elections Alberta Warns of Disinformation Campaign Targeting Elector List
Article Content
Browse articles 
- •Elections Alberta has flagged a fake elector list as disinformation.
- •The disinformation campaign aims to discredit the electoral system.
- •Public urged to verify information from official sources.
Elections Alberta has identified a fake list of electors circulating online, which it claims is part of a disinformation campaign aimed at undermining the electoral process. The agency has not specified the exact method of distribution but emphasizes the importance of verifying information from official sources. This incident raises concerns about the integrity of the electoral system, especially as it coincides with upcoming elections. No specific vulnerabilities or technical details have been disclosed regarding the spread of this disinformation. The agency urges the public to report any suspicious communications related to the electoral process.
Ask AI about this cluster
Answers cite the sources they use
Updated 9d ago How this analysis works
Timeline
2026-07-09
Elections Alberta issues warning
Elections Alberta publicly called out a fake list of electors, urging the public to verify electoral information.
Edmonton.Citynews.CaMore articles in this cluster (2)
Common questions
What is the nature of the disinformation?
A fake list of electors is being circulated online, which may mislead voters.
How should the public respond?
Elections Alberta advises the public to verify any electoral information through official channels.
Is there any technical detail on how this is spread?
No specific details on the distribution method of the disinformation have been provided.
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…