 Dubaieye1038
Iranian Drone Attack Targets UAE's Barakah Nuclear Power Plant
Article Content

- •Iranian drones attacked Barakah Nuclear Power Plant in May 2026, hitting external infrastructure.
- •FANR's Director-General commended response teams for their effective emergency preparedness.
- •FANR maintains a strong regulatory presence at Barakah to ensure safety and compliance.
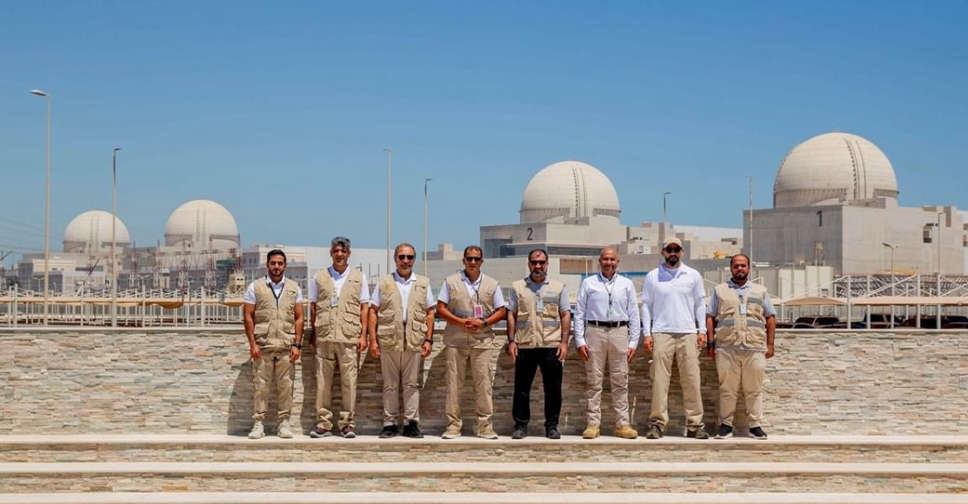
On May 2026, Iranian drones targeted the Barakah Nuclear Power Plant, hitting electrical infrastructure outside its inner perimeter. This attack, described as a violation of international law, prompted an immediate response from the Federal Authority for Nuclear Regulation (FANR). Following the incident, FANR's Director-General, Hamad Al Kaabi, visited the facility to assess operations and safety measures. He praised the response teams for their professionalism and coordination in maintaining safety and security. The plant's four operational units are currently undergoing scheduled maintenance and refueling. FANR continues to enforce a robust regulatory oversight to ensure compliance with safety and security standards. The incident highlighted the resilience of the UAE's nuclear regulatory systems and the importance of ongoing vigilance in the face of external threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Barakah Nuclear Power Plant in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…