 Hackread
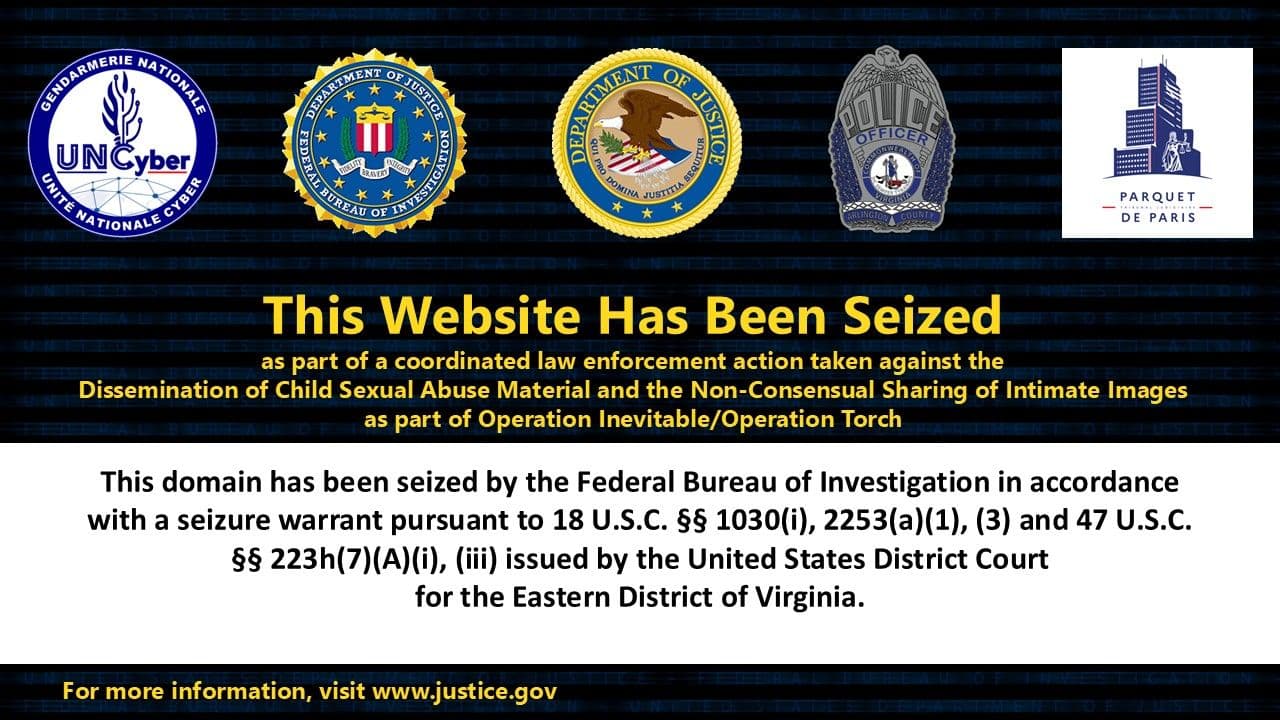
FBI and French Authorities Seize Deepfake CSAM Websites
Article Content

- •Two websites seized for distributing CSAM and deepfake media.
- •Over 17,000 victims identified, including minors.
- •Authorities arrested the suspected administrator and seized significant cryptocurrency.
The FBI and French authorities have seized two websites, NudeLeaksTeens and NLTVIDS, used for distributing child sexual exploitation material, including AI-generated deepfake media. The operation led to the arrest of a 25-year-old French man, suspected of being the main administrator, and his brother. The sites reportedly contained explicit images and videos of over 17,000 victims, including minors, sourced from hacked social media accounts. Law enforcement discovered that the sites operated with a form of currency for transactions and included collections of material organized by victim. The seizure is part of a broader effort to dismantle networks exploiting victims through anonymous online platforms. Authorities have urged victims to come forward and are investigating the financial transactions linked to the sites, including the seizure of €700,000 in cryptocurrency. The operation highlights the ongoing challenge of combating online exploitation and the use of deepfake technology in these crimes.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track FBI Washington Field Office in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of content were shared on the seized websites?
How many victims were affected by these websites?
What actions are being taken against the operators?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…