 Jalopnik
Flock Cameras Exposed to Hacking and Privacy Risks
Article Content

- •Flock cameras are vulnerable to hacking, allowing access to live and archived footage.
- •The hacking group stegan0gram exposed serious security flaws, including unencrypted data access.
- •Public protests against Flock cameras highlight growing concerns over privacy and data control.
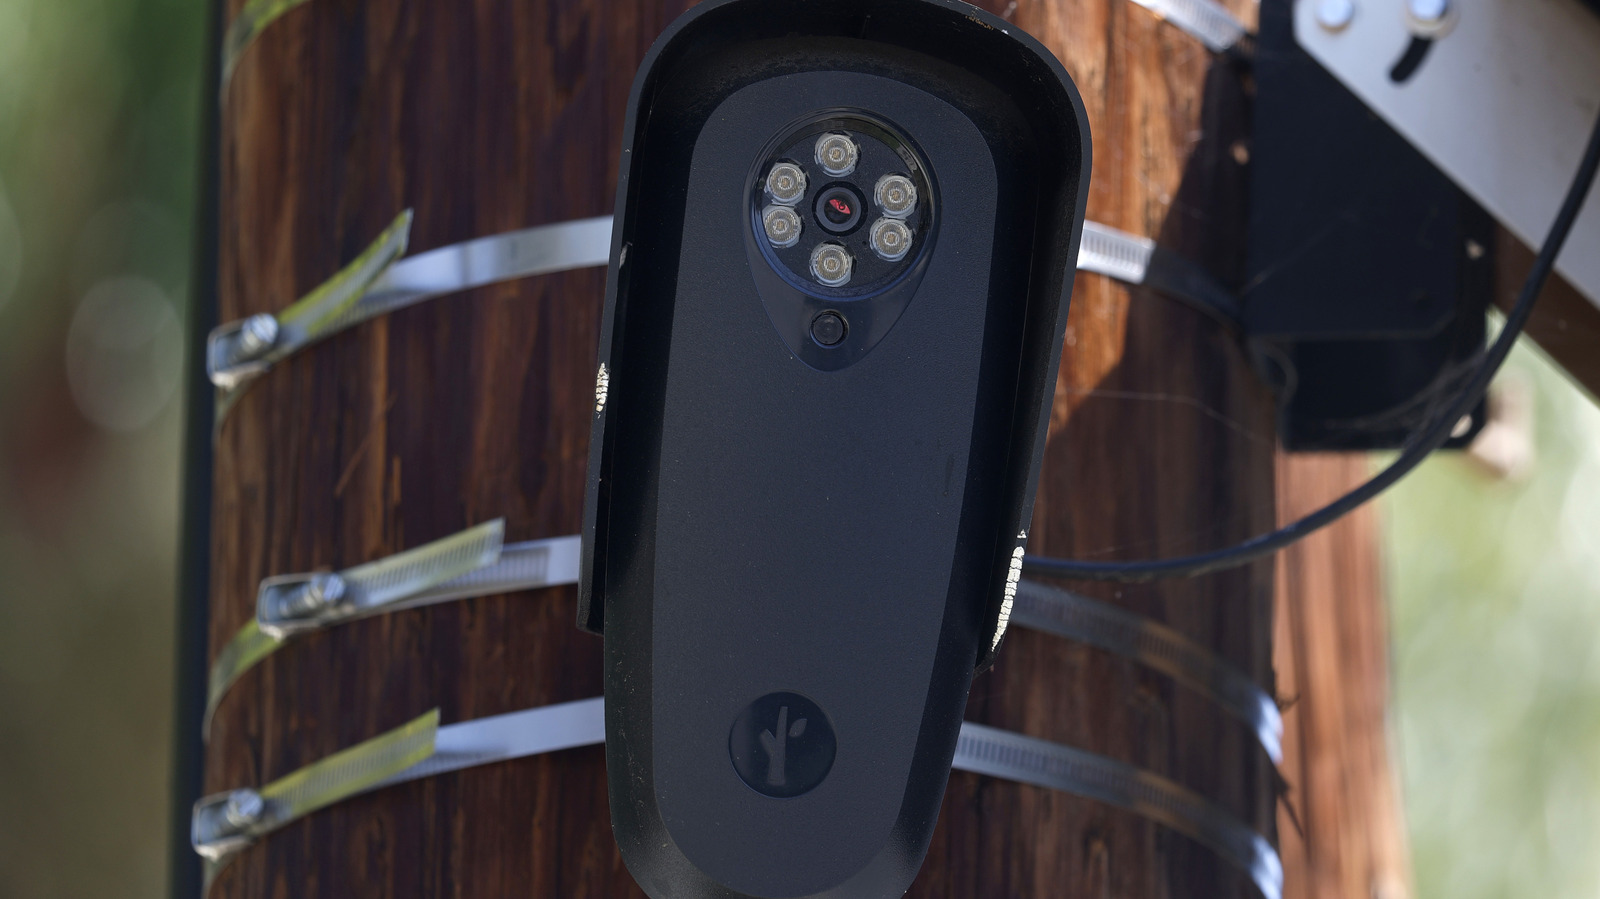
Recent investigations reveal significant vulnerabilities in Flock camera systems, with hackers demonstrating the ease of accessing live and archived footage. A hacking group, stegan0gram, successfully reverse-engineered a Flock camera, exposing unencrypted data and an encryption key that could unlock sensitive information about over 50,000 vehicles. This incident highlights the broader risks associated with automatic license plate readers (ALPRs), which are marketed as benign but collect extensive data beyond just license plates. Cybersecurity expert Noah Williams warns that police departments using these systems effectively rent access to data they do not control, raising privacy concerns. Flock cameras have faced public backlash, with protests and calls for their removal in various communities. The vulnerabilities found could lead to unauthorized surveillance and misuse of personal data.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Axon in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data can Flock cameras access?
How vulnerable are Flock cameras to hacking?
What are the privacy concerns related to Flock cameras?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…