 Aol
Former Detective Reveals Home Security Vulnerabilities
Article Content
Browse articles 
- •41% of Brits don't know how many house key copies exist.
- •20% have never changed their locks despite key access concerns.
- •Many homeowners underestimate the ease of burglary.
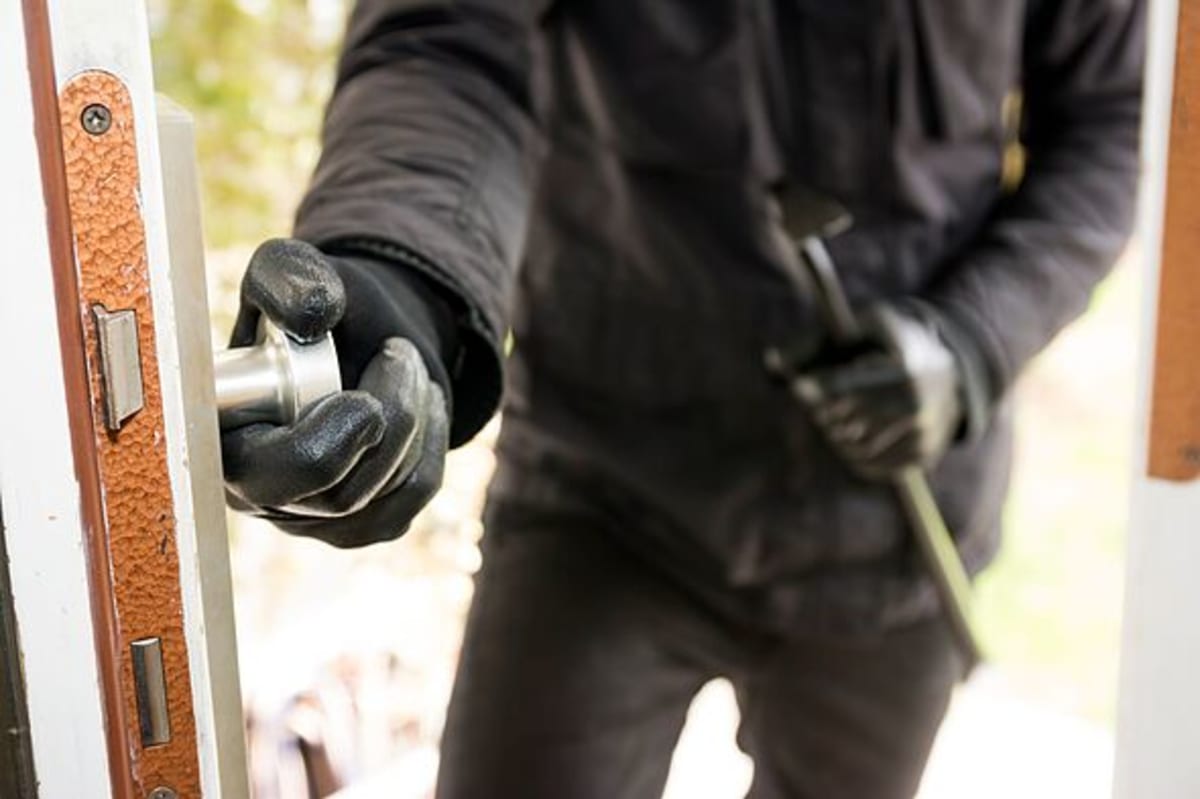
Peter Bleksley, a former Scotland Yard detective, highlights how common mistakes make British homes vulnerable to burglary. A study commissioned by security firm Ultion found that 41% of homeowners are unaware of how many copies of their keys exist. Alarmingly, 20% have never changed their locks despite concerns about key access. The findings are part of Ultion's campaign to raise awareness about home security risks, revealing that many homeowners underestimate the ease with which burglars can gain entry. The study shows a significant lack of awareness regarding key distribution and lock security among the British public.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
More articles in this cluster (2)
Common questions
What are the key vulnerabilities identified?
The main vulnerabilities include lack of awareness about key copies and failure to change locks.
What percentage of homeowners have never changed their locks?
20% of homeowners reported they have never changed their front door locks.
Who conducted the study on home security?
The study was commissioned by the security firm Ultion.
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…