 Hellorayo
Former Teacher Jailed for Child Exploitation Using Deepfakes and Upskirting
Article Content

- •Abusali Rahman was jailed for six years for 21 child sex offences.
- •He created sexualised deepfake images and took covert upskirting photographs of pupils.
- •The case highlights the misuse of technology in child exploitation.
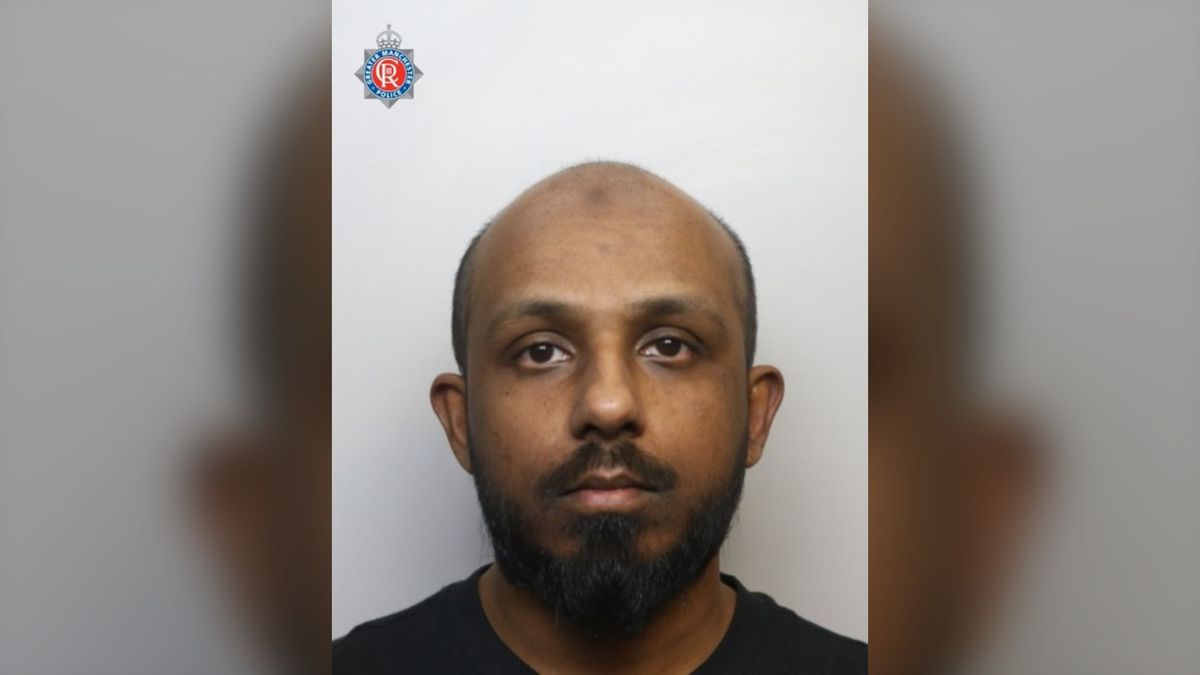
Abusali Rahman, a 37-year-old former supply teacher, was sentenced to six years in prison for 21 child sex offences, including creating sexualised deepfake images and taking upskirting photographs of pupils. The Crown Prosecution Service reported that Rahman misused his position to gather personal information about students, which he used to find and exploit them on social media. His offences included generating AI images of children in sexual contexts and covertly photographing them without consent. The investigation began after parents reported concerning social media accounts on March 2, 2025. Rahman's devices contained numerous deepfake images and upskirting photos, some of which were shared online. He was also placed under a 20-year Sexual Harm Prevention Order to prevent future offences. Rahman pleaded guilty on May 28, 2026, after initially remaining silent during police questioning.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific offences did Rahman commit?
What measures are in place to prevent future offences?
What prompted the police investigation?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…